
 Do Son
While India faces a surge in these pig-butchering scams, the phenomenon is not confined by geography. Similar tactics have been deployed in Taiwan
Cyber Security

NarniaRAT boasts information-stealing capabilities and swiftly conscripts the compromised machine into the Fenix Botnet.

The fallout from the devastating hacker attack on IT provider Xplain continues as the NCSC publishes a detailed report on the leaked data
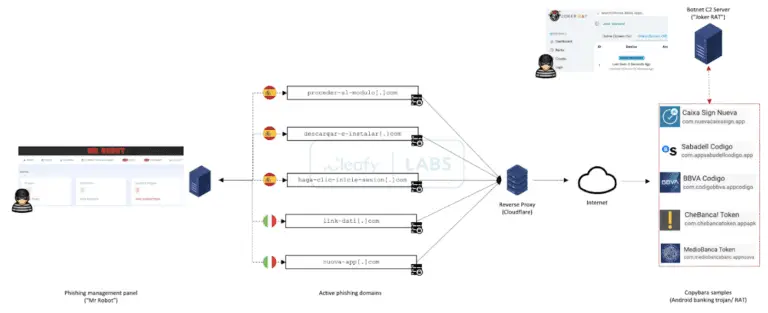
Copybara campaign unfolds in a series of meticulously executed stages. TAs are weaponizing a combination of social engineering, phishing infrastructure

TA4903 cybercriminal group has displayed a consistent pattern of sophisticated phishing tactics in pursuit of sensitive corporate data

Cado Security Labs' recent discovery exposed a complex malware campaign zeroing in on Linux servers misconfigured with popular cloud services

GhostSec aims to fund further operations, leveraging a variety of tactics from ransomware to DoS attacks to achieve their objectives.

CISA has added a critical Windows Kernel vulnerability (CVE-2024-21338) to its Known Exploited Vulnerabilities catalog

Fully Undetectable links are transforming the way cybercriminals execute phishing campaigns, malware distribution, and other nefarious schemes

TA577, a prolific cybercrime group responsible for past Qbot campaigns and associated with Black Basta ransomware attacks

Russia's NoName057(16) has become synonymous with the DDoSia project, a relentless campaign of DDoS attacks that target nations supporting Ukraine
Dubbed "Morris II," this zero-click worm exploits adversarial self-replicating prompts to spread across interconnected GenAI-powered apps

Security researchers from NVISO have uncovered two sophisticated TLS-based backdoors, dubbed SparkCockpit and SparkTar

Security experts are currently tracking a sophisticated phishing scheme aimed squarely at entrepreneurs operating within Telegram communities

These actors, identified as UNC1549 and overlapping with the Tortoiseshell group, are a force to be reckoned with

This attack, attributed to the infamous Lazarus hacking group, leverages a dangerous tactic: preying on developers' typos to install malware

Central to the Spiked Wine threat actor campaign is WINELOADER, a modular backdoor engineered with evasion and stealth in mind

Cyble Research and Intelligence Labs has uncovered a sophisticated phishing campaign actively exploiting ConnectWise ScreenConnect
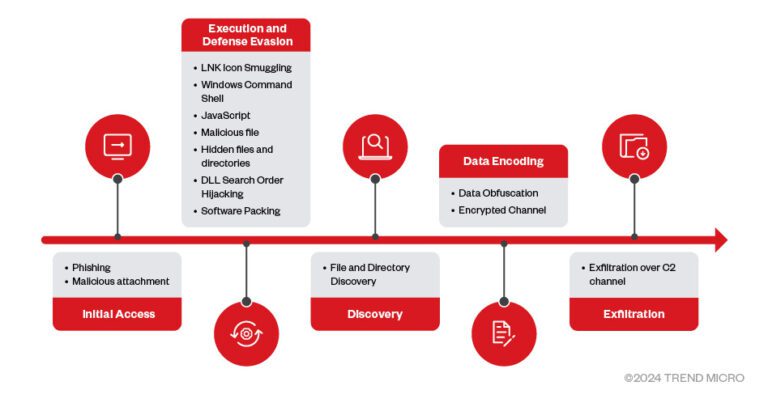
A startling revelation linked Earth Lusca to a Chinese entity known as I-Soon, unmasked through a breach of private documents

The infamous PlugX RAT, used by various threat actors, frequently leverages DLL side-loading to evade detection

This campaign, attributed to the Russia-aligned Doppelgänger network, focused on anti-Ukrainian content but has expanded to target audiences

The campaign investigated demonstrates Turla's focus on targeted attacks. This 'Pelmeni Wrapper' loads the next stage payload.