
 Do Son
A new report reveals Subtle Snail, an Iran-nexus group, is using fake LinkedIn jobs to deliver a custom backdoor for espionage against European telecom and defense firms.
Cyber Security

A new report reveals that a Russian influence network, CopyCop, has created over 200 new AI-powered fake media sites to spread propaganda and deepfakes globally.
Group-IB reports on MuddyWater, an Iranian APT, shifting tactics from RMM tools to custom malware and spearphishing, using new backdoors like Phoenix.

A new report reveals a surge in coordinated hacktivist attacks on India's critical infrastructure. Groups from Pakistan, Russia, and others are launching breaches and DDoS attacks.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.
A new APT28 campaign targets Ukraine's military with a blend of steganography, open-source tools, and legitimate cloud services for covert C2.

North Korean threat group Kimsuky is using AI-generated deepfakes in a new spear-phishing campaign, signaling a new frontier in cyber warfare.

The FBI has issued a FLASH Alert warning about UNC6040 and UNC6395, two groups actively compromising Salesforce via vishing and malicious OAuth apps to steal data.

IBM X-Force reveals new findings on Hive0154, a China-aligned threat actor using an upgraded Toneshell backdoor and a new USB worm to target organizations.

A new report reveals a Chinese APT group compromised a Philippine military company with a fileless malware framework called EggStreme, which uses DLL sideloading for stealth.

A new report reveals a ToneShell backdoor from Mustang Panda. The malware targets Myanmar and uses anti-analysis tricks to evade detection.

The Lazarus Group is using a new campaign to steal crypto by exploiting a vulnerability (CVE-2025-48384) with fake interviews and poisoned code repositories.
A new report uncovers 45 previously unknown domains linked to the Chinese APT group Salt Typhoon. The findings reveal a long-term, multi-year espionage infrastructure.

A new report reveals Noisy Bear, an APT group targeting Kazakhstan’s oil and gas sector with spear-phishing and multi-stage malware, mimicking internal communications.

A new report reveals that the North Korean Kimsuky APT is using social engineering on Facebook and Telegram to deliver AppleSeed malware to targets in South Korea.

A new report reveals a Lazarus Group subgroup is using a tiered arsenal of custom RATs—PondRAT, ThemeForestRAT, and RemotePE—to target the financial and crypto sectors.
A new report reveals North Korea's APT-37 is using malicious LNK files in a campaign, "Operation HanKook Phantom," to spy on South Korean government and research.

An Iranian-aligned group abused a compromised Omani Foreign Ministry mailbox to send spear-phishing emails to diplomats and international organizations in a global campaign.
A new CNA report reveals how private Russian cybersecurity firms, including Kaspersky and Positive Technologies, are deeply entwined with the Kremlin's cyber operations.

A new report reveals the TAOTH cyber-espionage campaign, which hijacks software updates and uses spear-phishing to deliver malware to high-value targets in Asia.

The NSA, CISA, and partners have released a joint advisory exposing how Chinese APT groups are compromising telecom and government networks for global espionage.
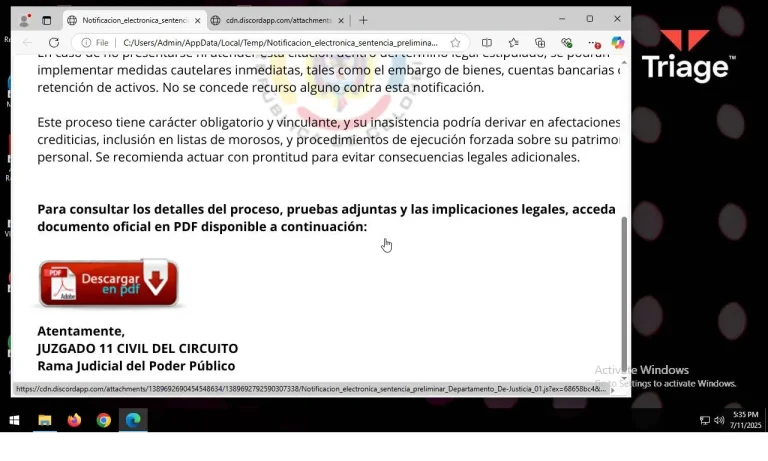
A new report reveals the Blind Eagle hacking group is using spearphishing and commodity RATs to conduct cyber espionage against Colombian government and private sector targets.