
 Do Son
Amidst India-Pakistan tensions, Bitter APT launched a spear phishing campaign against Pakistan Telecommunication Company, using WmRAT for espionage.
Cyber Security

ConnectWise disclosed a targeted cyber intrusion by a sophisticated nation-state actor affecting a small subset of ScreenConnect customers. Enhanced monitoring is in place.

APT41 is exploiting Google Calendar as a covert C2 channel in the TOUGHPROGRESS cyberespionage campaign, targeting government entities with stealthy malware.

Threat actor UTG-Q-015 is escalating operations, using 0-days and watering hole attacks against government, finance, and AI in Asia.

New campaigns by Silent Werewolf leverage custom C# loaders and advanced delivery to target entities in Russia and Moldova for cyber-espionage.

Microsoft identified Void Blizzard, a new Russia-affiliated cyberespionage group, targeting critical sectors in NATO countries and Ukraine.

Earth Lamia, a China-linked APT, is targeting critical industries worldwide using SQL injection, CVEs, and custom backdoors like PULSEPACK.

TA-ShadowCricket (formerly Shadow Force), a China-linked group, has been active for over a decade, targeting Asia-Pacific government and enterprise networks.

Russian-aligned TAG-110 (APT28) is launching a cyber-espionage campaign using macro-enabled Word docs to target Tajikistan's public sector for intelligence.

A China-linked APT, UAT-6382, is actively exploiting a zero-day (CVE-2025-0994) in Cityworks to gain RCE and persistent access to government and utility systems.

A joint advisory warns that Russia's APT28 (Fancy Bear) is actively targeting logistics and tech companies supporting Ukraine with espionage and data exfiltration.

DTEX reveals how North Korea's hidden IT workforce and cyber syndicate drive global espionage, crypto theft, and AI-powered attacks.

Russia-linked APT28 (Sednit/Fancy Bear) targets vulnerable webmail with XSS in Operation RoundPress, stealing data from global entities.

Interlock Ransomware breached AMTEC, leaking sensitive defense data and raising concerns over espionage and national security risks.

North Korean threat actor TA406 intensifies cyber espionage against Ukraine, using phishing and malware to gather political intelligence.

Earth Ammit’s VENOM and TIDRONE campaigns target Taiwan and South Korea’s drone, military, and satellite sectors via stealthy supply chain attacks.

Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.

A cyber-espionage campaign linked to Türkiye is exploiting a zero-day flaw in Output Messenger to target entities in Iraq. Learn about the attack.
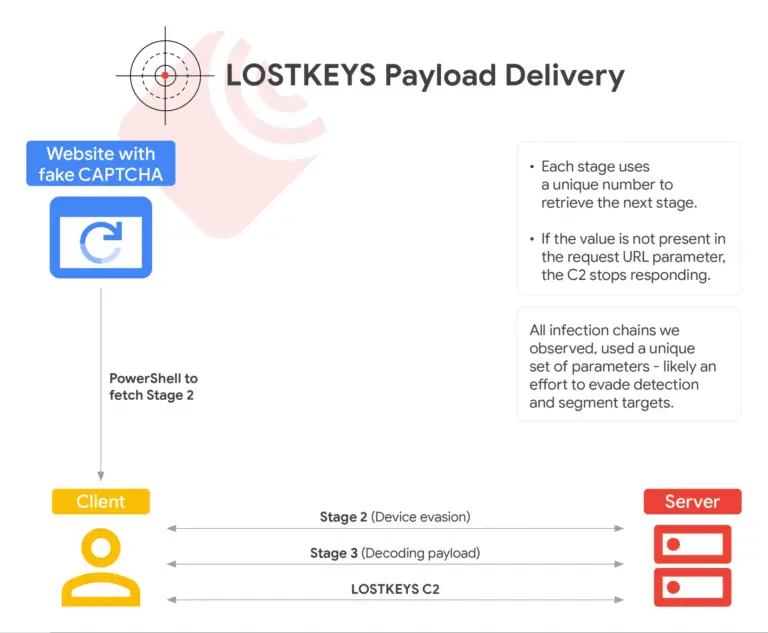
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.
Unit 42 uncovers Iranian cyber espionage using a fake modeling agency website to selectively target victims with sophisticated techniques.
Research reveals the widely used open source library 'easyjson' is controlled by developers linked to Russia's VK Group, raising security concerns.