
 Do Son
FortiGuard Labs uncovered a threat actor leveraging a sophisticated attack to distribute the CHAVECLOAK banking Trojan
Malware

When the Babuk ransomware group disbanded in 2021, it seemed like a minor victory in the ongoing...

Predator mobile spyware incorporates Python-based modules allowing for seamless updates and the introduction of new functionalities
Dubbed "Morris II," this zero-click worm exploits adversarial self-replicating prompts to spread across interconnected GenAI-powered apps

Security researchers from NVISO have uncovered two sophisticated TLS-based backdoors, dubbed SparkCockpit and SparkTar

From initial access via deceptive PDFs to the execution of obfuscated JavaScript files, the process is meticulously crafted to evade detection

A new Linux-based malware, christened GTPDOOR, has emerged with a cunning strategy to infiltrate the heart of telecommunication networks

The world of Pay-Per-Install (PPI) malware rarely stands still, and PrivateLoader, a notorious player in this arena,...

The cybersecurity landscape is constantly shifting, and a new, more insidious Linux variant of the Bifrost RAT has emerged

Security experts are currently tracking a sophisticated phishing scheme aimed squarely at entrepreneurs operating within Telegram communities

Enter GULoader, a malware favored by cybercriminals for its stealth, adaptability, and ability to bypass defenses

These actors, identified as UNC1549 and overlapping with the Tortoiseshell group, are a force to be reckoned with

This attack, attributed to the infamous Lazarus hacking group, leverages a dangerous tactic: preying on developers' typos to install malware

Bitdefender researchers have uncovered a new, stealthy variant of the infamous Atomic Stealer malware specifically targeting macOS users

Central to the Spiked Wine threat actor campaign is WINELOADER, a modular backdoor engineered with evasion and stealth in mind

Forcepoint has uncovered a sophisticated malware campaign exploiting Booking.com's brand reputation to deliver Agent Tesla malware
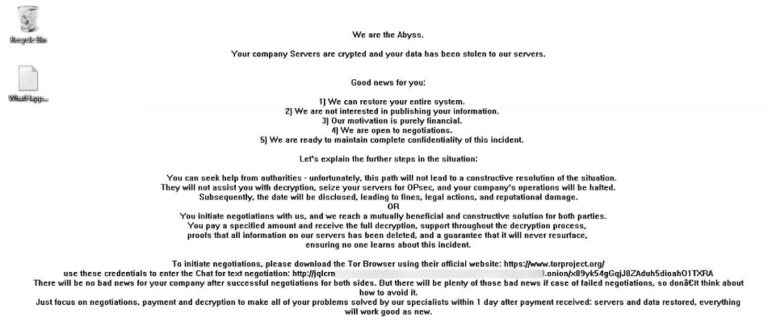
Abyss Locker ransomware terminates a plethora of processes related to security, productivity, and system management software

The new PIKABOT version introduces a novel unpacking method alongside heavy obfuscation, marking a significant evolution in its design

The campaign investigated demonstrates Turla's focus on targeted attacks. This 'Pelmeni Wrapper' loads the next stage payload.

The recently disclosed vulnerabilities in ScreenConnect (CVE-2024-1709, CVE-2024-1708) necessitate immediate action

Researchers at Talos and CERT.NGO have pulled back the curtain on new malicious components deployed by the notorious Turla APT group

The primary malware, dubbed "TrollAgent," was a data thief developed in GoLang and capable of stealing a wide array of information