
 Do Son
The Xehook Stealer goes beyond traditional password and credit card theft, posing an exceptionally broad threat.
Malware

Disguised as helpful tools to improve game performance, the malware known as "Tweaks" is spreading rapidly through popular platforms

FakeBat malware is often hidden within seemingly innocuous MSI installers. These installers are laced with heavily obfuscated PowerShell code

Dubbed "BIPClip", this campaign employed seven distinct malicious packages, released in 19 different versions since December 2022

One of the most concerning discoveries in this campaign is the deployment of a new Java-based RAT named VCURMS.

Security researchers have exposed a crafty attack campaign manipulating a decentralized content delivery network (CDN)

Attackers are tricking users into downloading a dangerous infostealer disguised as a legitimate Adobe Reader installation file

A dangerous new malware named Planet Stealer is making its rounds in the cybercriminal underworld, and security experts warn

Security researchers at GuidePoint have uncovered a new weapon in the BianLian ransomware gang’s arsenal – a...

The payload delivered through this elaborate ruse is a Lua JIT malware, comprising a compiled LuaJIT executable and a batch script

Security researchers at QiAnXin Threat Intelligence Center have uncovered a sophisticated malware campaign waged by the Kimsuky APT group

ASEC have uncovered a disturbing malware campaign that's cleverly disguised as a legitimate installer for the popular Notion software

One such group, known as UAC-0050 or "The DaVinci Group," has emerged as a key player in the ongoing conflict between Russia and Ukraine

Magnet Goblin is a financially motivated threat actor demonstrating proficiency in swiftly exploiting 1-day software vulnerabilities

The Balada Injector campaign, a sophisticated malware operation, has set its sights on exploiting a vulnerability within the WordPress plugin

NarniaRAT boasts information-stealing capabilities and swiftly conscripts the compromised machine into the Fenix Botnet.
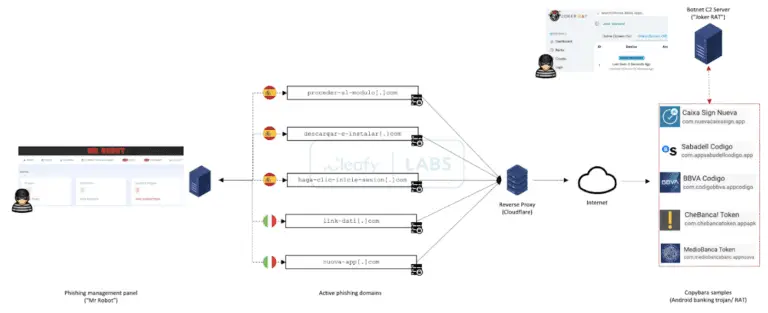
Copybara campaign unfolds in a series of meticulously executed stages. TAs are weaponizing a combination of social engineering, phishing infrastructure

Attackers are becoming increasingly adept at weaponizing trusted resources and services, as seen in a recent Python-based infostealer campaign

GhostSec aims to fund further operations, leveraging a variety of tactics from ransomware to DoS attacks to achieve their objectives.

Clicking those familiar "Windows" or "Android" download buttons unleashes the RATs, cleverly disguised behind innocent-sounding file names

Security researchers have sounded the alarm on a critical vulnerability (CVE-2024-0778) affecting outdated Zhejiang Uniview ISC cameras

A newly discovered backdoor malware dubbed 'WogRAT' is raising alarms for both Windows and Linux users.