
 Do Son
Coyote represents a paradigm shift in the realm of Brazilian banking Trojans, embracing modern technologies like Node.js, .NET
Malware

DotStealer malware, masquerading within the binary veil of a 32-bit executable, crafts its lair directly on the user's system

Raspberry Robin operates within a vast malware ecosystem, serving as an initial access broker for further malicious deployments

The ramifications of falling victim to the XPhase Clipper campaign are dire, with users facing the prospect of substantial financial losses

APT-K-47 has quickly garnered attention for its sophisticated cyber-attack techniques, which bear similarities to other notorious APT groups
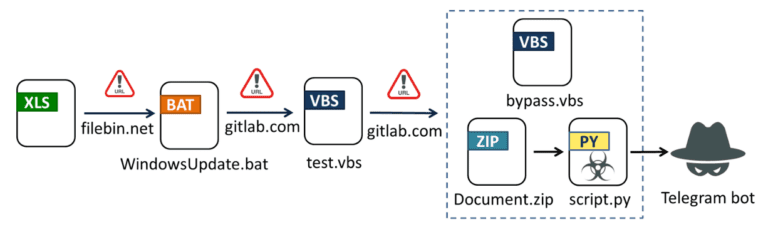
Discover how it retrieves script.py (the info-stealer), Document.zip (Python 3.11 with required libraries), and bypass.vbs (the Python executor)

Nevada Ransomware, identified by Resecurity’s threat research and intelligence team, is rapidly gaining notoriety for its advanced...

ESET has uncovered a startling revelation: a series of Android espionage apps bundled with the VajraSpy remote access trojan (RAT)

Notably, DiceLoader has been actively used since 2021, with the malware often delivered via a PowerShell script.

Unit 42 researchers stumbled upon Mispadu Stealer's latest variant while hunting for the SmartScreen CVE-2023-36025 vulnerability.

As investigators delve deeper into the labyrinthine world of the UAC-0027 hacking group, they have uncovered 486 IP addresses

The final phase of the ApateWeb campaign, Layer 3, is where victims encounter the malicious payload. This payload can manifest as scareware

This realm has now become the breeding ground for a more sinister threat: the macOS.Bkdr.Activator malware

As the tax season rolls in, so does the threat of cybercrime, and leading the charge in 2024 is the infamous TA576 threat actor

Orchestrated by the notorious APT28 group, this campaign was a masterclass in cyber deception and manipulation.

where cyber threats continually evolve, the rise of scripted ransomware marks a new era of digital extortion

Pawn Storm adopted a unique approach, sending spear-phishing emails with a small information stealer as an attachment

UNC4990 threat actor utilizes sophisticated tools like EMPTYSPACE, a versatile downloader, and QUIETBOARD, a multifunctional backdoor.

Crafted by the notorious Peach Sandstorm APT, the FalseFont backdoor has been specifically targeting defense contractors across the globe

The MDR team’s subsequent investigation uncovered over 1,000 “MessageSent” Teams events linked to the external user

A new threat actor, previously known as Trigona ransomware, has been identified as installing Mimic ransomware.

GRIT Ransomware Annual Report 2023 concludes with a forward-looking perspective, anticipating continued evolution in ransomware tactics