 Do Son
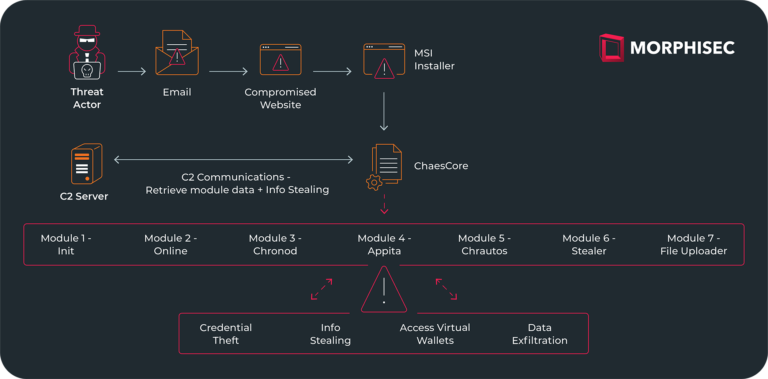
Chae$ 4.1 malware uses deceptive websites and compromised sites to distribute its payload, showcasing the attackers' adaptability
Malware

A key discovery in Volexity's investigation was the GIFTEDVISITOR webshell. Over 1,700 compromised Ivanti Connect Secure VPN devices

The NETSCOUT ASERT team has recently unearthed alarming patterns of behavior indicative of an upsurge in malicious botnet activities

7777-Botnet is known to exploit a range of vulnerabilities in various devices, including TP-Link routers, Xiongmai devices, and Hikvision cameras

Further investigation revealed that this JSP code was from an open-source web shell known as the Godzilla Webshell.

SPICA backdoor represents a significant advancement in COLDRIVER's capabilities, marking its first foray into custom malware development
the digital underworld witnessed the reemergence of TA866, a formidable threat in the realm of email-based cyber-attacks

Cado Security Labs researchers have uncovered a striking and innovative campaign that specifically targets vulnerable Docker services

Mimus ransomware employs AES-256 encryption, changing file extensions to ".encrypted" and generating ransom notes with Bitcoin wallet

The AhnLab Security Intelligence Center has uncovered that the LockBit ransomware is being spread through malicious Word files

Remcos RAT malware communicates with a remote IP address and initiates malicious activities, including keylogging and capturing screenshots

Atlantida stealer is not only adept at capturing entire screen contents but also targets specific data sources.

Kaspersky has released an open-source script, iShutdown, designed for rapid detection of spyware infections in iOS devices.

This year witnessed the alarming rise of mega ransomware attacks, characterized by their extensive scale and impact.

CherryPie, another stealthy infiltrator, exemplifies the cross-platform threat. Despite being caught by Apple, many static engines lag in detection
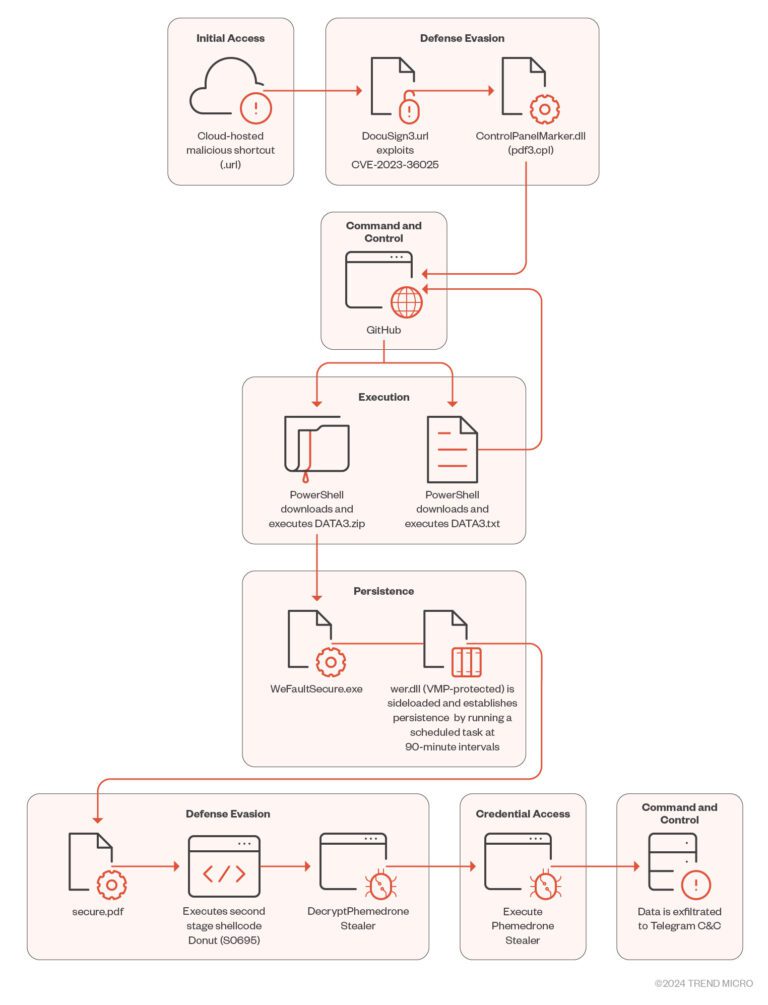
Phemedrone Stealer's infection chain begins with the hosting of malicious Internet Shortcut files on platforms like Discord or cloud services

A new predator lurks, targeting unsuspecting Chinese users through a sophisticated Financial Fraud APK campaign.

A deceptive package called 'sellpass-sdk' in PyPI, which turned out to be a distributor of the "Blank Grabber" infostealer malware
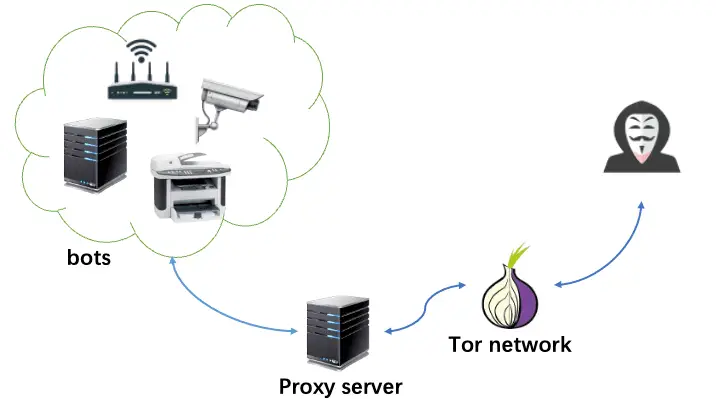
Rimasuta botnet is designed to infiltrate systems and evade detection. It employs advanced data encryption and communication techniques

WorkersDevBackdoor malware has been impacting the business services industry with its cunning distribution and destructive capabilities.

A Linux-based malware family, DreamBus has been quietly evolving, honing its capabilities to exploit vulnerabilities in business applications

Unit 42 Incident Response Team's investigation into a Medusa ransomware incident has unveiled intricate tactics, tools, and procedures