
 Do Son
Unlike Mirai, which is aimed at DDoS attacks, this new worm, dubbed NoaBot, installs crypto miners, enabling attackers to exploit
Malware

Forcepoint X-Labs, a vanguard in cybersecurity, has unveiled an intricate cyber-attack targeting business leaders during a pivotal general election period.

In the ever-evolving landscape of cyber threats, a new name has emerged with a notorious reputation –...

Victims of the Babuk Tortilla variant can now access the updated Avast Babuk decryptor through the NoMoreRansom website
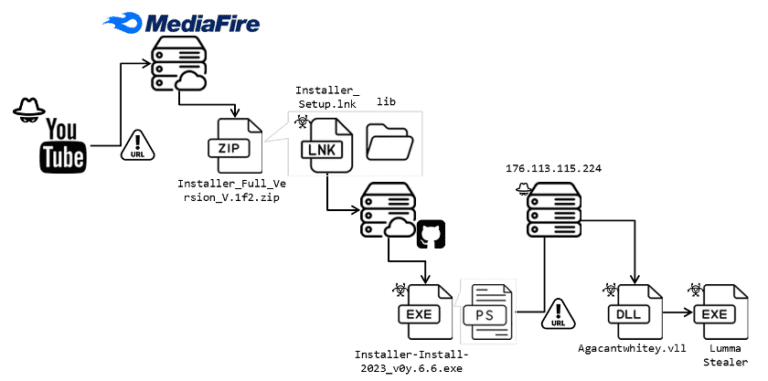
A cunning stratagem employed by a threat group, exploiting YouTube channels to disseminate a variant of the notorious Lumma Stealer malware.

SentinelOne, a security research organization, demonstrated this by creating a proof-of-concept attack using a maliciously crafted npm package

Revealing how malicious actors are using YouTube, a platform trusted for legitimate content, to distribute cryptocurrency miners.
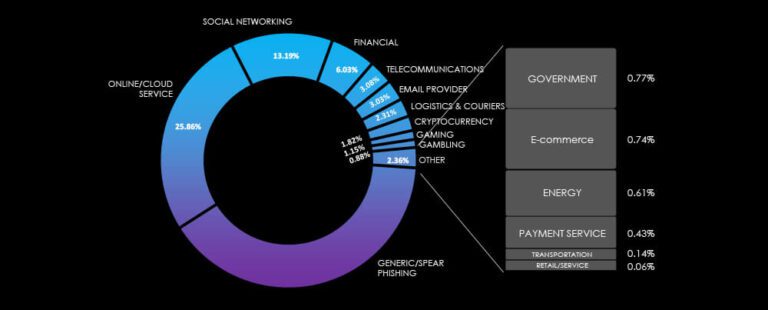
CYFIRMA Industries Report offers an illuminating look into the current state of cyber threats, in the professional goods & services industry

QiAnXin Threat Intelligence Center's detailed analysis linked the binary involved in this operation to a North Korean APT
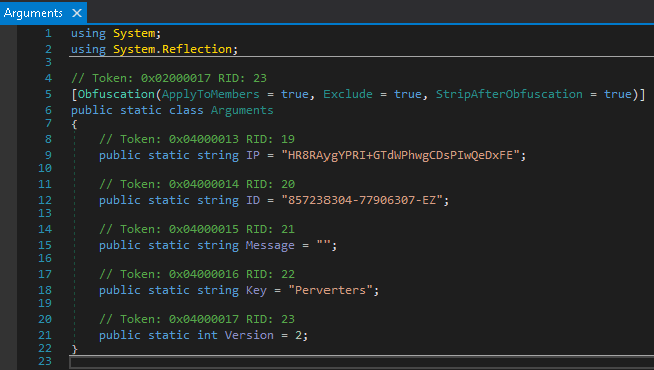
Among the myriad of threats, GuLoader and RedLine Stealer stand out for their sophisticated anti-analysis techniques.

Ducktail began its infiltration through a seemingly innocuous channel – LinkedIn. The attackers sent a private message to the target

The Python community has recently faced a new threat: three new malicious PyPI packages that deploy CoinMiner on Linux devices

At the heart of the UAC-0050 threat group's arsenal is RemcosRAT, a malware for remote surveillance and control.

Advent of scheduled task tampering as a persistence mechanism underscores the need for continuous evolution in threat-hunting

Security researchers from xlab-qianxin detected Mirai.TBOT, a variant of the original Mirai, operates with distinct characteristics

Their research has refined the classic DLL Search Order Hijacking technique, leveraging executables in the trusted WinSxS folder of Windows OS

These actors have been utilizing the ms-appinstaller protocol handler as a vector for malware, potentially leading to ransomware distribution

Central to Kimsuky's operations is AppleSeed, a backdoor malware that facilitates remote system control. It can execute commands

Carbanak malware, previously utilized for stealing banking data, is now employed by the cybercriminal group FIN7 for remote control

JaskaGO malware checks whether it is operating on a virtual machine, and if so, performs a harmless task, like pinging Google, to avoid detection

In the vast expanse of the digital ocean, a new wave of cyber attacks has emerged, targeting the seemingly unassuming Linux SSH servers.

PhantomControl, a chameleon in the digital world, has previously been associated with the Blind Eagle threat actors