
 Do Son
Stay informed about the latest phishing campaigns targeting businesses in Poland, Italy, and Romania. Learn how the ModiLoader Trojan is used to deliver malicious software.
Malware

Explore the rise and decline of UNC4393, a prolific ransomware gang. Learn about their tactics and targets in this comprehensive report.
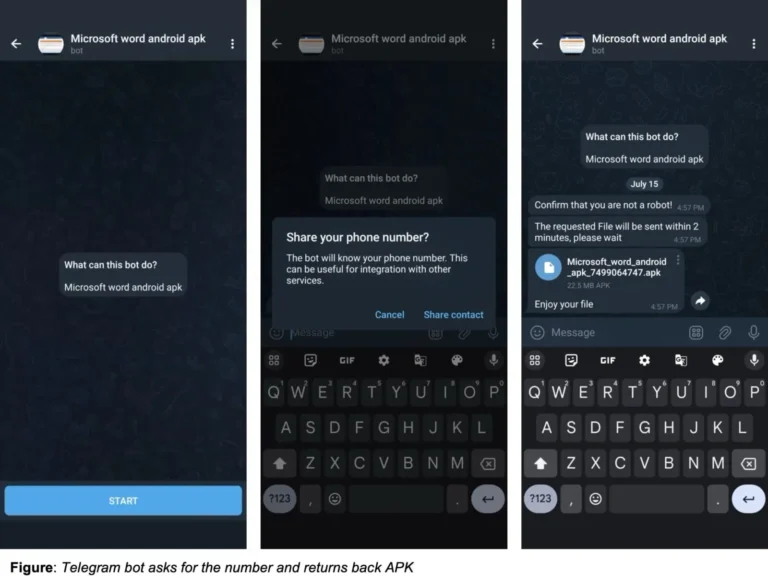
Discover the alarming spread of a new Android malware campaign: a silent SMS stealer targeting OTPs from top brands and compromising millions of accounts.

Beware of the latest OneDrive phishing campaign that tricks users into downloading malware. Stay informed and protect yourself from this sophisticated attack.

Stay safe from fake Google Authenticator downloads! Learn about the malicious campaign impersonating Google and spreading DeerStealer malware

Learn about the increase in IoT malware and supply chain attacks in 2024. Get insights from SonicWall's mid-year Cyber Threat Report.

Lab52 warns about the RansomHub ransomware gang. Discover their unique tactics and the potential impact on your organization's systems.

Learn about the sophisticated and persistent cyber espionage campaign known as Cuckoo Spear, attributed to the Chinese state-backed APT group APT10
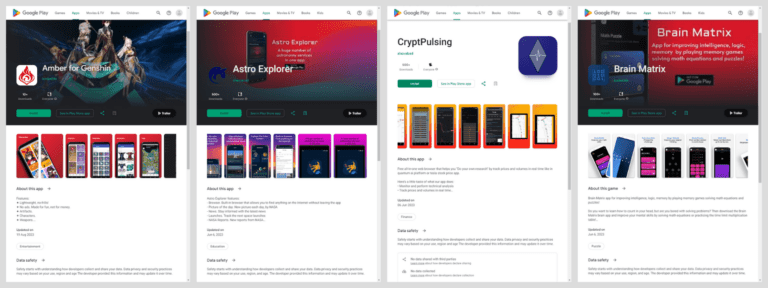
Discover the return of the Mandrake spyware on the Google Play Store. Uncover its obfuscation techniques and its widespread impact.

Discover the latest cybersecurity trends affecting SMBs. Find out about the surge in malware infections and the favored tactics used by cybercriminals.

Symantec's report reveals a concerning trend: cybercriminals are weaponizing ChatGPT hackers to craft sophisticated and deceptive attacks.

Discover the details of Operation ShadowCat, a highly sophisticated cyber espionage campaign targeting individuals involved in Indian political affairs

Beware of the new Latrodectus Malware phishing campaign targeting individuals searching for W2 tax forms online.

From cheat to malware: the story of EvolvedAim, a once-popular cheat for Escape From Tarkov that turned into a malicious endeavor.

Learn about the latest FormBook malware attack exploiting a vulnerability in Secure Email Gateways. Stay informed and protect your organization.

Learn about the large-scale operation to remove the PlugX trojan from infected devices. Discover how the French police and cybersecurity company Sekoia are combating this threat.

Protect yourself from the LummaC2 malware variant that uses Steam as a C2 server. Understand the techniques employed and the various channels

A stealthy cyber campaign is leveraging a critical flaw in Microsoft Windows SmartScreen, the built-in security feature

Network traffic analysis indicated that the Quad7 botnet is used for Password Spraying attacks on Microsoft 365 accounts

HotPage installs a driver capable of injecting code into remote processes, along with two libraries that intercept and modify browser network traffic

The espionage group Daggerfly has also introduced a new Windows backdoor, Trojan.Suzafk, first documented by ESET in March 2024

CrowdStrike, a leading cybersecurity firm, has issued a warning about a new information-stealing malware dubbed "Connecio"