
 Do Son
GrimResource technique capitalizes on an old XSS vulnerability in the apds.dll library, enabling attackers to execute arbitrary JavaScript code
Malware

The active exploitation of CVE-2024-29973 by a Mirai-like botnet underscores the urgency of applying the necessary security patches

Advanced Persistent Threat (APT) group APT-C-35, also known as DoNot Team, has been identified as one of the actors employing Rafel RAT

A new ransomware-as-a-service (RaaS) called RansomHub has emerged, targeting Windows, Linux, and ESXi operating systems

In a recent report, the eSentire Threat Response Unit (TRU) has uncovered a sophisticated adware strain dubbed AdsExhaust

Cisco Talos identified the SneakyChef group after observing a series of cyberattacks using the SugarGh0st RAT to target users

From early to mid-June 2024, the Zergeca botnet primarily targeted regions such as Canada, the United States, and Germany

SocGholish, a sophisticated JavaScript malware framework, has been a persistent threat since its emergence in 2017.

The perpetrators, utilizing tools linked to various Chinese espionage groups, have successfully penetrated these telecom networks

UNC3886 exploited a now-patched vulnerability in FortiOS, alongside a custom malware ecosystem targeting Fortinet devices
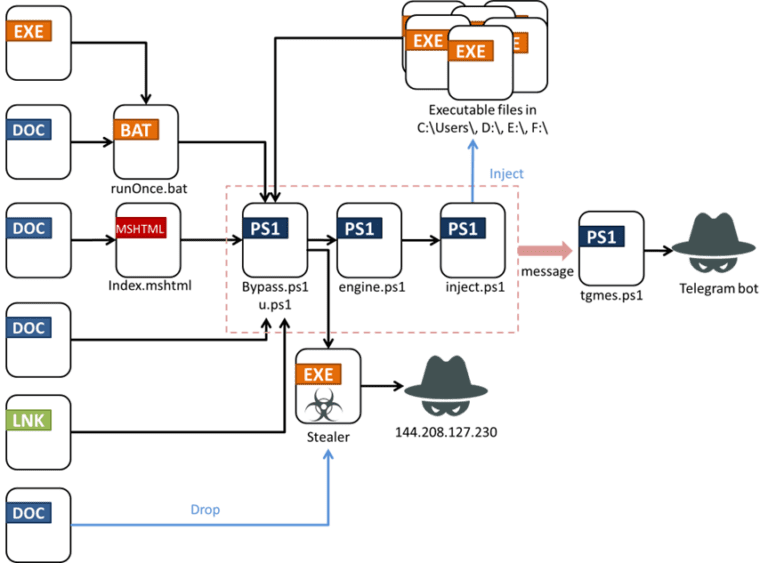
Fickle Stealer executes several scripts designed to bypass User Account Control (UAC) and prepare the environment for the main payload

Cybersecurity researchers at Avast have unearthed a new and previously undetected variant of the Diamorphine Linux kernel rootkit

Rapid7, a cybersecurity firm, has uncovered a recent malvertising campaign using fake software installers to distribute the Oyster backdoor

Cisco Talos has published a comprehensive report detailing a long-running cyber espionage campaign dubbed "Operation Celestial Force."

This new method has been employed by threat actors such as TA571 and the ClearFake cluster, targeting users with malware including DarkGate

Volexity has revealed a new cyber-espionage campaign targeting Indian government entities, employing a custom-built malware dubbed DISGOMOJI

TRU has uncovered a new campaign by the SolarMarker threat group, which involves the impersonation of the global employment website Indeed

New Cryptojacking Campaign suspected to be an evolution of the previously identified Spinning YARN operation

cybersecurity researchers have unveiled a sophisticated new backdoor, dubbed "BadSpace," that poses a significant threat to internet users

A recent analysis by security researcher Jacob Malimban at Cofense has revealed a resurgence in activity from the STR RAT malware

ASEC has published a report detailing a significant shift in the tactics employed by the Bondnet threat actor

The Black Basta ransomware group may have exploited a previously unknown vulnerability (CVE-2024-26169) in Windows Error Reporting Service