
 Do Son
Cybersecurity researchers at Trend Micro have unveiled a previously undocumented backdoor malware dubbed "Noodle RAT,"
Malware

This vulnerability is currently being actively exploited by malicious actors in a widespread ransomware campaign known as "TellYouThePass."

A new variant of an ongoing cryptojacking campaign targeting misconfigured Kubernetes clusters has been uncovered

FortiGuard Labs has recently identified a new phishing campaign deploying a variant of the notorious Agent Tesla malware

eSentire's Threat Response Unit (TRU) has unveiled a persistent and sophisticated cyber campaign employing the notorious more_eggs malware

TRU has unveiled a sophisticated attack campaign utilizing counterfeit KMSPico activators to deliver the notorious Vidar Stealer malware

Sophos researchers have uncovered a sophisticated and long-running cyberespionage campaign, dubbed Operation Crimson Palace

The attack begins with hackers compromising websites and inserting malicious code, often through the legitimate WordPress plugin "Hustle."

CVE-2023-33246 in RocketMQ versions 5.1.0 and below, allowing attackers to remotely execute code and download the notorious Muhstik malware

Trustwave SpiderLabs has uncovered a dangerous cyberattack campaign targeting users of the popular network scanning tool, Advanced IP Scanner

ReversingLabs researchers uncovered a malicious open-source package on the Python Package Index (PyPI) called xFileSyncerx

RansomHub attackers gained initial access by exploiting the Zerologon vulnerability (CVE-2020-1472), which grants domain administrator privileges

Cybersecurity researchers have uncovered a novel cryptojacking campaign dubbed "Commando Cat," actively targeting Docker Remote API servers

A CoinMiner, a type of malware that hijacks systems to mine cryptocurrency, unwittingly left a backdoor open

ASEC has recently identified a phishing campaign leveraging HTML files distributed via email to execute malicious commands on targeted systems

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation

UNC1151 employed DLL loaders that downloaded an encrypted JPG file, which was then decrypted to deploy a final payload executable.
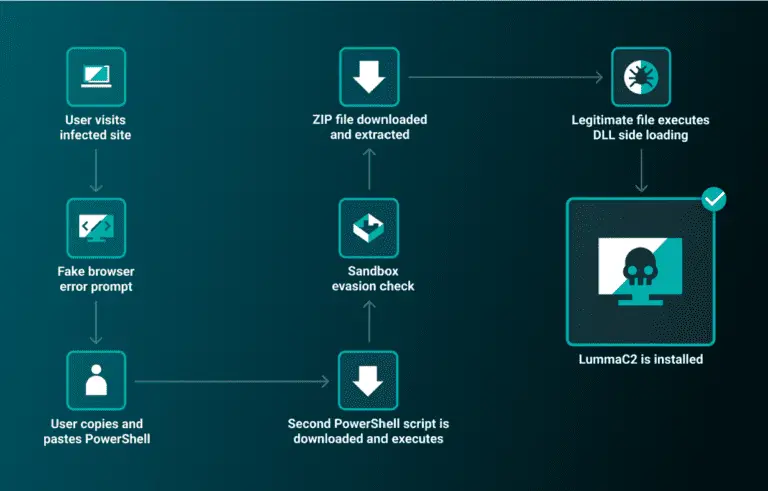
The ReliaQuest Threat Research Team has unveiled a new execution technique used in the ongoing ClearFake campaign

This multi-stage malware strategy ultimately delivers the notorious "Cobalt Strike" payload, establishing communication with a C2 server

BlueDelta even managed to bypass two-factor authentication and CAPTCHA challenges by leveraging compromised Ubiquiti routers

Krasimir Konov, malware analyst at Sucuri, exposes how hackers are leveraging Telegram's unique features to execute sophisticated website attacks

A new banking Trojan named "CarnavalHeist" is targeting Brazilian users, exploiting the country's festive spirit to steal financial data