 Do Son
The malware file named “.redtail” confirmed the presence of the RedTail cryptominer, previously reported by Cyber Security Associates (CSA)
Malware

The malware, identified as an InfoStealer, poses as the official app of Bahrain’s Labour Market Regulatory Authority (LMRA)

Chalubo malware was highly active in late 2023 and early 2024, with over 330,000 unique IP addresses communicating with known C2 servers

A new and sophisticated malware named AsukaStealer has emerged on the cybercrime scene, offering its malicious services

LilacSquid deploys a series of malicious tools, including MeshAgent, a customized version of QuasarRAT, dubbed "PurpleInk,"

The campaign utilizes a complex DLL side-loading technique involving legitimate files from the IObit anti-malware solution to execute malicious payloads

BitRAT is a powerful remote access tool that grants attackers extensive control over infected systems, enabling them to steal sensitive data

XLab's CTIA System uncovered the abuse of the Kiteshield packer by various cyber threat actors targeting Linux environments

Cybersecurity firm ReliaQuest has published a detailed analysis of a BlackSuit ransomware attack that occurred in April 2024

Cybersecurity researchers at Zscaler ThreatLabz have uncovered a sophisticated Android banking trojan called Anatsa (also known as TeaBot)

Moonstone Sleet deployed a new ransomware variant named FakePenny. This ransomware was used to target a company

Experts have exposed a new ransomware threat named ShrinkLocker, which cleverly exploits Microsoft's built-in BitLocker encryption tool

NetbyteSEC Detecx (NBS) team exposed a sophisticated malware campaign orchestrated by the notorious SharpPanda APT group

CatDDoS-related gangs have leveraged a wide array of vulnerabilities across multiple vendor devices like Apache, Cisco, D-Link, Huawei, ...
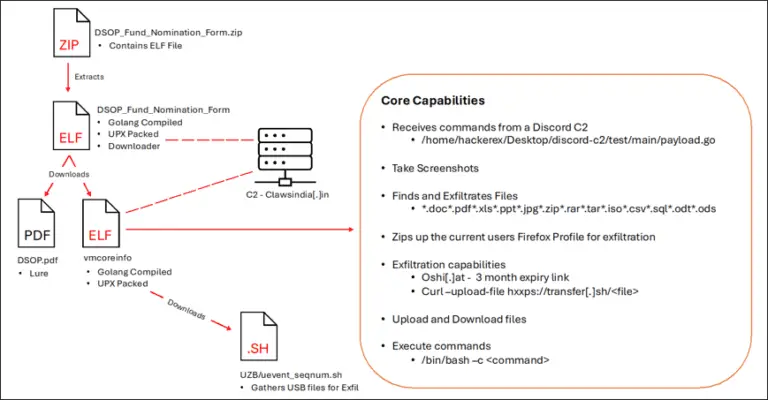
Researchers revealed a sustained campaign by Pakistani-based cyber espionage group APT36 targeting critical Indian government

attackers are leveraging an obscure WordPress plugin to install server-side malware, harvesting credit card details from WooCommerce online stores

The persistent cyber threat known as Kinsing malware has taken a new and sophisticated approach to its cryptojacking campaign

A critical vulnerability, designated CVE-2024-4978, has been discovered in Justice AV Solutions (JAVS) Viewer software

UAC-0006 is known for its use of the SMOKELOADER malware, a versatile tool often used to deliver additional malicious payloads

SamsStealer casts a wide net, targeting a broad spectrum of applications and platforms to maximize its data collection potential

CRIL identified a sophisticated campaign employing a tiny, stealthy backdoor, now suspected to be the work of the infamous Turla APT group

Elastic Security Labs has shed light on a complex and insidious crypto-mining operation codenamed REF4578, with its core payload, GHOSTENGINE