 Do Son
A Citrix security update fixes seven XenServer and UniconOS flaws, including guest-to-host and privilege escalation bugs. Patch hosts and thin clients.
News
Microsoft fixes the frustrating Windows 11 mouse stutter and cursor drift issues in games with the new KB5127648 update for versions 24H2, 25H2, and 26H2.
A SiteGuard Server Edition vulnerability, CVE-2026-106931, is exploited in the wild and grants root or SYSTEM access. Update to Ver8.00 Update 5 now.
Google restructures its Chrome VRP rewards, raising baseline payouts for memory corruption bugs to $2,000 and offering up to $20,000 for critical exploits.
Microsoft now audits ReFS removable storage in Windows 11 and will block mounting external ReFS volumes by default starting in January 2027.
GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
Review the latest Juniper security bulletin to patch critical Junos OS vulnerabilities, including RCE flaws CVE-2026-102182 and CVE-2026-101954.
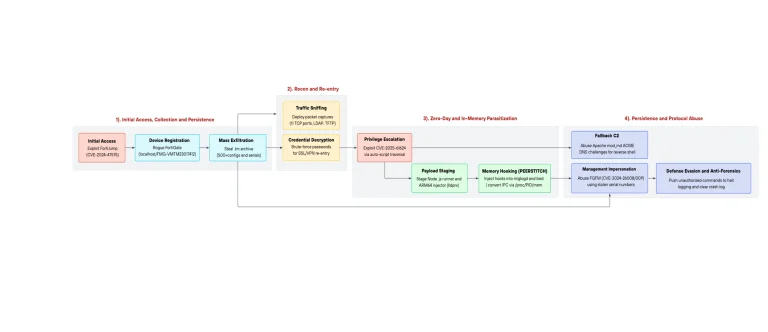
Unit 42 reveals how CL-STA-0954 deploys PEERSTITCH malware after a FortiManager breach, using FortiOS PEERSTITCH malware to hijack firewalls.
Apply the DSA-2026-405 security update for Dell Wyse Management Suite to fix four XSS flaws, including critical bug CVE-2026-82158 (CVSS 9.0).
Apply the NLnet Labs NSD patch for 4 flaws, including CVE-2026-101341. Each NSD stack overwrite vulnerability risks remote command execution.
Patch two high-severity SonicWall NSM On-Prem vulnerabilities (CVE-2026-96540, CVE-2026-100232) allowing admin privilege escalation and OS command RCE.
Microsoft and Proofpoint executed a CoGUI phishing kit takedown, seizing domains from YAM Store and Iron Man after 1B scam messages hit 75,000 firms.
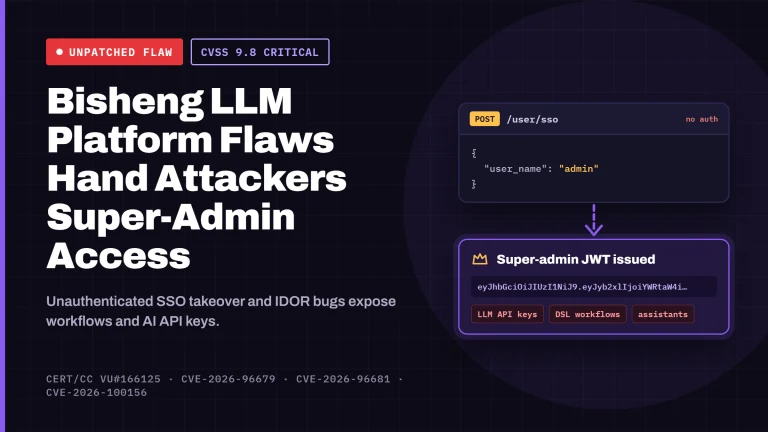
CERT/CC disclosed three DataElement Bisheng vulnerabilities (CVE-2026-96679, CVE-2026-96681, CVE-2026-100156) allowing unauthenticated admin takeover.
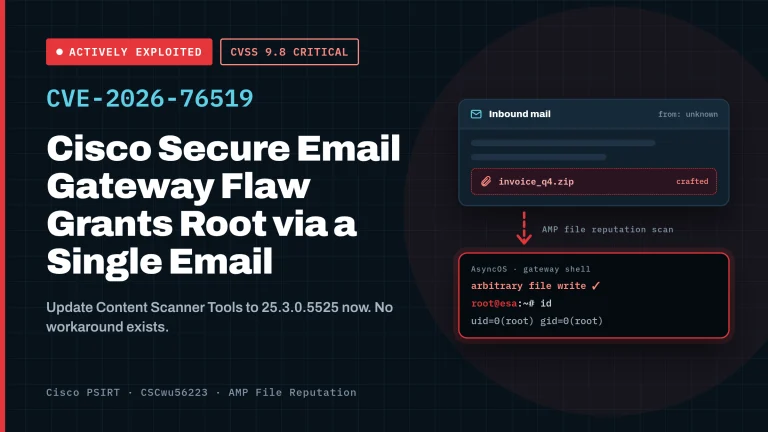
Attackers are exploiting CVE-2026-76519 (CVSS 9.8), a critical Cisco Secure Email Gateway vulnerability allowing root RCE via attachments. Patch right now.
Attackers are actively exploiting CVE-2026-0322, a high-severity Palo Alto PAN-OS RCE vulnerability in the management interface. Apply patches right now.
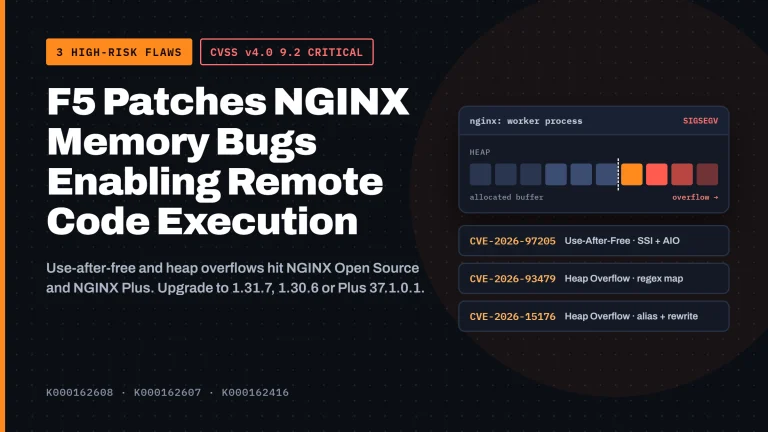
F5 patched three NGINX vulnerabilities (CVE-2026-97205, CVE-2026-93479, CVE-2026-15176) rated 9.2 Critical in F5 NGINX Plus and Open Source. Upgrade today.
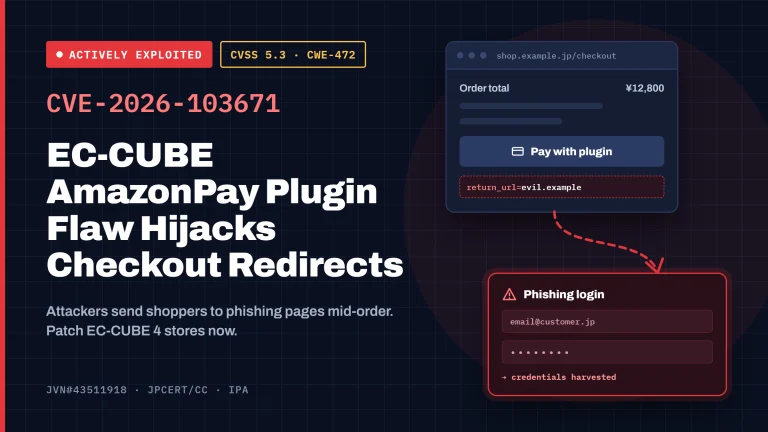
Attackers are exploiting CVE-2026-103671 in the wild, an EC-CUBE AmazonPay Plugin vulnerability that redirects shoppers to steal account credentials.
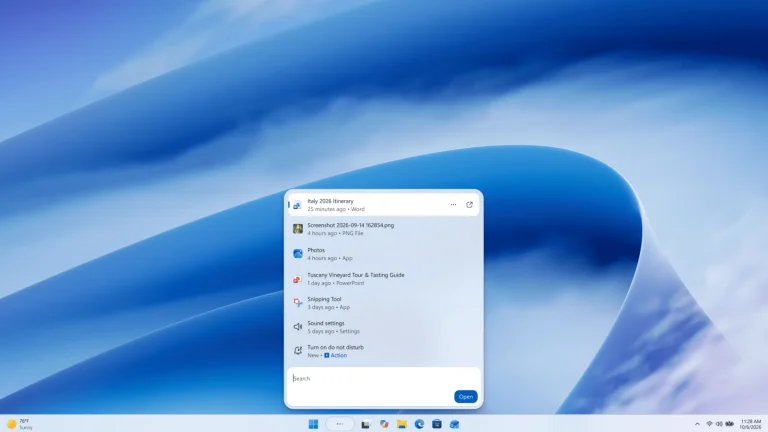
Download the Windows 11 KB5127648 update for versions 24H2, 25H2, and 26H2. This patch fixes AC-3 audio crashes, login black screens, and security flaws.
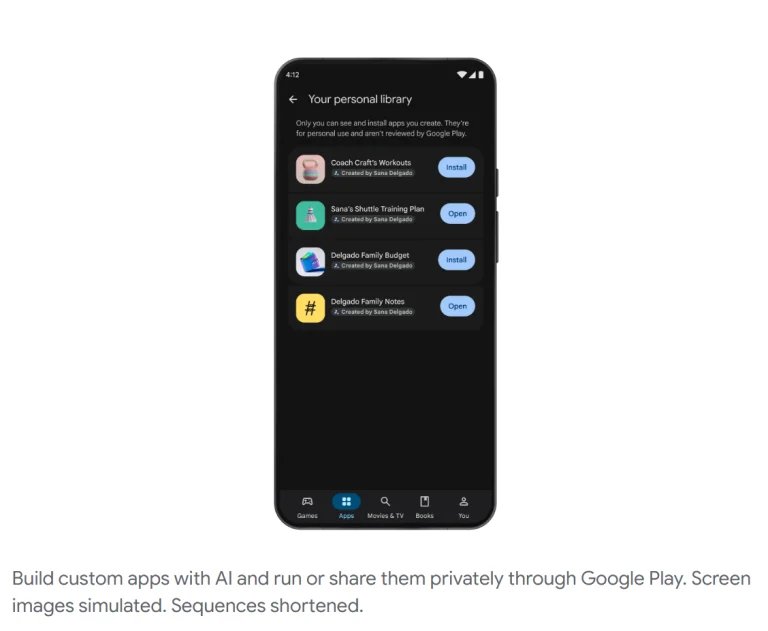
Users can now publish Google Play AI apps using a standard account. Discover how Google AI Studio and Gemini are transforming Android app development.
Microsoft officially announces Windows 11 24H2 EOL for Home and Pro editions. Learn why you must upgrade to 25H2 or 26H2 to maintain critical security.
Discover Google Gemini 4 Argon. Learn how this new AI model matches GPT-6 Astra in performance while offering lower API costs and Antigravity integration.