 Do Son
TL;DR
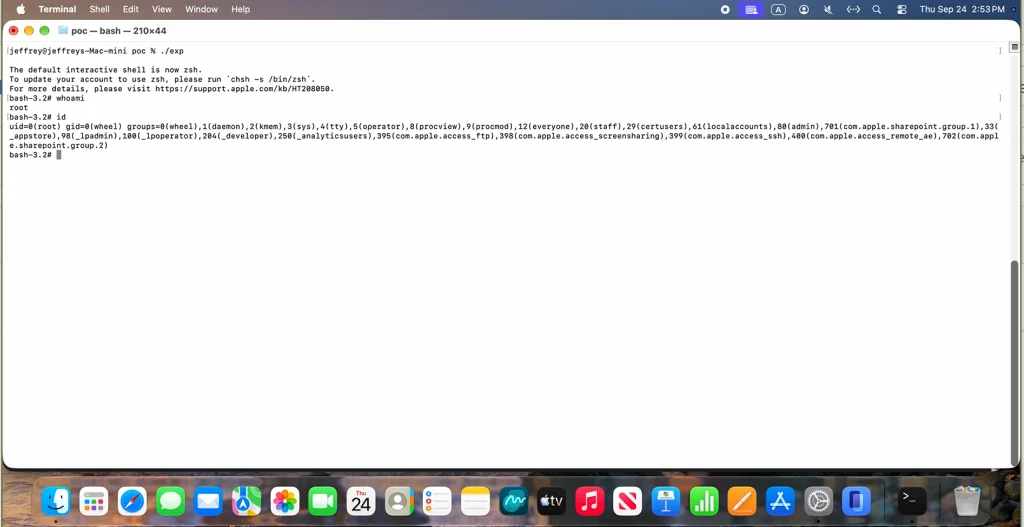
Security researcher Mas0nShi released full details and exploit code for CVE-2026-112445. This flaw is a simple macOS privilege escalation bug in launchd daemons. It lets a standard desktop user gain root rights without a password. Therefore, Mac users must update their systems right away. They need to keep their Macs safe from harm.
Why It Matters
Apple supports over 100 million active Macs, based on market data. In fact, many firms run shared Macs for staff. Because of this, local bugs bring real risk to office networks. Attackers can abuse these bugs to bypass user checks.
The researcher shared all details in a public GitHub repository with proof-of-concept exploit code. The post shows how simple the attack path is on modern Macs. In addition, security teams confirm that no active exploitation in the wild has occurred.
How the Attack Works
The Unauthenticated uscwoap Service
The security issue stems from an old system daemon named com.apple.xpc.uscwoap. Apple configured this LaunchDaemon to set Bash as an interactive shell linked to the console.
The researcher explains: “A non-administrator account logged into the active graphical console can start this job through launchd’s job control interface without administrator credentials.”
Root Execution via Terminal Queue
Once started, the Bash shell runs as root with UID 0. It links standard input to /dev/console. In turn, the desktop user owns this console device. Because of this, they can feed text into its input queue.
Specifically, the attacker calls the TIOCSTI terminal control tool. This tool pushes characters right into the queue. The report notes: “Bash interprets the characters as commands and executes them with its own root privileges.” As a result, input from a normal user runs as root.
Affected Versions
This macOS privilege escalation flaw affects builds before macOS 27.2.
Patch and Mitigation Steps
Apple fixed the flaw in macOS 27.2 by removing the daemon file. Therefore, admins should install macOS 27.2 today. Furthermore, security teams should audit LaunchDaemons for unknown files.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
