
 Do Son
CVE-2023-25616 (CVSS score of 9.9), a code injection vulnerability in SAP BusinessObjects Business Intelligence Platform (CMC)
Vulnerability

Bytecode Alliance Wasmtime, CVE-2023-26489, with a CVSS3 score of 9.9, is caused by an out-of-bounds read/write on x86_64.

The vulnerability has been assigned two CVEs, CVE-2022-47003 for Mura CMS and CVE-2022-47002 for Masa CMS, with a CVSS3 score of 9.8 for both

Bug has been identified as CVE-2023-27482, with a CVSS score of 10, the highest possible score, indicating that it is a critical security issue

Due to the CVE-2023-26604 vulnerability, an attacker could potentially exploit the system to gain elevated privileges to execute commands

CVE-2023-25610 allows an unauthenticated attacker to execute arbitrary code on the system, caused by a heap buffer underflow in the administrative interface
A remote attacker could exploit CVE-2023-25690 to bypass access controls in the proxy server, proxying unintended URLs to existing origin servers

CVE-2022-35914 allows a remote attacker to execute arbitrary PHP code on the system, caused by a flaw in the script in the htmlawed module
4 of the critical bugs patched this month reside in System (CVE-2023-20951 & CVE-2023-20954) and Qualcomm's closed-source components
Today, a technical analysis of the CVE-2023-21716 (CVSS score: 9.8) bug was published and a PoC exploit has now been released.

CVE-2022-31678 allows a remote attacker to obtain sensitive information, caused by improper handling of XML external entity declarations
CVE-2023-26463 vulnerability can allow an attacker to bypass authentication and potentially execute remote code on your system.
CVE-2023-0656 allows a remote unauthenticated attacker to cause DoS by exploiting a stack-based buffer overflow vulnerability
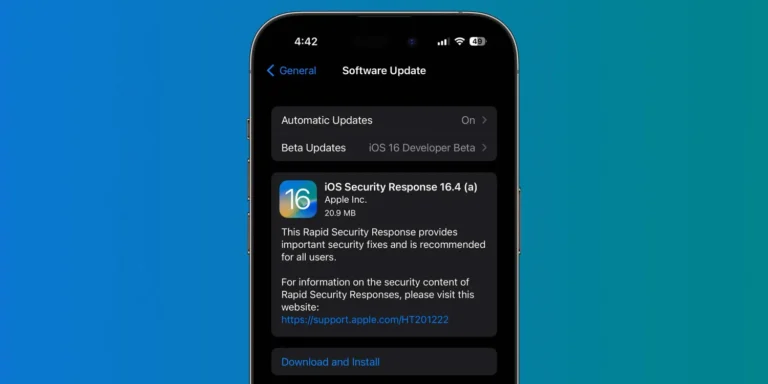
Apple has now released the first Rapid Security Response update for iOS 16.4 (a) to testers, which is likely only for testing purposes
CVE-2023-20078 in the web-based management interface of Cisco IP Phone allow attackers to execute arbitrary commands with root privileges

An attacker could exploit CVE-2023-1017 to execute arbitrary code in the TPM context or crash the TPM chip/process or rendering it unusable.
Tracked as CVE-2023-27320, the flaw exists in sudo's per-command chroot feature, which allows users to specify an alternate root directory

Most critical flaw affecting ZoneMinder tracked as CVE-2023-26035 (CVSS score: 10), stems from an insufficient validation of permissions check

Apache Airflow has published a security advisory to warn users about multiple vulnerabilities affecting many of its packages.

CVE-2023-22920 could allow a remote attacker to gain unauthorized access to the system, caused by a factory-default misconfiguration

Bugs tracked as CVE-2023-25157 affecting GeoServer and CVE-2023-25158 affecting GeoTools carry a critical severity rating of 9.8 on the CVSS
Security researchers discovered CVE-2023-22578 & CVE-2023-25813, two critical-severity defects in Sequelize assessed with a CVSS score of 10