
 Do Son
CVE-2022-47502 is a critical-severity vulnerability that affects Apache OpenOffice versions 4.1.13 and older.
Vulnerability

Deno, the popular runtime for JavaScript, TypeScript, has recently been identified with a critical security vulnerability (CVE-2023-28445)
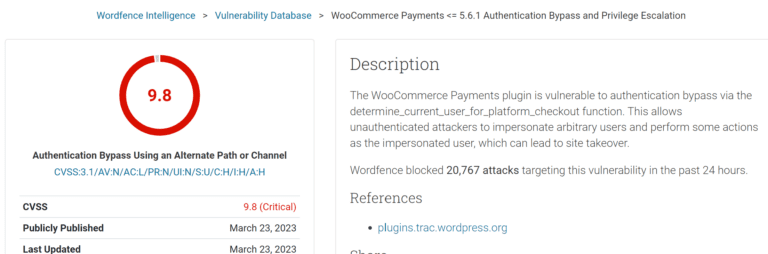
a critical vulnerability with a CVSS score of 9.8, resides in the WooCommerce Payments plugin versions 4.8.0 through 5.6.1

Due to CVE-2023-28432, MinIO returns all environment variables, including sensitive information like MINIO_SECRET_KEY and MINIO_ROOT_PASSWORD
Designated as CVE-2023-0386, this vulnerability has been assigned a CVSS score of 7.0, indicating a high level of severity

The vulnerability, identified as CVE-2023-28708, allows cybercriminals to access session cookies transmitted over an insecure channel

The CVE-2022-37337 vulnerability stems from the dev_name parameter in the access control function, which is susceptible to command injection.

By using a specially crafted file, an attacker could exploit the CVE-2023-28115 vulnerability to execute arbitrary code on the system.

The CVE-2023-20860 vulnerability, which carries a Common Vulnerability Scoring System (CVSS) score of 8.8, involves a security bypass

Flatpak has been found to allow remote attackers to execute arbitrary commands on the system. CVE-2023-28100- CVSS score of 10
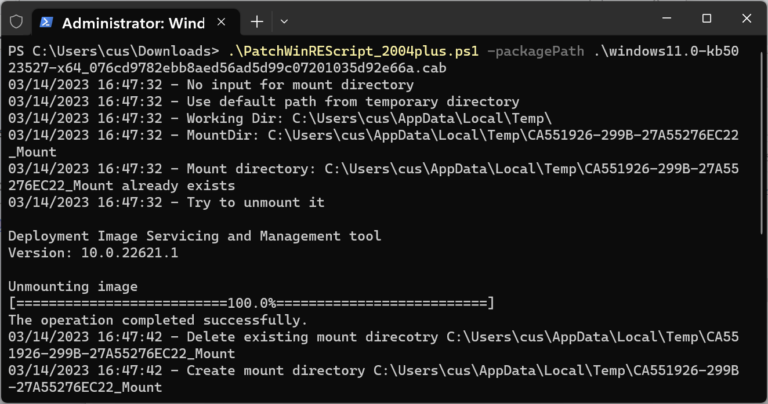
Microsoft unveiled dedicated PowerShell scripts for enterprise IT administrators, intended to remediate CVE-2022-41099 vulnerability.

CISA warns of nation-state-backed hackers and cybercrime groups exploiting an old Telerik vulnerability, compromising a federal agency's network server

By persuading a victim to open a maliciously crafted file, an attacker can exploit CVE-2023-27329 to execute arbitrary code on the system.

CVE-2023-25589 - A critical (CVSS3 score of 9.8) vulnerability in the web-based management interface of ClearPass Policy Manager

CVE-2023-23392 which carries a CVSS score of 9.8, enables a remote attacker to execute arbitrary code on the affected systems.

With a CVSS score of 9.6, CVE-2022-39214 is a high-severity vulnerability that allows authenticated users to bypass security restrictions

CVE-2023-27588, with a CVSS score of 7.5, is an unauthenticated path traversal vulnerability affecting the Hasura GraphQL Engine
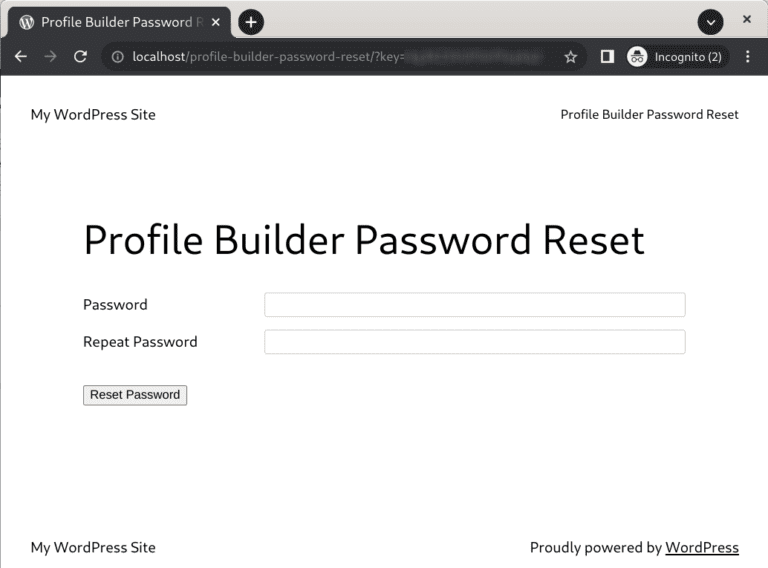
Exploiting CVE-2023-0814 can retrieve this key for any user. Hackers can reset the targeted user's password and subsequently login

Malicious actors can exploit the CVE-2023-22885 vulnerability by setting up a rogue SMB server to respond to client requests

The vulnerability, tracked as CVE-2023-24880, allows attackers to create files that can bypass Mark of the Web (MOTW) defenses

Adobe released security updates for ColdFusion versions 2021 and 2018 to resolve this critical flaw, tracked as CVE-2023-26360

Attackers can exploit CVE-2023-23397 by sending specially crafted emails that force a connection from the victim's device