
 Do Son
A memory leak vulnerability (CVE-2023-26083) affects Arm Mali GPU Kernel Driver across multiple versions, exposing sensitive kernel metadata.
Vulnerability

CVE-2023-28205, is a use-after-free vulnerability found in WebKit. It can be exploited by tricking targets into loading malicious web pages

Users are strongly encouraged to upgrade their Mali GPU driver to the latest fixed versions to mitigate the risks associated with these vulnerabilities
With a CVSS score of 10, the CVE-2023-29017 vulnerability is a significant concern for users of this popular sandboxing tool.
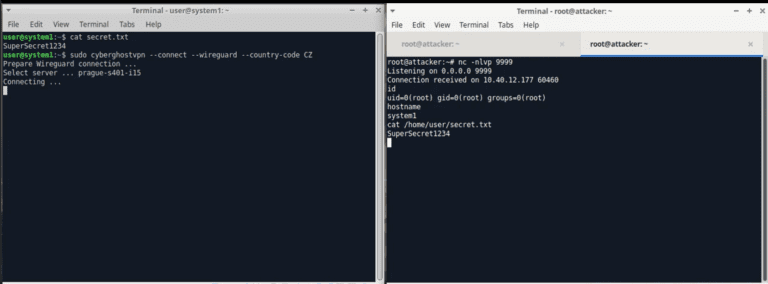
two vulnerabilities have been discovered, which, when combined, can lead to a man-in-the-middle (MITM) attack and remote code execution (RCE)

The CVE-2023-20117 & CVE-2023-20128 vulnerabilities found in the web-based management interface of Cisco RV320 and RV325 VPN Routers

CVE-2023-20102 (CVSS score of 8.8) could allow an authenticated, remote attacker to execute arbitrary code on the underlying OS
CVE-2022-4939, with a CVSS score of 9.8, is a severe security flaw affecting WCFM Membership versions up to and including 2.10.0

One such researcher discovered a critical pre-authentication command injection vulnerability (CVE-2023-1671) in the SWA's warn-proceed handler

An attacker could exploit CVE-2023-1550 to gain access to private keys, and use this information to launch further attacks against the affected system

Five of the critical vulnerabilities patched this month reside in System (CVE-2023-21085 and CVE-2023-21096) and Qualcomm components

Today, a security researcher from SSD Labs released a proof-of-concept (PoC) exploit code for the CVE-2023-0656 flaw.
CVE-2023-0189 and CVE-2023-0184 (CVSS scores of 8.8) vulnerabilities affect both Windows and Linux versions of the NVIDIA GPU Display Driver

CVE-2023-25076 affects the latest version on GitHub, the 0.6.0-2 Debian package, and potentially several forks of the original repository

In an increasingly connected world, security vulnerabilities are a persistent concern for businesses and individuals alike. The...
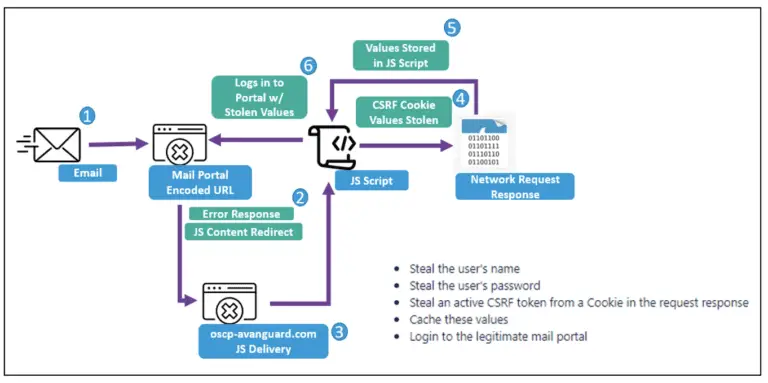
TA473 started exploiting the Zimbra vulnerability CVE-2022-27926 in phishing campaigns targeting European government entities

CVE-2023-0614 highlights a vulnerability that allows attackers to access and potentially obtain confidential information

CVE-2023-28326 is considered critical and can potentially cause serious harm to users and organizations that use this software.

Dubbed "MacStealer," the attack targets Wi-Fi networks with malicious insiders and exploits client isolation bypasses (CVE-2022-47522)

However, an e-commerce giant Pinduoduo used CVE-2023-20963 in conjunction with prior vulnerabilities to re-exploit the flaws.

The CVE-2023-25196 vulnerability also involves improper neutralization of special elements used in SQL commands.

CVE-2023-1177 is a more severe security vulnerability with a CVSS score of 10, enables an attacker to download arbitrary files from the host server