
 Do Son
The vulnerabilities have been confirmed in versions 3.8.45 and 3.8.49 of the Kiddoware Kids Place Parental Control Android App
Vulnerability
A Proof-of-Concept (PoC) for CVE-2023-32233 allows unprivileged local users to start a root shell on impacted systems.
CVE-2023-2499 (CVSS score of 9.8) is an authentication bypass vulnerability present in RegistrationMagic versions up to and including 5.2.1.0
CVE-2023-32314, (CVSS score of 9.8) vulnerability could allow a malicious entity to bypass the sandbox protections.

Dubbed CVE-2023-32784, this security bug exposes a loophole that allows for the master password to be dumped from memory
CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, indicating evidence of active exploitation.
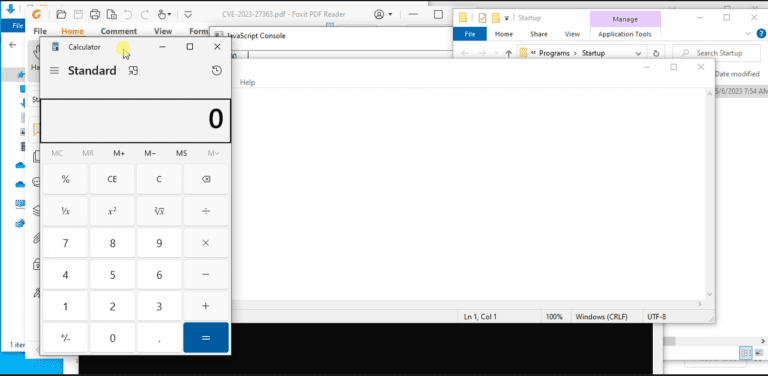
In a recent development, researcher j00sean has released a proof-of-concept (PoC) for the CVE-2023-27363 vulnerability.

Aruba issued patches for multi security vulnerabilities found in its ArubaOS 10 and Aruba InstantOS, which were affecting its access points

CVE-2023-28936 stems from an insufficient check of the invitation hash, allowing an attacker to access any arbitrary recording or room

The grave security flaw, tracked as CVE-2023-32243, with a CVSS score of 9.8, is an unauthenticated privilege escalation vulnerability.
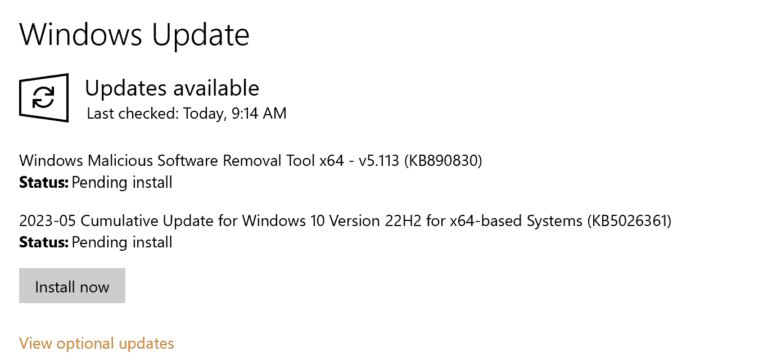
Among the addressed vulnerabilities, one has been detected under active exploitation in the wild: CVE-2023-29336

AndoryuBot botnet targets the Ruckus vulnerability to access devices, subsequently downloading a script for further propagation
CVE-2023-32233 has been discovered in the Linux kernel, which allows local authenticated users to escalate their privileges on the system.

The CVE-2023-30237 vulnerability was addressed in the 8.3.10.10015 version of CyberGhost, released on February 24, 2023

The flaw in question, CVE-2023-31039, has been classified as "important" in terms of severity and affects Apache bRPC versions 0.9.0 through 1.4.9
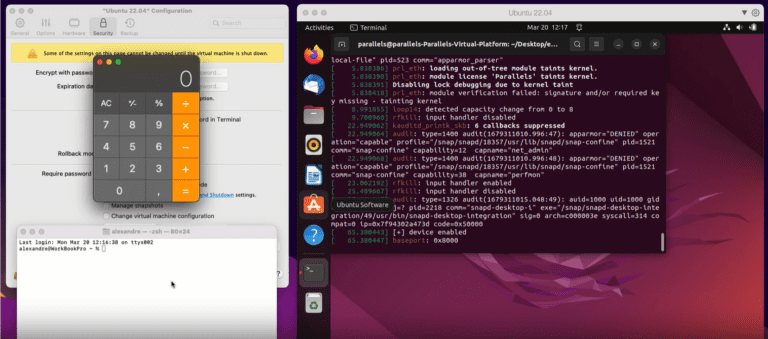
Malwareman007 released a PoC exploit for the CVE-2023-27326 vulnerability. The exploit was tested on Parallels Desktop version 18.0.0.

With a high CVSS score of 9.6, the CVE-2023-2478 vulnerability poses a serious risk to the integrity and security of GitLab projects.

Researcher Xkaneiki developed a PoC exploit for this vulnerability, demonstrating the potential risks posed by CVE-2023-0386

Malicious actors could exploit the CVE-2023-30777 vulnerability by manipulating the $this->view variable from the current_screen function

A recent scholarly article elucidates vulnerabilities called 'faulTPM' within AMD SoCs that could enable attackers to neutralize any security
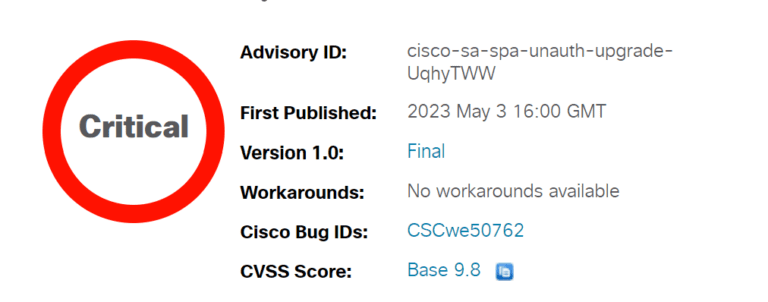
CVE-2023-20126 affects Cisco SPA112 2-Port Phone Adapters and allows an attacker to execute arbitrary code on affected devices.

CVE-2022-46718, a logic issue affecting Apple's iOS, enables unauthorized applications to access users' sensitive location information