
 Do Son
Microsoft's security division today unveiled the intricate details of the CVE-2023-32369 vulnerability, dubbed Migraine
Vulnerability
the discovery of an Unauthenticated PHP Object Injection vulnerability, with a CVE score of 8.3 and marked as CVE-2023-28782

The implications of CVE-2023-2650 are more pronounced in specific OpenSSL subsystems such as OCSP, PKCS7/SMIME, CMS, CMP/CRMF, and TS
The vulnerability, CVE-2023-30601, raises an alarming concern: privilege escalation when enabling Full Query Logging (FQL) or Audit logs

The vulnerability tracked as CVE-2023-2868 and boasting a worrisome CVSS score of 9.4, allows attackers to remotely execute system commands

CVE-2023-0950: Array Index Underflow in Calc Formula Parsing. The risk of arbitrary code execution - a major security concern - escalates

Vitellozzo, a security expert from the cybersecurity firm Occamsec, has released a PoC detailing how the CVE-2023-2825 flaw can be exploited

Utilizing several vulnerabilities, IZ1H9 poses a serious threat, taking full control of compromised devices to form part of its botnet.

Identified as CVE-2023-2732 and assigned a troubling Common Vulnerability Scoring System (CVSS) score of 9.8

The vulnerabilities, assigned the labels CVE-2023-33009 and CVE-2023-33010, both carry an alarming CVSS score of 9.8

CVE-2023-2825 is a path traversal vulnerability that enables an unauthenticated user to read arbitrary files on the server.

CVE-2023-32692 (CVSS score of 9.8) is a Remote Code Execution (RCE) vulnerability within CodeIgniter's Validation Placeholders.

This vulnerability tracked as CVE-2023-33246, revolves around the potential for RCE when utilizing the update configuration function

Google has now declared the initiation of a novel reward scheme for the discovery of vulnerabilities within a selection of its own Android applications
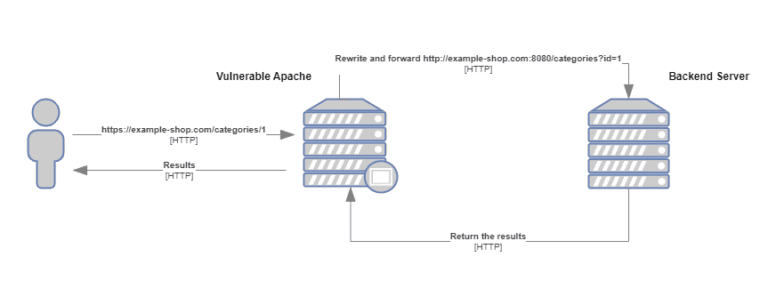
DSkfunk not only shared a proof of concept (PoC) for the CVE-2023-25690 vulnerability but also published an in-depth write-up

CVE-2023-31457 and CVE-2023-32748 have a Common Vulnerability Scoring System (CVSS) score of 9.6, highlighting the gravity of the situation
The CVE-2023-32960 vulnerability could lead to a more insidious Stored Site-Wide Cross-Site Scripting (XSS) attack on the wp-admin area

PoC exploit code has been made available for the CVE-2023-21554 bug, making it imperative that users move quickly to apply the patches

The CVE-2023-20883 vulnerability could trigger a DoS attack when Spring MVC is used along with a reverse proxy cache
CVE-2023-32409, a flaw that, quite alarmingly, allowed a remote attacker to break free from the confines of the Web Content sandbox
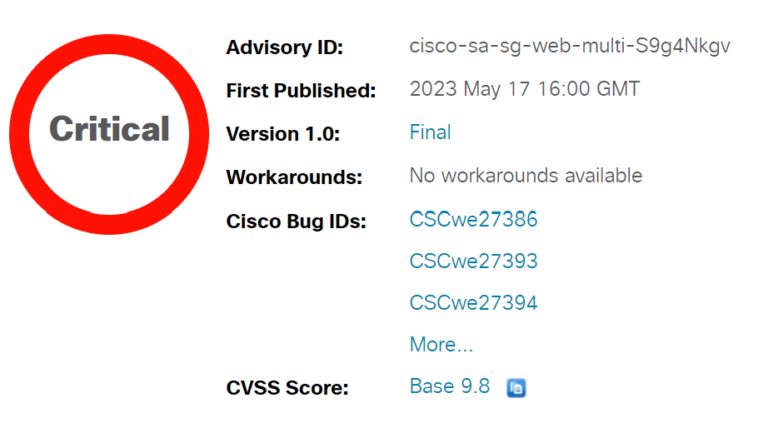
CVE-2023-20159 vulnerability stems from a security hole in the web-based user interface of the Cisco Small Business Series Switches.
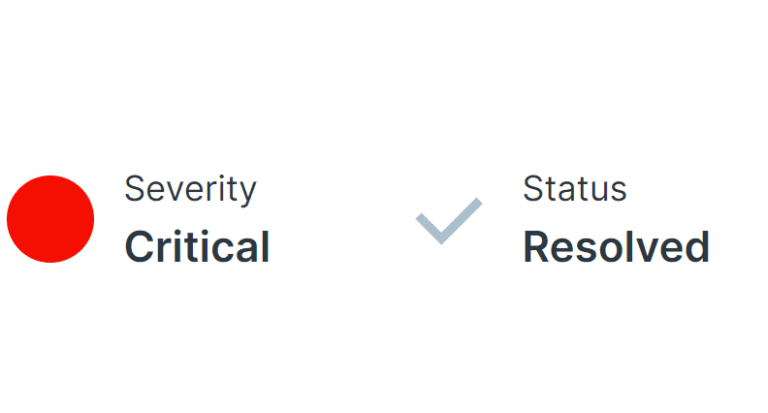
CVE-2023-32956 is ranked as critical with a CVSS3 Base Score of 9.8. It is an OS Command Injection flaw found in the CGI component of SRM