
 Do Son
Researcheruncovered a privilege escalation vulnerability (CVE-2023-30869) in the Easy Digital Downloads plugin versions 3.1.1.4.1 and below
Vulnerability
The CVE-2023-21839 vulnerability affects the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core)

CVE-2023-2356 (CVSS score of 10) allows attackers to access local server files on tracking server through a relative path traversal exploit

CVE-2023-30847 leads to invalid memory reads in proxy handler, which causes crashes, leaks of sensitive information to backend HTTP servers
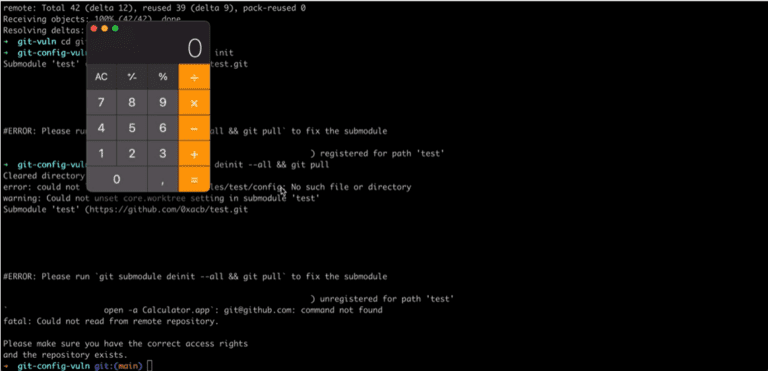
The impact of the CVE-2023-29007 vulnerability is substantial, as it can lead to arbitrary code execution by injecting values for executables
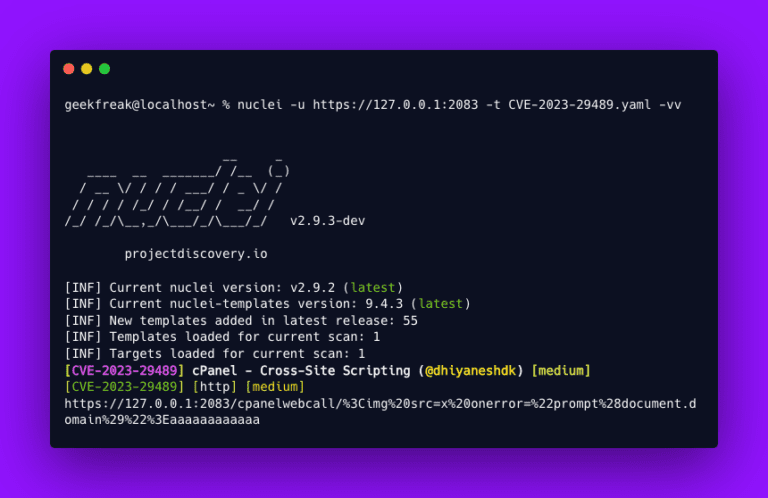
CVE-2023-29489 can be exploited without any authentication and affects even cPanel management ports that are not exposed externally

VMware Workstation and Fusion contain a critical stack-based buffer-overflow CVE-2023-20869 vulnerability (CVSSv3 base score of 9.3

CVE-2023-30839 allows a back-office user to write, update, and delete data in the database without having the necessary permissions.

The swift exploitation of CVE-2023-1389 by the Mirai botnet underscores the decreasing "time-to-exploit" speed observed

The Proof-of-Concept (PoC) for CVE-2023-1671, now available on Github, demonstrates how the vulnerability can be exploited

A recently discovered security vulnerability, CVE-2023-28771, has raised major concerns among network experts due to its CVSS score of 9.8
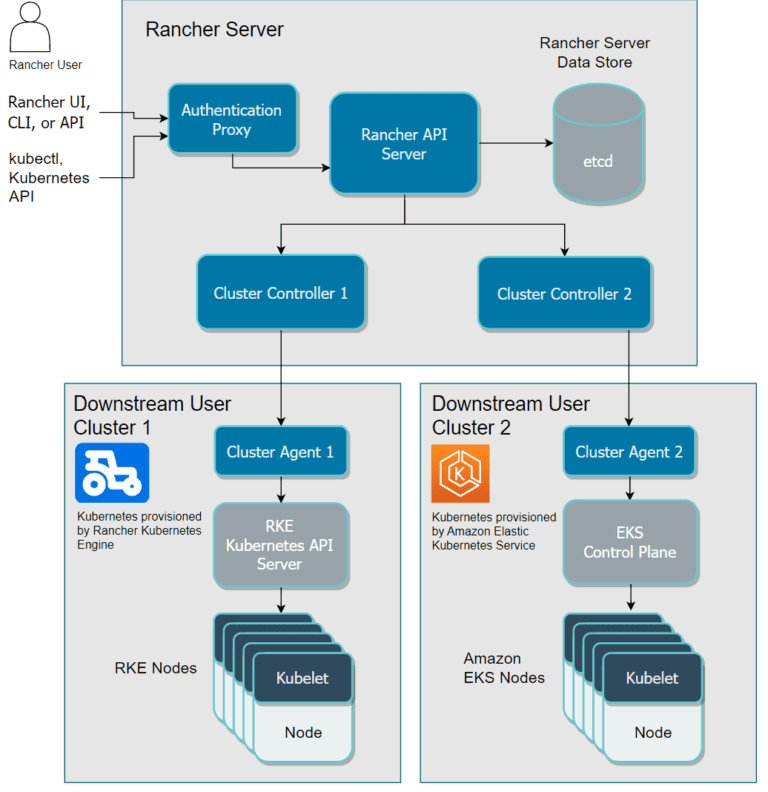
The root of CVE-2023-22651 lies in Rancher's admission Webhook, a component responsible for enforcing validation rules and security checks

Speculative execution side-channel flaws are security issues present in modern processors; they have been resolved in new Intel processors
Attackers can leverage the CVE-2023-27350 vulnerability to bypass authentication, execute arbitrary code in the context of SYSTEM

An unauthenticated hacker with network access to VMware Aria Operations for Logs may exploit CVE-2023-20864 to execute arbitrary code as root

CVE-2023-20873 affects multiple versions of Spring Boot, specifically 3.0.0 - 3.0.5, 2.7.0 - 2.7.10, and older unsupported versions

NVIDIA has released a security update for its DGX-1 firmware, addressing six vulnerabilities that may lead to issues such as arbitrary code execution
Attackers can exploit the CVE-2023-20046 vulnerability by sending a valid low-privileged SSH key to an affected device from a host configured

CVE-2023-20036 is present in the web UI of Cisco IND and allows an authenticated, remote attacker to execute arbitrary commands
two critical security vulnerabilities have been discovered in PaperCut MF and PaperCut NG, which are currently being exploited in the wild
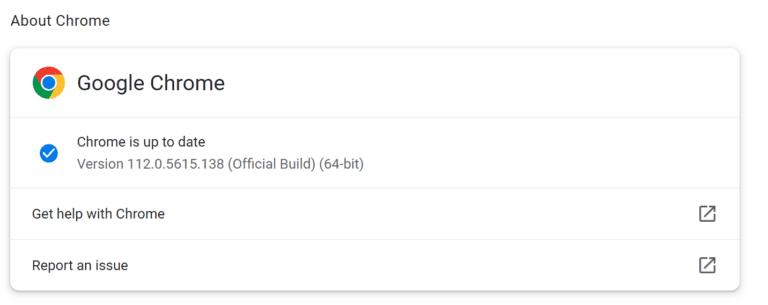
It's important to note that Google has acknowledged the existence of an exploit for CVE-2023-2136 in the wild.

the Citizen Lab discovered a series of zero-click exploit chains developed by the NSO Group, targeting iOS 15 and iOS 16 devices worldwide