Technical Details and PoC Exploit Published for Critical Drupal Field UI RCE (CVE-2026-108097)
 Do Son
TL;DR
FORTBRIDGE researcher Adrian Tiron has published a full technical analysis and lab exploit code for CVE-2026-108097, a critical Drupal RCE vulnerability in the Field UI module. Drupal patched the flaw on October 14, 2026, in advisory SA-CORE-2026-014. Sites should update to 11.4.10, 11.3.19 or 10.6.19.
Why It Matters
The code behind this Drupal RCE vulnerability ships in every affected install. Drupal rates it Critical, 19 out of 25, and warns that “multiple serious exploit paths exist with contributed modules.” The advisory adds: “At least one known exploit path does not require authentication.”
Exploit details now public
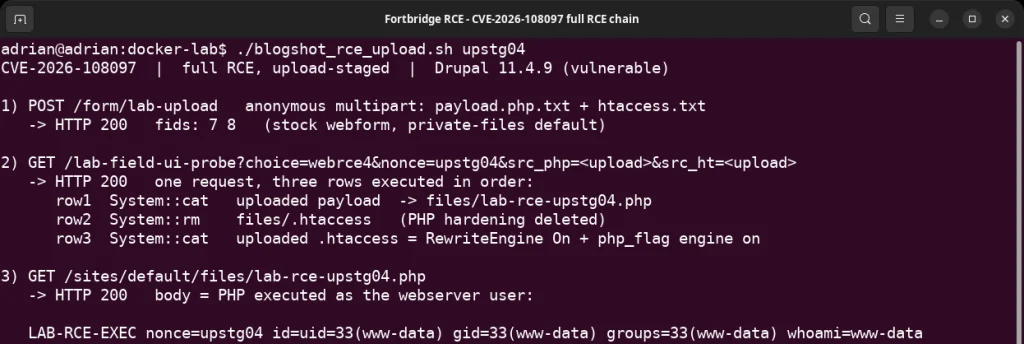
FORTBRIDGE rebuilt the full chain in its CVE-2026-108097 deep dive. The team also released its research code on GitHub. In its lab, the chain moved from file disclosure to full command execution, all without logging in.
How the Attack Works
A single line in Field UI runs whatever PHP callable a table row names. FORTBRIDGE explains that the code “treats one field of that data as code.” However, Drupal core alone cannot reach that line from outside. An attacker also needs a module that passes request data into those rows.
That is the catch. FORTBRIDGE used a lab-only bridge module to fill that gap, and it found no public module that does so today. The only known one, Entity List, was fixed separately. As a result, real exposure likely lies in custom code.
Exploitation status
A public PoC chain exists, but it relies on a synthetic module. No exploitation in the wild has been confirmed, and CISA has not listed the flaw.
Affected Versions
This Drupal RCE vulnerability affects Drupal 8.9.0 through 10.6.18, 11.0.0 through 11.3.18, 11.4.0 through 11.4.9, and 12.0.0 pre-releases before beta2.
Patch and Mitigation Steps
- Update to Drupal 11.4.10, 11.3.19 or 10.6.19. The fix removes the vulnerable line.
- If you cannot update, uninstall the Field UI module.
- Audit custom modules for code that feeds request data into Field UI tables.
- Alert on changes to the files directory and its .htaccess file.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
