Skip to content
October 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Microsoft Pushes Passwordless: New Accounts Default to Passkeys & MFA
  • Technology

Microsoft Pushes Passwordless: New Accounts Default to Passkeys & MFA

Do Son May 2, 2025 2 minutes read
0
Passwordless login, Microsoft accounts
Add Daily CyberSecurity as a preferred source on Google

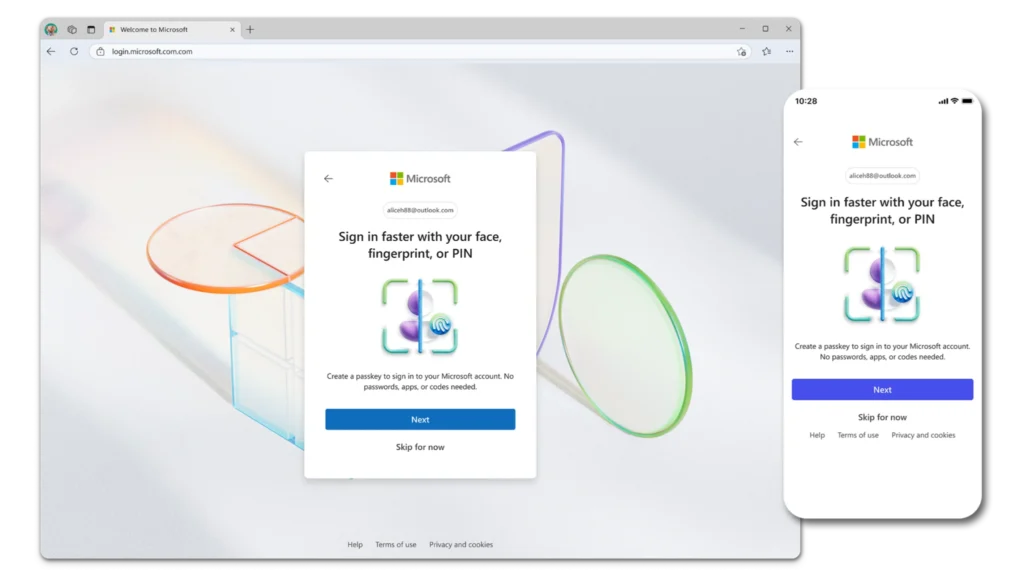
Microsoft is currently encouraging users to transition from traditional passwords to more secure authentication methods, such as passkeys and multi-factor authentication (MFA). For instance, a Microsoft account can be configured without a password, relying entirely on passkeys or MFA for login. Nevertheless, the majority of users still prefer signing in with conventional passwords.

To further this transition, Microsoft plans to revise its account registration process so that, by default, new accounts will no longer require the creation of a password. Instead, users will be prompted to select either a passkey or MFA as their primary authentication method. For those who still wish to use a password, Microsoft will offer the option to set one manually.

In preparation for this change, Microsoft will also enhance the login experience by defaulting to passkey and MFA authentication during sign-in, thereby bypassing the traditional password input field altogether.

Currently, Microsoft offers several sign-in options:

  • Logging in with a traditional password, often followed by an additional layer of passkey or MFA verification
  • Signing in directly using a passkey, with no further verification required
  • Generating a login request via the Microsoft Authenticator app, also requiring no additional verification

Once these changes are implemented, accounts already linked with a passkey or Microsoft Authenticator will default to these methods. In such cases, users may no longer see a password prompt at all and can complete the login process within seconds.

Some Microsoft applications or systems may not yet support passkey or MFA-based sign-ins. In these instances, users will still need to authenticate using a password. However, this is not the Microsoft account password itself, but rather a specially generated app-specific password. These passwords are distinct from your main credentials and are created exclusively for use in legacy applications that lack modern authentication support.

In essence, removing your Microsoft account password has no adverse effect, as these special-use cases always require an app-specific password regardless. Should you encounter such a need, you can obtain an app-specific password here.

Related Posts:

  • Passkeys: Microsoft’s Solution to 7,000 Password Attacks Per Second
  • Google Password Manager Adds Passkeys, Future Export Teased
  • FIDO Alliance Unveils New Draft Specifications for Secure Credential Exchange

Related coverage

  • Google Selfie Video Sign-In Recovers Locked Accounts
  • The 13-Year Lifeline: Apple Updates the iPhone 5s to Save iMessage
  • OpenAI Expands Beyond Microsoft: Google Cloud Joins Forces to Power ChatGPT and AI Growth
  • Chrome and Firefox browsers will further reduce the use of memory
  • The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer
  • Critical PCIe 6.0 Flaws Risk Secure Data Integrity via Stale Data Injection in IDE Mechanism
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS Β· Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Account Security authentication Login MFA Microsoft Multi-Factor Authentication Passkeys Passwordless

Leave a Reply Cancel reply

You must be logged in to post a comment.

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-104803CVSS 9.8
    The WPCOM Member plugin for WordPress is vulnerable to Authentication Bypass in all versions up to, and including,...
    📅 Updated: Oct 10, 2026
  • CVE-2026-104801CVSS 9.1
    The PPOM – Product Addons & Custom Fields for WooCommerce plugin for WordPress is vulnerable to arbitrary file...
    📅 Updated: Oct 10, 2026
  • CVE-2026-62045CVSS 9.8
    Deserialization of Untrusted Data vulnerability in ThemeREX Group Booklovers booklovers allows Object Injection.This issue affects Booklovers: from n/a...
    📅 Updated: Oct 10, 2026
  • CVE-2026-62046CVSS 9.8
    Deserialization of Untrusted Data vulnerability in ThemeREX Group Gutentype gutentype allows Object Injection.This issue affects Gutentype: from n/a...
    📅 Updated: Oct 10, 2026
  • CVE-2026-93942CVSS 9.8
    Deserialization of Untrusted Data vulnerability in ThemeREX Group Dwell dwell allows Object Injection.This issue affects Dwell: from n/a...
    📅 Updated: Oct 10, 2026
  • CVE-2026-93943CVSS 9.8
    Deserialization of Untrusted Data vulnerability in ThemeREX Group Convex convex allows Object Injection.This issue affects Convex: from n/a...
    📅 Updated: Oct 10, 2026
  • CVE-2026-93944CVSS 9.8
    Deserialization of Untrusted Data vulnerability in ThemeREX Group Camelia camelia allows Object Injection.This issue affects Camelia: from n/a...
    📅 Updated: Oct 10, 2026
  • CVE-2026-93945CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Axiomthemes Balance balance allows Object Injection.This issue affects Balance: from n/a through...
    📅 Updated: Oct 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.