Skip to content
November 13, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Malware
  • New attack uses Excel spreadsheets to launch the malware Loki Bot
  • Malware

New attack uses Excel spreadsheets to launch the malware Loki Bot

Do Son December 26, 2017 3 minutes read
Malware Loki Bot

Cybersecurity company Lastline discovered a new attack technology that leverages Office Excel spreadsheets in early December 2017 and has just recently expanded to include other Office applications. The researchers discovered a new type of malicious Office Excel file that downloads and executes malware without any clues to macros, shellcode or DDE code. And when the researchers scanned the files submitted to Virustotal, a website that offers free suspicious file analysis services, only three anti-virus software defined it as malicious, so this is a new attack technique for Excel spreadsheets.

Attack and Payload

When the user opens the Excel file, a dialog box will pop up saying:

External links

Is a feature of Microsoft Office that allows authors to share Office documents through external resource links without having to embed those resources directly into the document, making the entire document smaller, newer and more flexible.

From this perspective, this attack appears to be very similar to the DDE attack, which is the more popular Office File Utilization technology used to execute external code through Microsoft’s Dynamic Data Exchange facility.

Once the user agrees to update the link, the document immediately creates a cmd / PowerShell process that downloads and executes the next phase payload (exe file): Execute malware.

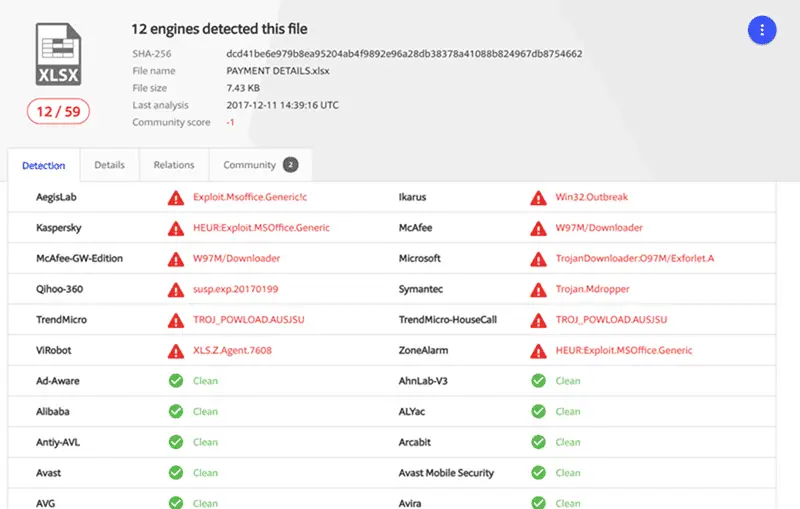
Since only three software detected such attacks, even scanning for an Excel infection was considered a false positive and may not be further investigated or remedied. The researchers confirmed that the payload sent by the Excel script was Loki, a notorious “document stealing” malware.

Figure B: Twelve days after initial detection, 12 AV tools detected this threat

For most security response teams, this is a double blow. First, the low detection rate makes the security team think it is false positives. Second, even if they discovered Loki, the mitigation was often mistakenly implemented. When subsequent threat attackers use the leaked credentials to gain unauthorized access and attempt to move laterally, the victim is vulnerable to a second “no malware” attack.

The researchers submitted the malicious Excel script to Virustotal on December 10 and 12 of 60 anti-virus tools detected it as a threat. After the log tracing found a file named “_output23476823784.exe”, about 50% of the detection engines identified the file as a malicious file.
Most anti-virus programs mark _output23476823784.exe Payload as a Trojan, which indicates that it is a Trojan.Generic Payload.

The real body of this Payload: Malware Loki Bot

Behavioral Intelligence further identifies the dubious Payload as a Loki bot.

Figure G: Dark Market Ad

Loki’s promotional videos show that it can capture vouchers for a variety of applications, especially FireFox (47% stolen documents) and Chrome (41%), while Windows and email vouchers account for just 1% -3%.

Figure I: Vulnerable websites as per Loki

Once the victim’s voucher has been stolen, Loki shows vulnerable sites for identity theft, including social media sites, payment portals, bitcoin wallets, and even a Moroccan government login page.

Malware LokiBot

In November 2017, “LokiBot”, a malicious software evolved from “BankBot,” is known as the first “Transformers” Android malware because “LokiBot” has its own unique features compared to other bank hijackings, Which can initiate attacks according to different target environments, such as initiating interface hijacking to user equipment, encrypting user equipment data, extorting money from users, establishing socks5 proxy and SSH tunnel, and infiltrating intranet data.

“LokiBot” Spreads The user’s installation was induced through malicious updates such as “Adobe Flash Playe”, “APK Installer”, “System Update”, “Adblock”, “Security Certificate” and other application updates.

Reference: lastline

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • New Melofee Backdoor Variant Targets Linux Systems with Advanced Stealth Tactics
  • NCC Group Reports: September’s Alarming Ransomware Spike
  • Warning: Xubuntu Website Compromised to Deliver Malware
  • NGate Android Malware Steals NFC Payment Data at ATMs
  • Cybercriminal on Cybercriminal Crime: Ransomware Hijacks CoinMiner
  • Earth Longzhi’s Cyber Attack: New Techniques Target Asia-Pacific Organizations
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Malware LokiBot

🚨 Active Exploits in the Wild

  • CVE-2026-123039CVSS 7.8
    The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating...
    Admin intel📅 Updated: Nov 12, 2026
  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-75491CVSS 9.2
    Cudy TR3000 before 2.5.42 contains an authentication bypass vulnerability in the Mosquitto plugin auth_plugin_jwt.so that accepts unsigned JWTs...
    📅 Updated: Nov 13, 2026
  • CVE-2026-75495CVSS 9.2
    Cudy TR3000 before 2.5.42 contains an OS command injection vulnerability that allows a malicious or compromised ACS to...
    📅 Updated: Nov 13, 2026
  • CVE-2026-126265CVSS 9.1
    SiYuan 2.1.0 before 3.8.9 contains a flaw where the loginAuth CAPTCHA challenge lives in a signed client-side cookie,...
    📅 Updated: Nov 13, 2026
  • CVE-2026-126269CVSS 9.3
    NocoDB before 2026.09.0 contains a stored cross-site scripting vulnerability that allows authenticated Editor users to execute scripts by...
    📅 Updated: Nov 13, 2026
  • CVE-2026-126273CVSS 9.2
    NocoDB before 2026.09.0 contains a privilege escalation vulnerability in initAdminFromEnv.ts that silently skips super-admin bootstrap when the admin...
    📅 Updated: Nov 13, 2026
  • CVE-2026-126274CVSS 9.3
    NocoDB before 2026.08.0 contains a stored cross-site scripting vulnerability that allows authenticated Creator users to inject script by...
    📅 Updated: Nov 13, 2026
  • CVE-2026-126280CVSS 9.1
    NocoDB before 2026.08.0 contains a race condition in refresh-token rotation that allows attackers to reuse tokens because UserRefreshToken.ts...
    📅 Updated: Nov 13, 2026
  • CVE-2026-126315CVSS 9.3
    Frappe HRMS 16.14.0 before 16.20.1 sends product usage events on certain HR transactions without checking the site's telemetry...
    📅 Updated: Nov 13, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.