
 Do Son
Three Tornado security vulnerabilities (CVE-2026-49853, CVE-2026-49855, CVE-2026-49854) risk credential leaks and DoS. Update to Tornado 6.5.6 now.
A critical Vitest RCE vulnerability (CVE-2026-53633, CVSS 9.8) has public PoC code. Browser Mode flaw enables config overwrite and remote code execution.
A Haskell TLS vulnerability (CVE-2026-9648) lets attackers bypass X.509 NameConstraints to impersonate domains. Update crypton-x509-validation to 1.9.1.

CISA warns of 7 Naxclow IoT vulnerabilities, including a hard-coded key (CVE-2026-28742) enabling device takeover of doorbells and cameras.

Two pre-auth FreeSWITCH heap buffer overflow bugs (CVE-2026-49841, CVE-2026-49840) hit mod_verto and libesl. Update to v1.11.1 to stay safe.

A critical phpBB authentication bypass (CVE-2026-48611) lets attackers hijack any account on thousands of forums. Update to 3.3.17 now.

Gone are the days when managing personal finances required a weekly trip to a local bank branch...

CVE-2026-54420, a LiteSpeed cPanel privilege escalation flaw, is exploited in the wild to gain root on shared hosting. Patch to plugin v2.4.8 now.
Cisco warns CVE-2026-20262, a Cisco SD-WAN vulnerability enabling arbitrary file write, is exploited in the wild. Patch SD-WAN Manager now.
The Uncanny Automator breach exposed customer data and pushed a backdoored plugin build (7.3.0.5). Here's what happened and how to secure your site.
Compare the best encrypted cloud storage for ransomware defense — zero-knowledge encryption, versioning and pricing for Internxt, Proton, Tresorit and more.

Discover how UCSD and Google are pioneering low carbon cloud computing by transforming retired smartphones into powerful, eco-friendly data centers.

A Jenkins RCE vulnerability (CVE-2026-53435) is under active exploitation. Honeypots are seeing attacks now, so patch your Jenkins controller fast.

Plumbing issues can disrupt the comfort and functionality of your home, often requiring immediate attention to prevent...

Howler Cell exposes an X-VPN DLL sideloading campaign delivering STX RAT via 11 trojanized installers targeting crypto and VPN users.

Firefox's built-in VPN removes its 50GB cap and adds 22 new countries this summer, helping travelers stream and browse securely.

ReliaQuest uncovers OP-512, a China-linked cluster using a unique IIS web shell framework with RSA/RC4 encryption and timestomping.

Mandiant details the UNC3753 vishing campaign targeting US law firms with fake IT calls, RMM abuse, and rapid data theft extortion.
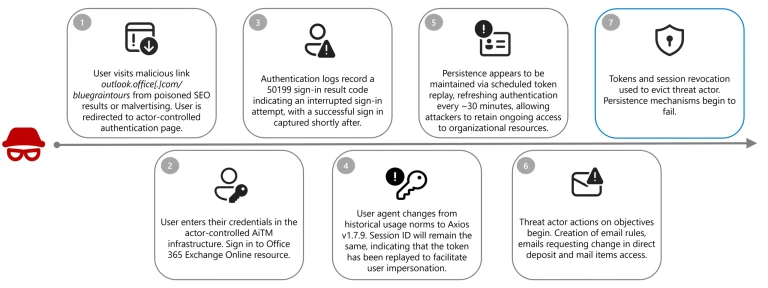
The active Payroll Pirate campaign uses AiTM session hijacking and token replay to target corporate payroll and HR personnel across multiple industries.
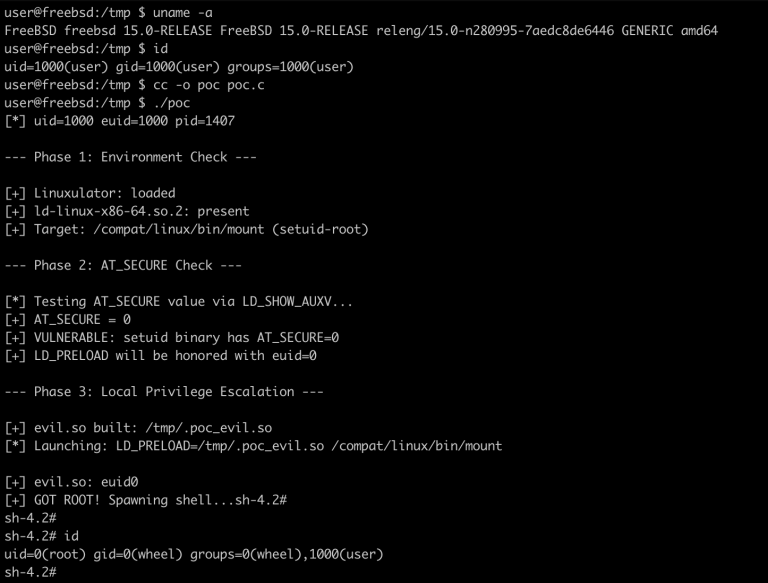
A FreeBSD privilege escalation flaw (CVE-2026-49413) in the Linuxulator lets local users get root. Public PoC exploit code makes patching urgent.

Two critical FreePBX RCE vulnerabilities in Superfecta and UCP modules expose servers to authenticated arbitrary code execution and command injection.

Use our Anthropic Claude refund guide to navigate the recent export ban. Discover eligibility rules, prorated details, and hidden Apple IAP risks.