Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
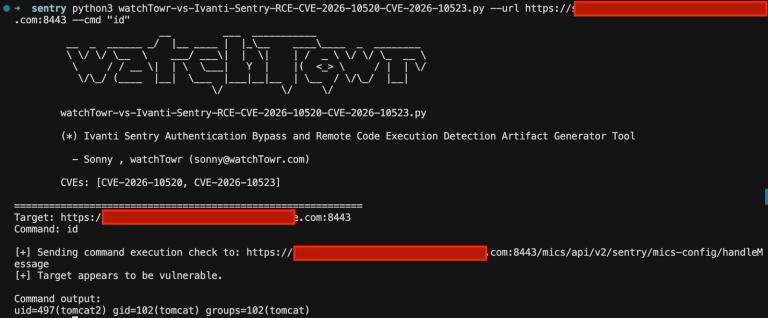
Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10 Ivanti Sentry RCE publicly disclosed PoC
  • Vulnerability Report

Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10

Do Son June 10, 2026 0

Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.

OpenSSL Security Patches Fix Remote Code Execution Risk CVE-2022-3602 OpenSSL security patches remote code execution risk
  • Vulnerability Report

OpenSSL Security Patches Fix Remote Code Execution Risk

Do Son June 10, 2026 0

New OpenSSL security patches address a critical use-after-free bug that introduces an immediate remote code execution risk across enterprise systems.

New Microsoft Defender Zero Day Exploit Released Publicly Online Defender zero day exploit race condition vulnerability
  • Vulnerability Report

New Microsoft Defender Zero Day Exploit Released Publicly Online

Do Son June 10, 2026 0

A new Microsoft Defender zero day exploit leaks online, exposing a severe race condition vulnerability affecting fully patched Windows installations.
CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws

Do Son June 10, 2026 0

The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws

Do Son June 10, 2026 0

Deploy the latest Microsoft Patch Tuesday fixes. The June release addresses severe zero day vulnerabilities and over thirty critical flaws.

High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile Ivanti EPMM security updates Ivanti ITSM vulnerability authenticated privilege escalation Ivanti Xtraction vulnerability CVE-2026-8043 Ivanti EPM RCE, SQL Injection Ivanti EPM, remote code execution CVE-2024-50330 - CVE-2025-0282 and CVE-2025-0283
  • Vulnerability Report

High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile

Do Son June 10, 2026 0

New Ivanti EPMM security updates address high-severity flaws that could allow a remote authenticated attacker to achieve remote code execution.

Critical Rclone Command Execution Bug Threatens Cloud Environments rclone command execution execute local commands Rclone RCE CVE-2026-41176
  • Vulnerability Report

Critical Rclone Command Execution Bug Threatens Cloud Environments

Do Son June 10, 2026 0

A critical rclone command execution flaw allows users to execute local commands. Secure your cloud synchronization setup against this risk.

Critical Veeam Backup Vulnerability Exposed Veeam Backup vulnerability remote code execution Veeam Backup vulnerability Veeam Vulnerabilities CVE-2024-42448 & CVE-2024-42449
  • Vulnerability Report

Critical Veeam Backup Vulnerability Exposed

Do Son June 10, 2026 0

A critical Veeam Backup vulnerability allows remote code execution. Secure your domain-joined systems by upgrading to the latest build immediately.

Critical FortiSandbox Flaw Requires Immediate Patching CVE-2026-25089 CVE-2023-45590
  • Vulnerability Report

Critical FortiSandbox Flaw Requires Immediate Patching

Do Son June 10, 2026 0

An urgent patch fixes the critical CVE-2026-25089 FortiSandbox bug. Attackers can execute remote commands, so update your systems immediately.

Critical TinyMCE Cross Site Scripting Flaws Threaten Millions of Applications TinyMCE cross site scripting stored XSS vulnerability
  • Vulnerability Report

Critical TinyMCE Cross Site Scripting Flaws Threaten Millions of Applications

Do Son June 10, 2026 0

A major TinyMCE cross site scripting threat is uncovered. Patch this critical stored XSS vulnerability by updating your rich text editor now.
MBS Universal Gateway Flaws Threaten Building Automation Networks Haskell TLS vulnerability CVE-2026-9648, X.509 NameConstraints, crypton-x509-validation MBS Universal Gateway flaws stack buffer overflow bugs SystemLink authentication bypass privilege escalation bug Cache Warmer RCE flaw Magento PHP object injection
  • Vulnerability Report

MBS Universal Gateway Flaws Threaten Building Automation Networks

Do Son June 10, 2026 0

Multiple MBS Universal Gateway flaws, including stack buffer overflow bugs and default passwords, expose building automation networks. Patch now.

Spring Framework Security Vulnerabilities Addressed in Critical Maintenance Updates Spring framework security vulnerabilities authentication bypass threat
  • Vulnerability Report

Spring Framework Security Vulnerabilities Addressed in Critical Maintenance Updates

Do Son June 9, 2026 0

New updates address multiple Spring framework security vulnerabilities, resolving a critical authentication bypass threat and several denial of service bugs.

New MagicAd Android Trojan Bypasses OS Restrictions to Flood Devices with Ads MagicAd Android trojan GetApps malware distribution
  • Malware

New MagicAd Android Trojan Bypasses OS Restrictions to Flood Devices with Ads

Do Son June 9, 2026 0

Read how the MagicAd Android trojan exploits GetApps malware distribution networks to run background advertisements without user consent.

Strategic Value: Google Slashes AI Plus Subscription Fees While Doubling Storage Google AI Plus subscription
  • Technology

Strategic Value: Google Slashes AI Plus Subscription Fees While Doubling Storage

Do Son June 9, 2026 0

Discover the new Google AI Plus subscription price drop to $4.99. Learn about the double 400GB cloud storage upgrade and new Gemini features.

Decentralized Diffusion: Z-Library Upgrades Mirror Infrastructure to Evade Seizures Z-Library mirror network
  • Technology

Decentralized Diffusion: Z-Library Upgrades Mirror Infrastructure to Evade Seizures

Do Son June 9, 2026 0

Discover the new Z-Library mirror network. Learn how white-label satellite sites fight domain seizures and pay a twenty percent crypto dividend.

Structured Expiration: Microsoft Enforces Comprehensive Lifecycle Management for OneDrive OneDrive data retention policy
  • Technology

Structured Expiration: Microsoft Enforces Comprehensive Lifecycle Management for OneDrive

Do Son June 9, 2026 0

Discover the new OneDrive data retention policy hitting teams in July 2026. Learn how Microsoft purges unlicensed user accounts and files.

Malicious Traffic Routing Stack Exploited to Spread Global Malware malicious traffic routing Check Point research report
  • Malware

Malicious Traffic Routing Stack Exploited to Spread Global Malware

Do Son June 9, 2026 0

Discover how malicious traffic routing hijacks open-source downloads in this new Check Point research report on global malware distribution.

Argamal Trojan Campaign Targets Adult Gamers with COM Hijacking Argamal Trojan campaign Kaspersky malware analysis
  • Malware

Argamal Trojan Campaign Targets Adult Gamers with COM Hijacking

Do Son June 9, 2026 0

Read the Kaspersky malware analysis revealing how the Argamal Trojan campaign targets adult gamers using stealthy COM hijacking.

SAP Security Patch Day: Critical Security Vulnerabilities Remediated SAP security patch day critical security vulnerabilities SAP SQL Injection April 2026 Patch Day SAP Security, Critical Vulnerabilities Security Patch Day CVE-2025-42944
  • Vulnerability Report

SAP Security Patch Day: Critical Security Vulnerabilities Remediated

Do Son June 9, 2026 0

The latest SAP security patch day addresses critical security vulnerabilities. Learn about the four high-impact flaws and protect your systems today.

Sophisticated TA4922 Cybercrime Operations Expand Globally Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

Sophisticated TA4922 Cybercrime Operations Expand Globally

Do Son June 9, 2026 0

Read this Proofpoint cybercrime analysis on the surge of TA4922 malware campaigns targeting organizations globally with advanced evasion tactics.

Seamless Interoperability: Apple Notes Optimizes Markdown Integration in iOS 27 Apple Notes Markdown support
  • Technology

Seamless Interoperability: Apple Notes Optimizes Markdown Integration in iOS 27

Do Son June 9, 2026 0

Discover the upgraded Apple Notes Markdown support in iOS 27. Learn how clipboard parsing transforms raw markdown text into rich text instantly.

Market Shockwave: OpenAI Confidentially Files for Historic Public Offering OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

Market Shockwave: OpenAI Confidentially Files for Historic Public Offering

Do Son June 9, 2026 0

Discover the OpenAI confidential IPO filing details. Learn how the tech giant targets a $1 trillion valuation alongside Anthropic and SpaceX in 2026.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105604CVSS 9.3
    Joomla Extension - dj-extensions.com - Unauthenticated SQL injection in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds is...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91299CVSS 10.0
    Vulnerability in the JD Edwards EnterpriseOne Orchestrator product of Oracle JD Edwards (component: E1 IOT Orchestrator Security). Supported...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91305CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). Supported versions that...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119706CVSS 9.3
    InternLM LMDeploy 0.9.0 through 0.18.0 contains an unauthenticated remote code execution vulnerability that allows remote attackers to run...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105603CVSS 9.4
    Joomla Extension - dj-extensions.com - Authenticated arbitrary file upload in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds...
    📅 Updated: Nov 2, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.