Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Automated Fortification: iOS 27 Introduces AI-Driven Password Rectification WWDC 2026 iOS 27
  • Technology

Automated Fortification: iOS 27 Introduces AI-Driven Password Rectification

Do Son June 9, 2026 0

Discover the new iOS 27 password reset feature. Learn how Apple Intelligence automatically fixes compromised credentials in the background via Safari.

Critical Kemp LoadMaster Flaws Expose Network Appliances to RCE Kemp LoadMaster flaws command injection remote execution Kemp LoadMaster Vulnerability WAF Bypass Technique Progress WhatsUp Gold Vulnerabilities
  • Vulnerability Report

Critical Kemp LoadMaster Flaws Expose Network Appliances to RCE

Do Son June 9, 2026 0

Fix critical Kemp LoadMaster flaws today. Learn how a command injection remote execution vulnerability leaves application networks exposed.

Emergency Patch Release Secures Apache HTTP Server Deployments Against Remote Attacks Apache HTTP Server patches buffer overflow vulnerabilities CVE-2022-36760
  • Vulnerability Report

Emergency Patch Release Secures Apache HTTP Server Deployments Against Remote Attacks

Do Son June 9, 2026 0

New Apache HTTP Server patches resolve multiple buffer overflow vulnerabilities. Upgrade your production infrastructure immediately to keep deployments secure.

TP-Link Patches Critical Archer MR600 Command Injection Flaw Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

TP-Link Patches Critical Archer MR600 Command Injection Flaw

Do Son June 9, 2026 0

A critical Archer MR600 command injection vulnerability surfaces within the WireGuard client configuration. Update your TP-Link firmware now.

ABB Patches Critical T-MAC Plus Terminal System Flaws ABB T-MAC Plus vulnerabilities terminal system flaws ABB OPTIMAX Vulnerability CVE-2025-14510 ABB Edgenius Auth Bypass, Critical RCE ABB, ASPECT BMS CVE-2024-48841, CVE-2024-48849, and CVE-2024-48852 CVE-2024-48510
  • Vulnerability Report

ABB Patches Critical T-MAC Plus Terminal System Flaws

Do Son June 9, 2026 0

ABB addresses critical ABB T-MAC Plus vulnerabilities. Learn how these terminal system flaws allow authentication bypass and file disclosure.

Jupyter Gateway Vulnerabilities: Severe CVSS 10 Exploits Uncovered Jupyter Gateway vulnerabilities critical CVSS 10 flaws
  • Vulnerability Report

Jupyter Gateway Vulnerabilities: Severe CVSS 10 Exploits Uncovered

Do Son June 9, 2026 0

Read about new Jupyter Gateway vulnerabilities and critical CVSS 10 flaws that allow remote code execution and full Kubernetes cluster takeover.

Pragmatic Refinement: Apple Rebalances Aesthetics and Performance at WWDC 2026 Apple AirPort Utility deprecated notice on legacy wireless routers AFP protocol macOS 27, SMB3 protocol, Apple Filing Protocol, file sharing protocol Apple WWDC 2026 announcements
  • Technology

Pragmatic Refinement: Apple Rebalances Aesthetics and Performance at WWDC 2026

Do Son June 9, 2026 0

Discover the new Apple WWDC 2026 announcements. Learn about the refined Liquid Glass design, massive iOS 27 speed leaps, and macOS Golden Gate updates.

Sovereign Synthesis: Apple Unveils Gemini-Powered Siri AI and macOS Golden Gate Siri AI system prompt Siri AI iOS 27 Apple Siri URL summarization restriction interface in the iOS 27 beta update
  • Technology

Sovereign Synthesis: Apple Unveils Gemini-Powered Siri AI and macOS Golden Gate

Do Son June 9, 2026 0

Discover the new Siri AI iOS 27 features from WWDC 2026. Learn how the Google Gemini engine powers the standalone app and system tools.

Apache MINA Patches Critical Framework Vulnerabilities Apache MINA flaws critical deserialization bypass Apache MINA Deserialization CVE-2026-42778 RCE Apache MINA RCE CVE-2026-41635
  • Vulnerability Report

Apache MINA Patches Critical Framework Vulnerabilities

Do Son June 9, 2026 0

Fix dangerous Apache MINA flaws immediately. Learn how a critical deserialization bypass and a DoS vulnerability leave Java applications exposed.

New Chrome Security Update Addresses Critical V8 Exploit in the Wild Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

New Chrome Security Update Addresses Critical V8 Exploit in the Wild

Do Son June 9, 2026 0

Apply the new Chrome security update immediately. Google warns that a critical exploit in the wild targets a high-severity V8 engine flaw.

Deep Integration: Apple Intelligence Anchors iOS 27 and macOS 27 Default Application Suites Apple Intelligence WWDC 2026
  • Technology

Deep Integration: Apple Intelligence Anchors iOS 27 and macOS 27 Default Application Suites

Do Son June 9, 2026 0

Discover the new Apple Intelligence WWDC 2026 features. Learn how deep Siri upgrades, Safari tab automation, and iOS 27 tools change your daily workflow.

Sovereign Intelligence: Apple Reimagines Siri with Gemini Core Integration at WWDC 2026 Siri AI standalone app
  • Technology

Sovereign Intelligence: Apple Reimagines Siri with Gemini Core Integration at WWDC 2026

Do Son June 9, 2026 0

Discover the new Siri AI standalone app from WWDC 2026. Learn how the Google Gemini integration brings multimodal vision features to your devices.
Malicious PyPI Package Wave Spreads Evolving Supply Chain Attacks malicious PyPI package wave supply chain attacks
  • Malware

Malicious PyPI Package Wave Spreads Evolving Supply Chain Attacks

Do Son June 9, 2026 0

A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.

CISA Active Exploit Catalog Expands with Critical Gateway Flaws CISA active exploit catalog critical gateway flaws CVE-2023-27532 & CVE-2024-37383
  • Vulnerability Report

CISA Active Exploit Catalog Expands with Critical Gateway Flaws

Do Son June 9, 2026 0

CISA expands its active exploit catalog with critical gateway flaws in BerriAI LiteLLM and Check Point configurations. Patch immediately.

Accelerating Business Growth: 8 Tips and Considerations Andariel APT
  • Technique

Accelerating Business Growth: 8 Tips and Considerations

Do Son June 8, 2026 0
Growing your business is an exciting phase, but it needs to be approached strategically. Before you dive...
Read More Read more about Accelerating Business Growth: 8 Tips and Considerations
Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Vulnerability Report

Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links

Do Son June 8, 2026 0

A critical Check Point VPN vulnerability is actively exploited in the wild, allowing unauthenticated attackers to bypass user login requirements.

Best B2B Tech Marketing Agencies tech
  • Technique

Best B2B Tech Marketing Agencies

Do Son June 8, 2026 0
Complex B2B technology companies do not fail because they lack content. They fail because their go-to-market systems...
Read More Read more about Best B2B Tech Marketing Agencies
Cyber Espionage Campaign Targets Global Stock Exchange Executive AdaptixC2 Abuse, Russian Cybercrime RondoDox Botnet, Exploit Shotgun China Cyber Power, Red Hackers Nvidia cyberattack
  • Cybercriminals

Cyber Espionage Campaign Targets Global Stock Exchange Executive

Do Son June 8, 2026 0

Discover how stealthy Outlook mailbox theft fueled a 5-month executive espionage campaign at a global stock exchange using trusted cloud tools.

Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide Smishing Error524 campaign Group-IB phishing report
  • Cybercriminals

Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide

Do Son June 8, 2026 0

Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.

Instagram Account Recovery Flaw Exploited via AI Support Tool Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Data Leak

Instagram Account Recovery Flaw Exploited via AI Support Tool

Do Son June 8, 2026 0

A serious Instagram account recovery flaw has been exposed. Read this Meta incident notification detailing how AI-assisted bugs bypass security.
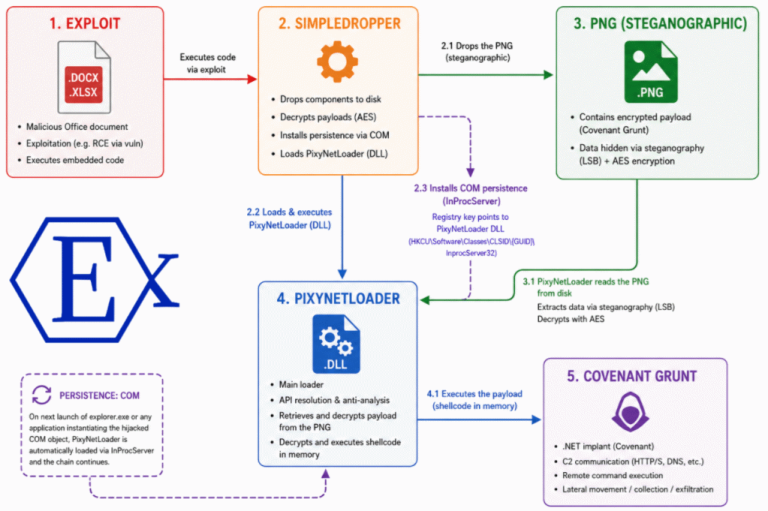
PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files PixyNetLoader malware analysis APT28 steganography attack
  • Malware

PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files

Do Son June 8, 2026 0

Researchers expose PixyNetLoader malware analysis revealing APT28's steganography APT28 attack, hiding Covenant Grunt payloads inside PNG pixels since 2024.

Redis DarkReplica Exploit: Full PoC Code and Technical Details Released CVE-2022-35951 Redis DarkReplica exploit CVE-2026-23631 public disclosure
  • Vulnerability

Redis DarkReplica Exploit: Full PoC Code and Technical Details Released

Do Son June 8, 2026 0

Full technical details and functional PoC code for the Redis DarkReplica exploit are out. Read our breakdown of this CVE-2026-23631 public disclosure.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105604CVSS 9.3
    Joomla Extension - dj-extensions.com - Unauthenticated SQL injection in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds is...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91299CVSS 10.0
    Vulnerability in the JD Edwards EnterpriseOne Orchestrator product of Oracle JD Edwards (component: E1 IOT Orchestrator Security). Supported...
    📅 Updated: Nov 2, 2026
  • CVE-2026-91305CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). Supported versions that...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119706CVSS 9.3
    InternLM LMDeploy 0.9.0 through 0.18.0 contains an unauthenticated remote code execution vulnerability that allows remote attackers to run...
    📅 Updated: Nov 2, 2026
  • CVE-2026-105603CVSS 9.4
    Joomla Extension - dj-extensions.com - Authenticated arbitrary file upload in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds...
    📅 Updated: Nov 2, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Nov 2, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.