Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
strongSwan CVE-2026-47895: Double-Free Exploit Explained libstrongswan double-free exploit strongSwan CVE-2026-47895 CVE-2023-41913 strongSwan Vulnerability VPN Denial of Service
  • Vulnerability Report

strongSwan CVE-2026-47895: Double-Free Exploit Explained

Do Son June 11, 2026 0

A new strongSwan CVE-2026-47895 vulnerability allows remote code execution via a libstrongswan double-free exploit. Patch your VPN servers now!

Spring Data Vulnerabilities: Patch Five Critical Flaws Now Spring Data vulnerabilities Spring Cloud Config CVE-2026-22739 Spring Gateway SpEL, STOMP WebSocket CSRF Spring Security, vulnerability CVE-2024-38819 CVE-2025-41243 Spring Cloud Gateway, vulnerability
  • Vulnerability Report

Spring Data Vulnerabilities: Patch Five Critical Flaws Now

Do Son June 11, 2026 0

Five new Spring Data vulnerabilities threaten applications with SpEL expression injection and DoS attacks. Upgrade your Spring frameworks immediately!
Critical UpdraftPlus CVE-2026-10795 Exploit Targets Millions UpdraftPlus CVE-2026-10795, UpdraftPlus authentication bypass, WordPress plugin vulnerability, CVE-2026-10795
  • Vulnerability Report

Critical UpdraftPlus CVE-2026-10795 Exploit Targets Millions

Do Son June 10, 2026 0

A critical UpdraftPlus CVE-2026-10795 vulnerability threatens 3 million sites. Hackers are exploiting this UpdraftPlus authentication bypass in the wild.
Cloud Security Report Finds Fragmented Tools Widening the Cloud Complexity Gap Featured-Image-new_1780946080xcAbTTR9Sc
  • Press Release

Cloud Security Report Finds Fragmented Tools Widening the Cloud Complexity Gap

cybernewswire June 10, 2026 0
Washington D.C., USA, 10th June 2026, CyberNewswire
Read More Read more about Cloud Security Report Finds Fragmented Tools Widening the Cloud Complexity Gap
VerdantBamboo Malware Campaign Targets Edge Devices via Supply Chain Breach VerdantBamboo malware campaign Volexity threat report
  • Cyber Security
  • Malware

VerdantBamboo Malware Campaign Targets Edge Devices via Supply Chain Breach

Do Son June 10, 2026 0

Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.

Regulatory Alignment: Let’s Encrypt Amends Subscriber Agreement to Enforce US Sanctions and Export Compliance Let's Encrypt subscriber agreement Let's Encrypt OCSP Support 45-Day Certificate Limit Let's Encrypt Automation
  • Technology

Regulatory Alignment: Let’s Encrypt Amends Subscriber Agreement to Enforce US Sanctions and Export Compliance

Do Son June 10, 2026 0

Discover the new Let's Encrypt subscriber agreement changes. Learn how Version 1.7 integrates U.S. sanctions compliance for global SSL domains.
Algorithmic Acceleration: Microsoft Deploys Low-Latency Core Profiles via KB5094126 Cumulative Update Windows 11 CPU optimization Microsoft Windows user engagement
  • Windows

Algorithmic Acceleration: Microsoft Deploys Low-Latency Core Profiles via KB5094126 Cumulative Update

Do Son June 10, 2026 0

Discover the new Windows 11 CPU optimization in KB5094126. Learn how dynamic frequency scaling reduces interface latency and how to enable it.
Algorithmic Fluency: Google Unveils Gemini 3.5 Live Translate for Real-Time Audiocentric Mediation Gemini Live Translate tool
  • Technology

Algorithmic Fluency: Google Unveils Gemini 3.5 Live Translate for Real-Time Audiocentric Mediation

Do Son June 10, 2026 0

Discover the new Gemini Live Translate tool from Google. Learn how this low-latency vocal model translates over 70 languages seamlessly in real time.

Deprecating the Legacy: Google Chrome Initiates Final Removal of Manifest v2 Architecture Chrome Manifest v3 migration
  • Technology

Deprecating the Legacy: Google Chrome Initiates Final Removal of Manifest v2 Architecture

Do Son June 10, 2026 0

Discover the final Chrome Manifest v3 migration timeline. Learn how Google updates remove legacy MV2 flags and permanently disable classic ad blockers.

Architectural Exposure: Developers Extract Apple’s Subterranean Core Prompts for Siri AI Siri AI system prompt Siri AI iOS 27 Apple Siri URL summarization restriction interface in the iOS 27 beta update
  • Data Leak

Architectural Exposure: Developers Extract Apple’s Subterranean Core Prompts for Siri AI

Do Son June 10, 2026 0

Discover the leaked Siri AI system prompt from the iOS 27 beta. Learn how Apple structures JSON entities, tool logic, and system rules.

COXMO Botnet Variant: New Advanced Threat Exploits Router Firmware COXMO botnet variant Gafgyt malware analysis
  • Malware

COXMO Botnet Variant: New Advanced Threat Exploits Router Firmware

Do Son June 10, 2026 0

Read the latest Gafgyt malware analysis revealing how the dangerous COXMO botnet variant spreads via standalone scripts.

Havoc Stager Campaign Exploits Fake Invoices to Compromise Networks BingX cyberattack FortiGate SSO Attacks Firewall Config Theft
  • Malware

Havoc Stager Campaign Exploits Fake Invoices to Compromise Networks

Do Son June 10, 2026 0

Discover how the Havoc stager campaign exploits fake invoices. Read the LevelBlue SpiderLabs report detailing this stealthy threat.

Cybercriminals Deploy Malicious AI Extensions to Steal Private Chat Data malicious AI extensions browser data exfiltration
  • Data Leak
  • Malware

Cybercriminals Deploy Malicious AI Extensions to Steal Private Chat Data

Do Son June 10, 2026 0

A new report reveals how malicious AI extensions use browser data exfiltration tactics to steal private conversations from ChatGPT and Claude.

Sovereign Ascent: Anthropic Deploys Flagship Fable 5 Architecture Anthropic Fable 5 model
  • Technology

Sovereign Ascent: Anthropic Deploys Flagship Fable 5 Architecture

Do Son June 10, 2026 0

Discover the new Anthropic Fable 5 model family. Learn how its advanced vision layer reverse-engineers code from pixels with zero cap access.
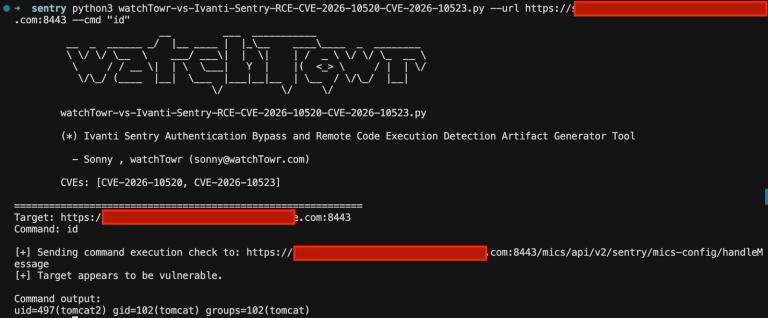
Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10 Ivanti Sentry RCE publicly disclosed PoC
  • Vulnerability Report

Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10

Do Son June 10, 2026 0

Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.

OpenSSL Security Patches Fix Remote Code Execution Risk CVE-2022-3602 OpenSSL security patches remote code execution risk
  • Vulnerability Report

OpenSSL Security Patches Fix Remote Code Execution Risk

Do Son June 10, 2026 0

New OpenSSL security patches address a critical use-after-free bug that introduces an immediate remote code execution risk across enterprise systems.

New Microsoft Defender Zero Day Exploit Released Publicly Online Defender zero day exploit race condition vulnerability
  • Vulnerability Report

New Microsoft Defender Zero Day Exploit Released Publicly Online

Do Son June 10, 2026 0

A new Microsoft Defender zero day exploit leaks online, exposing a severe race condition vulnerability affecting fully patched Windows installations.
CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws

Do Son June 10, 2026 0

The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws

Do Son June 10, 2026 0

Deploy the latest Microsoft Patch Tuesday fixes. The June release addresses severe zero day vulnerabilities and over thirty critical flaws.

High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile Ivanti EPMM security updates Ivanti ITSM vulnerability authenticated privilege escalation Ivanti Xtraction vulnerability CVE-2026-8043 Ivanti EPM RCE, SQL Injection Ivanti EPM, remote code execution CVE-2024-50330 - CVE-2025-0282 and CVE-2025-0283
  • Vulnerability Report

High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile

Do Son June 10, 2026 0

New Ivanti EPMM security updates address high-severity flaws that could allow a remote authenticated attacker to achieve remote code execution.

Critical Rclone Command Execution Bug Threatens Cloud Environments rclone command execution execute local commands Rclone RCE CVE-2026-41176
  • Vulnerability Report

Critical Rclone Command Execution Bug Threatens Cloud Environments

Do Son June 10, 2026 0

A critical rclone command execution flaw allows users to execute local commands. Secure your cloud synchronization setup against this risk.

Critical Veeam Backup Vulnerability Exposed Veeam Backup vulnerability remote code execution Veeam Backup vulnerability Veeam Vulnerabilities CVE-2024-42448 & CVE-2024-42449
  • Vulnerability Report

Critical Veeam Backup Vulnerability Exposed

Do Son June 10, 2026 0

A critical Veeam Backup vulnerability allows remote code execution. Secure your domain-joined systems by upgrading to the latest build immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.