Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
TP-Link Patches Critical Setup Flaw Across Multiple Tapo Smart Devices Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

TP-Link Patches Critical Setup Flaw Across Multiple Tapo Smart Devices

Do Son June 5, 2026 0

A critical Tapo smart device vulnerability stems from unencrypted Bluetooth transmission. Learn how to patch your smart plugs, bulbs, and chimes.

International Law Enforcement Smashes Major Identity Forgery Ring counterfeit document production facility fraudulent identity documents
  • Cybercriminals

International Law Enforcement Smashes Major Identity Forgery Ring

Do Son June 5, 2026 0

Europol dismantled a counterfeit document production facility in Spain distributing fraudulent identity documents across Europe through an online marketplace.

International Law Enforcement Smashes Major Illegal Streaming Networks illegal streaming networks complex criminal enterprises UAT-7290 China-nexus Espionage Adversarial Misuse of Generative AI
  • Cybercriminals

International Law Enforcement Smashes Major Illegal Streaming Networks

Do Son June 5, 2026 0

Europol targets illegal streaming networks run by complex criminal enterprises. The joint action dismantled nine crime groups and removed 27,000 URLs.
Teamwork Cloud RCE Vulnerability Threatens Corporate Modeling Platforms Teamwork Cloud RCE vulnerability untrusted deserialization flaw
  • Vulnerability Report

Teamwork Cloud RCE Vulnerability Threatens Corporate Modeling Platforms

Do Son June 5, 2026 0

A critical Teamwork Cloud RCE vulnerability exploits an untrusted deserialization flaw. Patch No Magic and CATIA systems now.
Poly VoIP Phone Vulnerability Revealed with Public Exploit Code Disclosed Poly VoIP phone vulnerability public exploit code released
  • Vulnerability Report

Poly VoIP Phone Vulnerability Revealed with Public Exploit Code Disclosed

Do Son June 5, 2026 0

A critical Poly VoIP phone vulnerability is exposed. Read the report now that public exploit code released online to secure your office networks.

Critical Policy Bypass Flaw Threatens OpenStack Mistral Workflow Environments Mistral policy bypass flaw arbitrary code execution CVE-2024-40767 Keystone Vulnerability S3 Bypass
  • Vulnerability Report

Critical Policy Bypass Flaw Threatens OpenStack Mistral Workflow Environments

Do Son June 5, 2026 0

A critical Mistral policy bypass flaw allows arbitrary code execution. Learn how to patch your workflow service to prevent security credentials theft.
IBM WebSphere Security Advisory: Critical Vulnerabilities Uncovered IBM WebSphere execution flaws WebSphere security bulletin patches request smuggling patch WebSphere remote code execution Langflow OSS vulnerability remote code execution patch
  • Vulnerability Report

IBM WebSphere Security Advisory: Critical Vulnerabilities Uncovered

Do Son June 5, 2026 0

Severe IBM WebSphere execution flaws expose servers to RCE. Apply the new WebSphere security bulletin patches immediately to secure your network.
Chrome Desktop Security Update Resolves Hundreds of Vulnerabilities Chrome desktop security update critical vulnerabilities patched
  • Vulnerability Report

Chrome Desktop Security Update Resolves Hundreds of Vulnerabilities

Do Son June 5, 2026 0

The new Chrome desktop security update resolves hundreds of issues. Protect your device against several critical vulnerabilities patched today.
Cisco SD-WAN Vulnerability Exploited in the Wild with Root RCE Risks Cisco SD-WAN vulnerability CVE-2026-20262, arbitrary file write, SD-WAN Manager Cisco SD-WAN vulnerability exploited in the wild
  • Vulnerability Report

Cisco SD-WAN Vulnerability Exploited in the Wild with Root RCE Risks

Do Son June 5, 2026 0

A critical Cisco SD-WAN vulnerability is actively exploited in the wild. Learn how to inspect logs and secure your deployment immediately.
53M Downloads At Risk: Critical 9.8 CVSS Vitest Remote Code Execution Vulnerabilities Disclosed Vitest RCE vulnerability CVE-2026-53633, Browser Mode RCE, config file overwrite Vitest remote code execution critical 9.8 CVSS flaws
  • Vulnerability Report

53M Downloads At Risk: Critical 9.8 CVSS Vitest Remote Code Execution Vulnerabilities Disclosed

Do Son June 5, 2026 0

Critical 9.8 CVSS flaws trigger Vitest remote code execution risks. Discover how to protect your testing environments and patch these bugs immediately.
SSHFS Command Execution Exploit Code Released Publicly sshfs command execution exploit public exploit code released
  • Vulnerability Report

SSHFS Command Execution Exploit Code Released Publicly

Do Son June 5, 2026 0

A serious sshfs command execution exploit threat is unveiled. Protect your Linux clients now that public exploit code released online.
The Renaissance of Native Architecture: Microsoft Rebrands WinUI to Salvage Windows 11 Performance Microsoft WinUI rebrand
  • Windows

The Renaissance of Native Architecture: Microsoft Rebrands WinUI to Salvage Windows 11 Performance

Do Son June 4, 2026 0

Discover the Microsoft WinUI rebrand from Build 2026. Learn how Microsoft is ditching web hybrid apps to fix Windows 11 performance.

The Quantum Bastion: Let’s Encrypt Embraces Merkle Tree Certificates against Post-Quantum Threats Merkle Tree Certificates Let's Encrypt 45-Day Certificates ACME Profile Updates 2026 Let’s Encrypt Generation Y, 45-Day TLS Certificates Let's Encrypt, IP Certificates Certificate Revocation Lists
  • Technology

The Quantum Bastion: Let’s Encrypt Embraces Merkle Tree Certificates against Post-Quantum Threats

Do Son June 4, 2026 0

Discover how Merkle Tree Certificates resolve post-quantum signature bloat. Learn about the new TLS standards from Google and Cloudflare.
Refining the Interface: Microsoft Addresses the Cluttered Windows 11 Context Menu Windows 11 version 26H2 support lifecycle and deployment roadmap for enterprise environments Windows 11 update anomaly Windows 11 context menu Windows 11 KB5089549 update error 0x800f0922 Windows 11 taskbar relocation
  • Windows

Refining the Interface: Microsoft Addresses the Cluttered Windows 11 Context Menu

Do Son June 4, 2026 0

Discover upcoming changes to the Windows 11 context menu. Learn how Microsoft plans to optimize speed and remove right-click menu bloat.
Apache Fory Vulnerability: High Severity Flaw Bypasses Core Java Serialization Checks Apache Fory vulnerability Apache Fory vulnerability patch PyFory deserialization policy bypass
  • Vulnerability Report

Apache Fory Vulnerability: High Severity Flaw Bypasses Core Java Serialization Checks

Do Son June 4, 2026 0

Learn how a new Apache Fory vulnerability impacts Java platforms. Apply the urgent Apache Fory vulnerability patch to protect your enterprise nodes.

DriveSurge Threat Cluster Exploits Thousands of Websites Globally DriveSurge threat cluster Traffic Distribution System
  • Cybercriminals

DriveSurge Threat Cluster Exploits Thousands of Websites Globally

Do Son June 4, 2026 0

The active DriveSurge threat cluster is compromising thousands of websites. Discover how its customized Traffic Distribution System redirects victims.
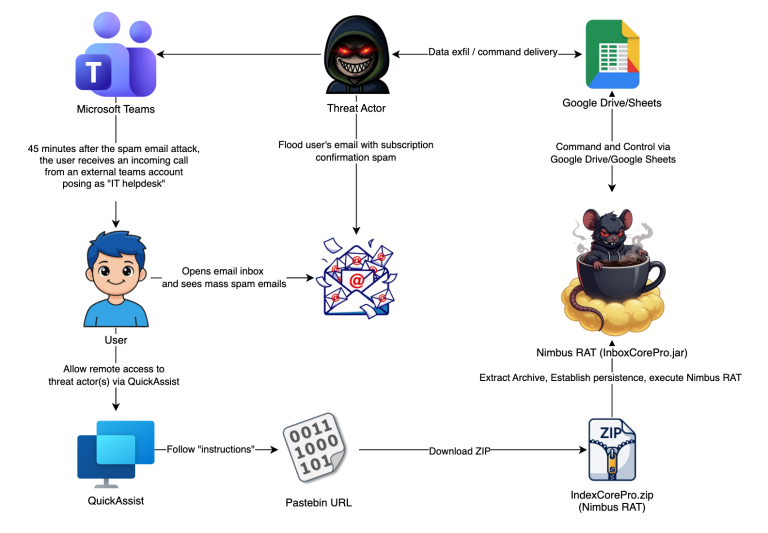
New Microsoft Teams Vishing Attack Exploits Quick Assist to Deploy Stealthy Malware Microsoft Teams vishing attack Nimbus RAT deployment
  • Malware

New Microsoft Teams Vishing Attack Exploits Quick Assist to Deploy Stealthy Malware

Do Son June 4, 2026 0

Learn how a Microsoft Teams vishing attack leverages email flooding and Quick Assist to execute a dangerous Nimbus RAT deployment chain.
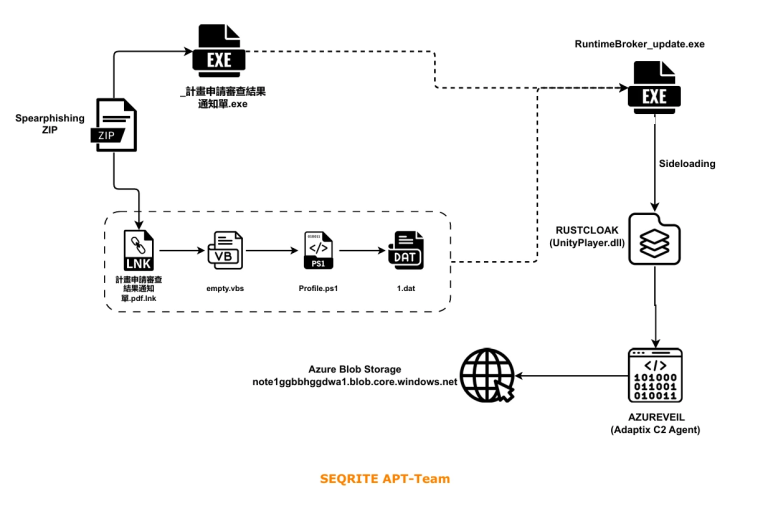
Operation Dragon Weave Exposed: Cyber Espionage Campaign Weaponizes Cloud Storage Operation Dragon Weave dead-drop C2 channel
  • Cybercriminals

Operation Dragon Weave Exposed: Cyber Espionage Campaign Weaponizes Cloud Storage

Do Son June 4, 2026 0

Learn how Operation Dragon Weave uses a dead-drop C2 channel on Azure Blob Storage to target global officials in a new espionage campaign.
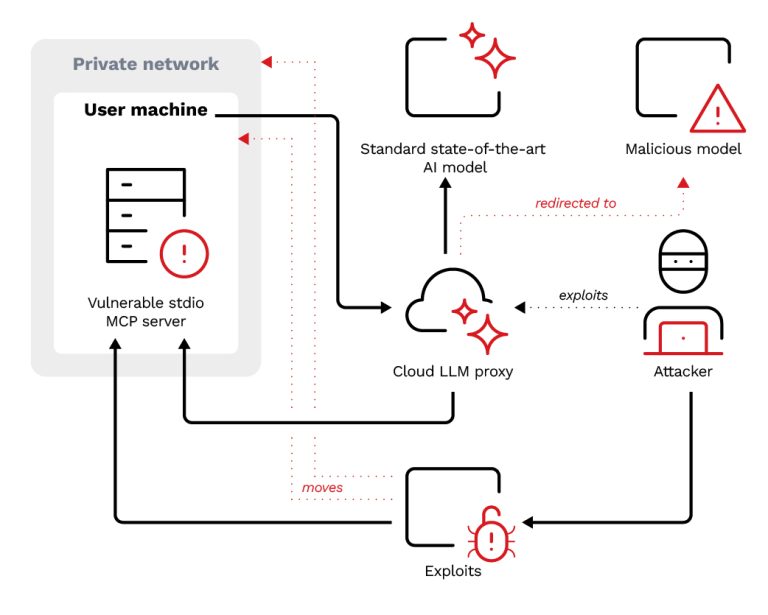
AI Generated Code Vulnerabilities Threaten Emerging Dev Ecosystems AI generated code vulnerabilities MCP server repositories
  • Vulnerability Report

AI Generated Code Vulnerabilities Threaten Emerging Dev Ecosystems

Do Son June 4, 2026 0

New research explores AI generated code vulnerabilities within MCP server repositories. Learn why expert domain verification remains critical.
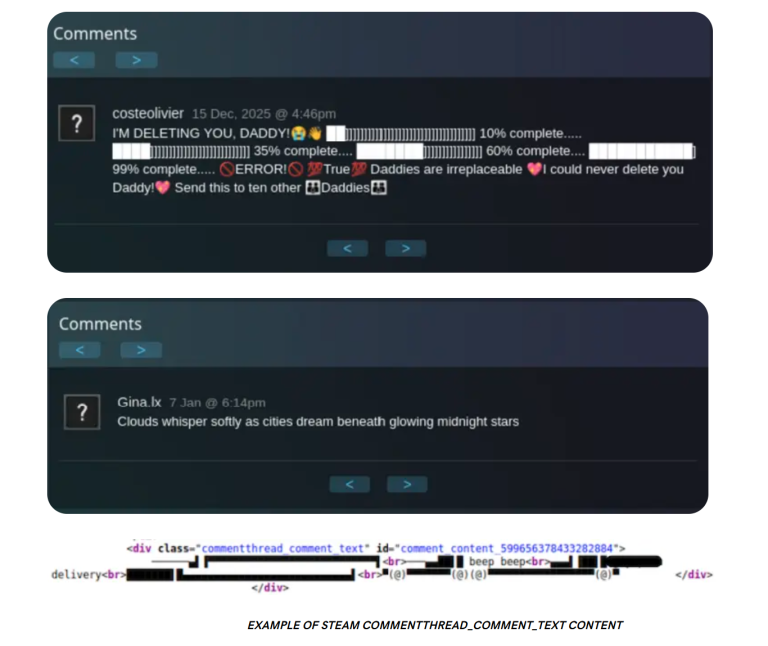
Valve Platform Exploited to Distribute WordPress Web Shells Steam profile malware campaign invisible Unicode steganography
  • Malware

Valve Platform Exploited to Distribute WordPress Web Shells

Do Son June 4, 2026 0

A sneaky Steam profile malware campaign targets WordPress. Attackers use invisible Unicode steganography to hide malicious command strings.
Google Unveils Gemma 4 12B: Democratic Multimodal AI for Consumer Hardware Google Gemma 4 12B
  • Technology

Google Unveils Gemma 4 12B: Democratic Multimodal AI for Consumer Hardware

Do Son June 4, 2026 0

Discover Google Gemma 4 12B, a new multimodal model for 16GB consumer hardware. Learn how this open-source AI runs natively.

The Sovereignty of Content: Google Unveils AI Overview Opt-Out Controls AI Overviews opt out Google Gemini Pentagon contract Penske Media, AI Overviews
  • Technology

The Sovereignty of Content: Google Unveils AI Overview Opt-Out Controls

Do Son June 4, 2026 0

Discover the new AI Overviews opt out feature. Learn how to block AI scraping via Search Console without losing organic search visibility.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.