Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright AI pre-release vetting AI copyright law US UK FoundationMotion, AI Motion Understanding AI Deregulation, DOGE AI Self-Preservation, GPT-4o Country of Geniuses
  • Technology

The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright

Do Son March 7, 2026 0

The US Supreme Court denies AI-generated copyright, while the UK suspends its controversial "opt-out" data bill. Is the era of free AI training over?
Identity Under Attack: Why Deception Is Becoming Essential for Active Directory Security Employees Risk
  • Technique

Identity Under Attack: Why Deception Is Becoming Essential for Active Directory Security

Do Son March 6, 2026 0
Identity is now the primary target in cyberattacks. Attackers go after authentication systems—especially Microsoft Active Directory (AD)....
Read More Read more about Identity Under Attack: Why Deception Is Becoming Essential for Active Directory Security
The “Threads” Trap: How X is Weaponizing Narrative Suspense to Dethrone Meta X Creator Subscriptions 2.0
  • Technology

The “Threads” Trap: How X is Weaponizing Narrative Suspense to Dethrone Meta

Do Son March 6, 2026 0

X launches "Exclusive Threads," a masterful 2.0 upgrade that lets creators paywall the climax of their stories. See how suspense is the new currency for 2026.

The Ruwiki Sleeper: How a Slumbering JavaScript Worm Paralyzed Wikipedia’s Global Infrastructure Wikipedia JavaScript worm Wikimedia Enterprise AI partners, Wikipedia 25th anniversary monetization Wikipedia down Wikipedia Paid API AI Traffic Decline
  • Technology

The Ruwiki Sleeper: How a Slumbering JavaScript Worm Paralyzed Wikipedia’s Global Infrastructure

Do Son March 6, 2026 0

A dormant ruwiki script triggered a global Wikipedia lockdown. Discover how a 23-minute JavaScript worm compromised admins and forced a read-only mandate.
The Torrent Titanic Sinks: YggTorrent Breached as Hackers Expose “Turbo” Tier Greed and 54,000 Credit Cards Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

The Torrent Titanic Sinks: YggTorrent Breached as Hackers Expose “Turbo” Tier Greed and 54,000 Credit Cards

Do Son March 6, 2026 0

YggTorrent infrastructure falls to unknown hackers. Discover the massive 54,000 credit card leak, the "Turbo" tier scandal, and the new ygg.gratis clone.

Unmasking the Shadows: A Global Hunt for PlugX Staging Infrastructure Mustang Panda C2 Procurement
  • Malware

Unmasking the Shadows: A Global Hunt for PlugX Staging Infrastructure

Do Son March 6, 2026 0

Researcher @goyaramen reveals how PRC threat actors like Mustang Panda use expired domains and Cloudflare to mask their PlugX C2 infrastructure.
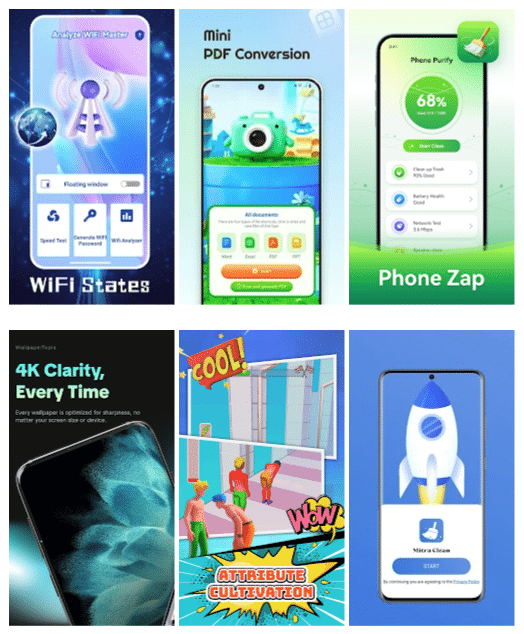
Unmasking Genisys: The AI-Powered Ad Fraud Scheme Silently Hijacking Your Smartphone Genisys Ad Fraud
  • Malware

Unmasking Genisys: The AI-Powered Ad Fraud Scheme Silently Hijacking Your Smartphone

Do Son March 6, 2026 0

IAS Threat Lab unmasks Genisys, a massive AI-powered mobile ad fraud scheme hijacking smartphones to generate fake traffic and steal from advertisers.
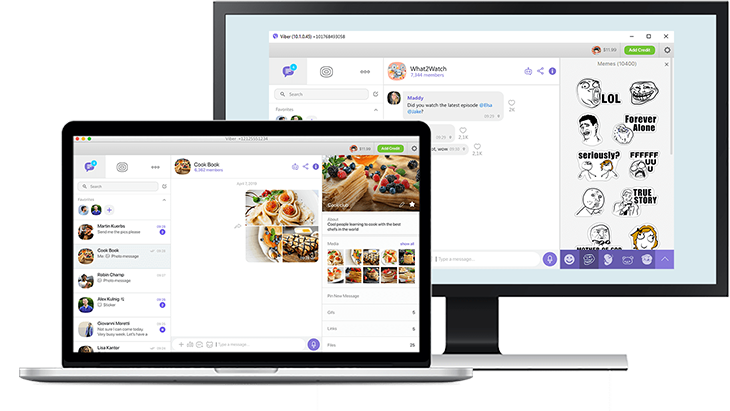
Exposed in Plain Sight: Critical Privacy Flaw Defeats Viber’s Anti-Censorship ‘Cloak’ Mode Viber Cloak Vulnerability CVE-2025-13476
  • Vulnerability Report

Exposed in Plain Sight: Critical Privacy Flaw Defeats Viber’s Anti-Censorship ‘Cloak’ Mode

Do Son March 6, 2026 0

CERT/CC reveals a major privacy flaw (CVE-2025-13476) in Viber's Cloak mode, allowing network censors to easily identify and block proxy traffic. Update now.

OpenAI Unveils GPT-5.4: The “Professional” Frontier with Native Computer Control and 1M Token Context ChatGPT advertising US only OpenAI GPT-5.4 launch OpenAI Responses API file support ChatGPT Ads pricing ChatGPT conversational advertising, OpenAI monetization strategy 2026 OpenAI Code Red, ChatGPT Sycophancy Crisis AI music ChatGPT memory, targeted ads ChatGPT User Milestone, Generative AI Adoption ChatGPT ads, AI monetization GPT-5, OpenAI
  • Technology

OpenAI Unveils GPT-5.4: The “Professional” Frontier with Native Computer Control and 1M Token Context

Do Son March 6, 2026 0

OpenAI launches GPT-5.4, featuring native computer control that beats human benchmarks and a 1M token context window. See the new "Professional" AI in action.

Sovereign & AI-Native: Broadcom’s VMware Telco Cloud Platform 9 Rewrites the TCO Rulebook at MWC 2026 VMware Telco Cloud Platform 9 Tesco, Broadcom, VMware Walmart Broadcom Jericho4, Distributed AI Infrastructure Broadcom VMware, Perpetual Licenses AI Data Centers, Network Switch Unix automation security, Broadcom vulnerability
  • Technology

Sovereign & AI-Native: Broadcom’s VMware Telco Cloud Platform 9 Rewrites the TCO Rulebook at MWC 2026

Do Son March 6, 2026 0

Broadcom unveils VMware Telco Cloud Platform 9 at MWC 2026, promising a 40% TCO reduction through AI-native architecture and sovereign cloud-ready infrastructure.
The iPhone’s Shadow: Why the MacBook Neo is Trapped with 8GB of RAM and a Single Chip MacBook Neo 8GB RAM limit MacBook Neo Windows Parallels
  • Technology

The iPhone’s Shadow: Why the MacBook Neo is Trapped with 8GB of RAM and a Single Chip

Do Son March 6, 2026 0

Discover why Apple's new MacBook Neo is stuck with 8GB of RAM. We dive into the A18 Pro chip constraints and the trade-offs of this $599 ultra-entry laptop.

The Cart is Empty: Why OpenAI is Abandoning In-App Shopping to Become an “AI Discovery Engine” ChatGPT Shopping retreat ChatGPT Search, OpenAI
  • Technology

The Cart is Empty: Why OpenAI is Abandoning In-App Shopping to Become an “AI Discovery Engine”

Do Son March 6, 2026 0

OpenAI is pulling the plug on ChatGPT's native checkout. Discover why the "Amazon killer" is pivoting to an ad-based discovery model after a Shopify slump.

Eyes on the Front: Iranian Threat Actors Weaponize IP Cameras in Middle East Conflict Iranian Cyber Reconnaissance IP Camera Security NCSC Warning Russian Hacktivists Taiwan Cyberattacks China State-Sponsored Hacking state-sponsored threat actor Ransomware RAT Abuse, AnyDesk
  • Cyber Security
  • Vulnerability Report

Eyes on the Front: Iranian Threat Actors Weaponize IP Cameras in Middle East Conflict

Do Son March 6, 2026 0

A new Check Point Research report reveals how Iranian-nexus threat actors compromise IP cameras in the Middle East for real-time missile reconnaissance.

Stream Hijacked: Critical Zero-Click Command Injection Flaw Exposed in AVideo-Encoder AVideo-Encoder Vulnerability CVE-2026-29058
  • Vulnerability Report

Stream Hijacked: Critical Zero-Click Command Injection Flaw Exposed in AVideo-Encoder

Do Son March 6, 2026 0

A critical 9.8 CVSS flaw (CVE-2026-29058) in AVideo-Encoder allows unauthenticated remote attackers to execute arbitrary system commands. Patch now.

Cracking the Cloud’s Crypto: Unauthenticated Bypass Flaws Found in Amazon’s AWS-LC Library Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Vulnerability Report

Cracking the Cloud’s Crypto: Unauthenticated Bypass Flaws Found in Amazon’s AWS-LC Library

Do Son March 6, 2026 0

Researchers discovered three major flaws in Amazon’s AWS-LC cryptographic library, allowing hackers to bypass digital signature validation. Update now.

Signed Malware Masquerading as Workplace Apps Deploys Persistent Backdoors EV Certificate Phishing RMM Backdoors
  • Cybercriminals

Signed Malware Masquerading as Workplace Apps Deploys Persistent Backdoors

Do Son March 6, 2026 0

Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.

Unmasking OCRFix: The New Russian Botnet Hiding its C2 Infrastructure in the Blockchain OCRFix Botnet EtherHiding CrowdStrike supply chain attack Ivanti CSA Vulnerabilities
  • Malware

Unmasking OCRFix: The New Russian Botnet Hiding its C2 Infrastructure in the Blockchain

Do Son March 6, 2026 0

Cybersecurity researchers uncover OCRFix, a Russian-linked botnet using EtherHiding and fake CAPTCHAs to mask its C2 servers in blockchain smart contracts.

Malicious PHP Packages Found Hidden in Laravel Ecosystem fast16 Malware Cyber Sabotage IronWind malware Stealc
  • Malware

Malicious PHP Packages Found Hidden in Laravel Ecosystem

Do Son March 6, 2026 0

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).

Which Tool Is Free And Secure to Merge PDFs Online? Screenshot_20260305_220705_Docs
  • Technique

Which Tool Is Free And Secure to Merge PDFs Online?

Do Son March 5, 2026 0
If you’ve ever had to merge pdf files securely and without losing your mind, you know it...
Read More Read more about Which Tool Is Free And Secure to Merge PDFs Online?
Nvidia’s “Overclocking” Rescue: The 595.76 Hotfix Arrives to Cure GPU Voltage and Cooling Woes NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Technology

Nvidia’s “Overclocking” Rescue: The 595.76 Hotfix Arrives to Cure GPU Voltage and Cooling Woes

Do Son March 5, 2026 0

Nvidia releases the 595.76 Hotfix to resolve a critical voltage cap preventing GPU overclocking and fix Resident Evil: Requiem visual bugs. Download now!

Weaponized in the Wild: Public PoC Exploit Disclosed for Critical 10.0 Cisco SD-WAN Flaw Cisco SD-WAN Vulnerability CVE-2026-20127 CVE-2024-20481 - Daggerfly group
  • Vulnerability Report

Weaponized in the Wild: Public PoC Exploit Disclosed for Critical 10.0 Cisco SD-WAN Flaw

Do Son March 5, 2026 0

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!
Integer Overflow Flaw in Apache ActiveMQ Exposes MQTT Brokers to DoS ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability Report

Integer Overflow Flaw in Apache ActiveMQ Exposes MQTT Brokers to DoS

Do Son March 5, 2026 0

An integer overflow flaw (CVE-2025-66168) in Apache ActiveMQ's MQTT module allows authenticated attackers to crash brokers. Update your systems immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-109469CVSS 10.0
    Authorization bypass through user-controlled key in Entra Device Registration allows an unauthorized attacker to elevate privileges over a...
    📅 Updated: Nov 6, 2026
  • CVE-2026-68935CVSS 9.1
    Chartbrew is an open-source web application for creating charts from databases and APIs. In versions 4.8.5 through 5.2.2,...
    📅 Updated: Nov 6, 2026
  • CVE-2025-9230CVSS 9.8
    Issue summary: An application trying to decrypt CMS messages encrypted using password based encryption can trigger an out-of-bounds...
    📅 Updated: Nov 6, 2026
  • CVE-2024-4741CVSS 9.8
    Issue summary: Calling the OpenSSL API function SSL_free_buffers may cause memory to be accessed that was previously freed...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.