 cybernewswire
Philadelphia, PA, United States, 9th March 2026, CyberNewswire
 Do Son
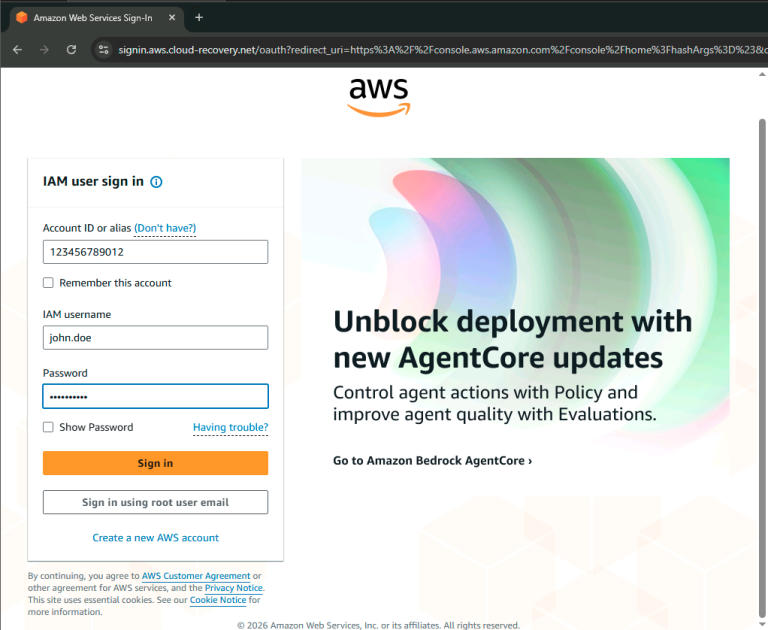
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

Apache IoTDB issues an urgent fix for a critical JEXL injection flaw (CVE-2026-24713) and insecure defaults. Upgrade to 1.3.7 or 2.0.7 to secure your IIoT data.
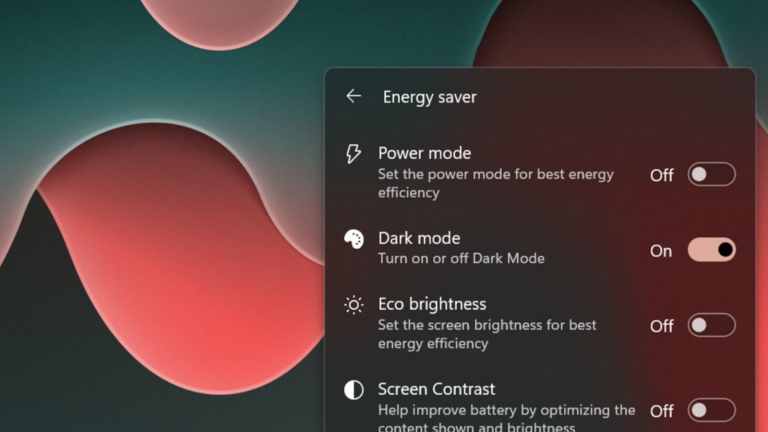
Microsoft finally adds a one-click Dark Mode toggle to the Windows 11 taskbar—but it's hidden in the Energy Saver menu. Is this a genius move or a UI fail?
OpenAI's new "Codex for Open Source" offers maintainers 6 months of ChatGPT Pro and Codex Security. Is your repository eligible for this $1,200 AI grant?

OpenAI's robotics lead Caitlin Kalinowski resigns in a "crisis of governance" over the Pentagon deal. Discover the "red lines" shaking the AI industry in 2026.

The Pentagon brands Anthropic a "Supply-Chain Risk" over ethical AI refusals. See how Microsoft, Google, and Amazon are defying the military to save Claude.

Nintendo sues the U.S. for a full refund of "unlawful" Trump tariffs. Discover how the 2026 IEEPA ruling could shift the price of the Nintendo Switch 2.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.
A critical 9.4 CVSS buffer overflow flaw (CVE-2026-1678) in Zephyr RTOS's DNS parser allows unauthenticated RCE on IoT devices. Patch immediately.
Critical vulnerabilities in Vaultwarden (like CVE-2026-27898) allow privilege escalation and unauthorized access to secrets. Update to version 1.35.4 now.
A critical 9.3 CVSS reflected XSS flaw (CVE-2026-29183) in SiYuan's dynamic icon API lets attackers steal private notes via SVG injection. Update now.

Apache ZooKeeper vulnerabilities (CVE-2026-24281, CVE-2026-24308) allow PTR record spoofing and sensitive data leaks in logs. Update clusters immediately.

Researchers uncover a massive campaign by a Vietnamese operator using GitHub and Polygon blockchain smart contracts to distribute the StealC infostealer.

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.

Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.

A critical 9.8 CVSS flaw (CVE-2026-27944) in Nginx UI lets hackers download and decrypt full system backups via an open API. Update and rotate secrets!
OpenAI launches Codex Security, an advanced AI agent that uses reasoning to find and fix complex vulnerabilities without the noise of false positives.

Apple overhauls its hardware lineup amidst a global DRAM famine. Discover why the 512GB Mac Studio is extinct and how the MacBook Air is being reborn.