Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The AI Heartbeat: Why Microsoft is Moving Build 2026 to San Francisco’s Historic Fort Mason Microsoft Build 2026
  • Technology

The AI Heartbeat: Why Microsoft is Moving Build 2026 to San Francisco’s Historic Fort Mason

Do Son March 4, 2026 0

Microsoft Build 2026 moves to San Francisco on June 2–3. With a 2,500-attendee limit at Fort Mason, the focus is on "Agentic AI" and deep technical immersion.

Personal Superintelligence: Meta AI Unveils “Shopping Research” to Take on Gemini and ChatGPT Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Technology

Personal Superintelligence: Meta AI Unveils “Shopping Research” to Take on Gemini and ChatGPT

Do Son March 4, 2026 0

Meta AI launches "Shopping Research" trials in the US. With visual carousels and tailored advice, Zuckerberg’s agentic tools aim to revolutionize e-commerce.
The Ray Tracing Revolution: Microsoft’s Shader Model 6.9 Unlocks a 90% Power Surge for Intel and NVIDIA Shader Execution Reordering (SER)
  • Technology

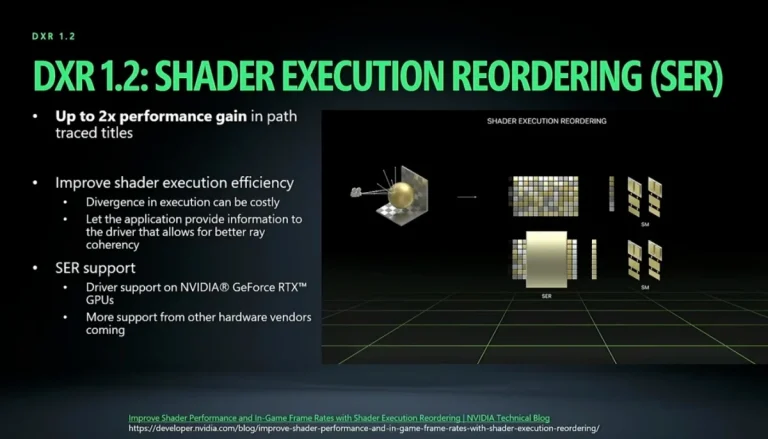
The Ray Tracing Revolution: Microsoft’s Shader Model 6.9 Unlocks a 90% Power Surge for Intel and NVIDIA

Do Son March 4, 2026 0

Microsoft’s Shader Model 6.9 introduces Shader Execution Reordering (SER), delivering a staggering 90% ray tracing boost for Intel Arc and 40% for NVIDIA GPUs.

From Vision to Validation: Ericsson Unveils the “Superbrain” of 6G with First Live OTA Trials at MWC 2026 Ericsson 6G OTA trial CVE-2024-39696
  • Technology

From Vision to Validation: Ericsson Unveils the “Superbrain” of 6G with First Live OTA Trials at MWC 2026

Do Son March 4, 2026 0

Ericsson makes 6G real at MWC 2026 with the world’s first pre-standard OTA trial and radar-like ISAC technology, powering the next era of AI-native networks.

Siri’s Secret Engine: Why 90% of Apple’s AI Servers are Idle as Google Gemini Takes the Reins iOS 27 Apple Intelligence Apple AI Extensions bazaar Siri iOS 27 Gemini integration Apple AI server Baltra Siri AI delay iOS 26.4 Apple Google Gemini Siri partnership, Siri powered by Google Gemini 2026 Siri Gemini, Apple Intelligence Siri, Apple AI Apple "Veritas", Siri AI Siri Gemini Supercharged Siri, AI assistant Siri Integration, App Intents Apple Siri Apple AI Strategy, ChatGPT Rival
  • Technology

Siri’s Secret Engine: Why 90% of Apple’s AI Servers are Idle as Google Gemini Takes the Reins

Do Son March 4, 2026 0

Apple’s AI infrastructure faces a 90% dormancy crisis. To save Siri, Apple is turning to Google Gemini while secretly developing the 3nm "Baltra" AI chip.
Critical RCE Vulnerability Discovered in OpenStack Vitrage Root Cause Analysis Service OpenStack Vitrage RCE CVE-2026-28370
  • Vulnerability Report

Critical RCE Vulnerability Discovered in OpenStack Vitrage Root Cause Analysis Service

Do Son March 4, 2026 0

Nokia discovers a critical 9.1 RCE flaw (CVE-2026-28370) in OpenStack Vitrage's RCA service. Patch immediately to prevent total host server takeovers.
Critical Auth Bypass in Apache Artemis: Attackers Can Hijack Message Queues ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability

Critical Auth Bypass in Apache Artemis: Attackers Can Hijack Message Queues

Do Son March 4, 2026 0

A critical flaw (CVE-2026-27446) in Apache Artemis allows unauthenticated attackers to hijack message queues via rogue brokers. Update to 2.52.0 immediately.

Django Releases Security Patches to Address DoS and Permission Vulnerabilities Django Security Update CVE-2026-25673 Django Security Update SQL Injection Vulnerability Django SQL Injection, PostgreSQL Flaw CVE-2022-34265 PoC Django, SQL injection
  • Vulnerability Report

Django Releases Security Patches to Address DoS and Permission Vulnerabilities

Do Son March 4, 2026 0

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.

CISA Adds Qualcomm and VMware Flaws to Known Exploited Catalog Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability Report

CISA Adds Qualcomm and VMware Flaws to Known Exploited Catalog

Do Son March 4, 2026 0

CISA adds actively exploited Qualcomm (CVE-2026-21385) and VMware (CVE-2026-22719) flaws to its KEV catalog. See the impact and patch deadlines inside.

Cyber Retaliation Escalates: Iranian Hacktivists Target Critical Infrastructure Following Military Strikes Iranian Hacktivists Operation Epic Fury Cyber New Generation Warfare Russian Hybrid Escalation Plex data breach Water Systems Cybersecurity - Threat Actor Naming Standard
  • Cyber Security

Cyber Retaliation Escalates: Iranian Hacktivists Target Critical Infrastructure Following Military Strikes

Do Son March 4, 2026 0

Sophos X-Ops CTU warns of a surge in Iranian hacktivist cyber retaliation, including DDoS and targeted doxxing, following Operation Epic Fury.
Critical Vulnerabilities in AVideo: From SQL Injection to Remote Code Execution AVideo RCE YPTSocket Vulnerability AVideo Vulnerabilities Streaming Platform Security AVideo Vulnerabilities CVE-2026-28501
  • Vulnerability Report

Critical Vulnerabilities in AVideo: From SQL Injection to Remote Code Execution

Do Son March 4, 2026 0

AVideo patches two critical flaws (CVE-2026-28501 & 28502) allowing unauthenticated SQL injection and remote code execution. Update to version 23 now.

WordPress Security Alert: Critical Privilege Escalation Flaw in Popular Membership Plugin WordPress Privilege Escalation CVE-2026-1492 Sneeit Framework RCE, Unauthenticated Code Execution Post SMTP, Account Takeover WordPress Vulnerability, Unpatched XSS WordPress Vulnerability, PHP Object Injection WordPress AI Engine, Privilege Escalation CVE-2024-43153 & CVE-2024-43234
  • Vulnerability Report

WordPress Security Alert: Critical Privilege Escalation Flaw in Popular Membership Plugin

Do Son March 4, 2026 0

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.
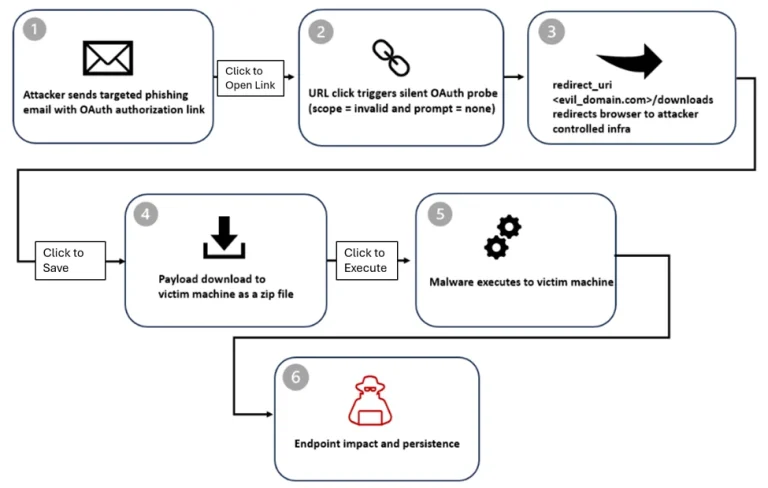
OAuth Hijack: Phishing Campaigns Weaponize Legitimate Redirection to Bypass Defenses OAuth Phishing Redirect URI Abuse
  • Cybercriminals

OAuth Hijack: Phishing Campaigns Weaponize Legitimate Redirection to Bypass Defenses

Do Son March 4, 2026 0

Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

ClickFix Alert: Fake Venture Capitalists Target Web3 Pros with “Terminal” Phishing ClickFix Malware Crypto VC Scam
  • Malware

ClickFix Alert: Fake Venture Capitalists Target Web3 Pros with “Terminal” Phishing

Do Son March 4, 2026 0

Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.

Trojanized FileZilla FTP Client Targets Developer Credentials via DLL Sideloading FileZilla Malware DLL Hijacking
  • Malware

Trojanized FileZilla FTP Client Targets Developer Credentials via DLL Sideloading

Do Son March 4, 2026 0

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.
Critical RCE Flaw in Qwik Framework Allows Server Takeover via Single Request Qwik RCE CVE-2026-27971
  • Vulnerability Report

Critical RCE Flaw in Qwik Framework Allows Server Takeover via Single Request

Do Son March 4, 2026 0

Qwik framework patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-27971) where unsafe deserialization in server$ RPC allows total server takeover.
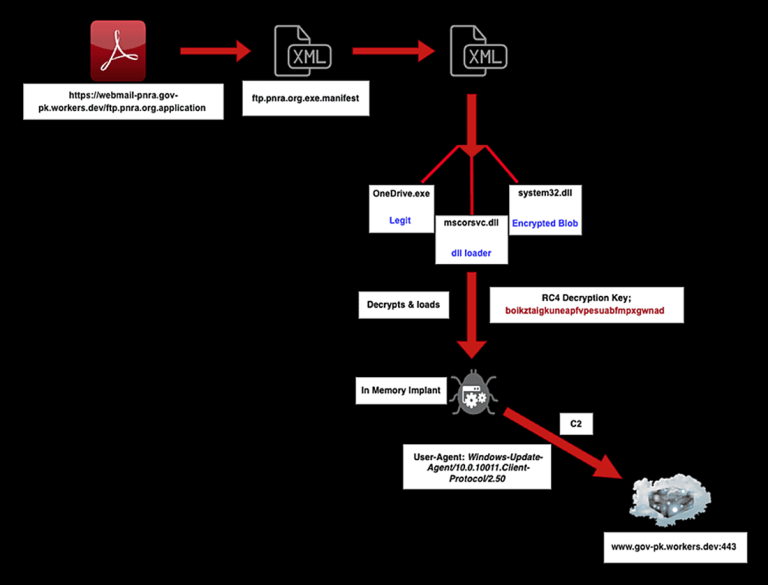
The BurrowShell Threat: Inside ‘Sloppy Lemming’s’ Stealthy Cyber Espionage Campaign in South Asia Sloppy Lemming BurrowShell Malware
  • Cyber Security
  • Malware

The BurrowShell Threat: Inside ‘Sloppy Lemming’s’ Stealthy Cyber Espionage Campaign in South Asia

Do Son March 4, 2026 0

Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

AuraStealer: The “Result-Oriented” Malware Rising from the Post-Lumma Void AuraStealer Malware Infostealer
  • Malware

AuraStealer: The “Result-Oriented” Malware Rising from the Post-Lumma Void

Do Son March 4, 2026 0

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

The Trojan Prompt: How an Autonomous AI Hijacked Aqua Trivy to Weaponize Developer Copilots AI Prompt Injection Aqua Trivy Breach AI Assistant Apertus, open-source AI .ai domain milestone
  • Vulnerability Report

The Trojan Prompt: How an Autonomous AI Hijacked Aqua Trivy to Weaponize Developer Copilots

Do Son March 4, 2026 0

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

PlugX Evolves: New “Meeting Invitation” Phishing Campaign Leverages Trusted Security Software Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Malware

PlugX Evolves: New “Meeting Invitation” Phishing Campaign Leverages Trusted Security Software

Do Son March 4, 2026 0

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM image_18_1772539903dkCSeaHBoZ
  • Press Release

Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM

cybernewswire March 3, 2026 0
San Francisco, CA, United States, 3rd March 2026, CyberNewswire
Read More Read more about Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM
Cyber Escalation: Multi-Vector Attacks Surge Following “Operation Epic Fury” GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security

Cyber Escalation: Multi-Vector Attacks Surge Following “Operation Epic Fury”

Do Son March 3, 2026 0

Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-83542CVSS 9.8
    Improper Control of Generation of Code ('Code Injection') in Apache OFBiz 24.09 before 24.09.08 on all platforms allows...
    📅 Updated: Nov 6, 2026
  • CVE-2026-82907CVSS 9.8
    Authentication Bypass by Capture-replay in ExternalLoginKeysManager in Apache OFBiz 24.09 before 24.09.08 on all platforms allows a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102894CVSS 9.1
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. From 0.7.1 until...
    📅 Updated: Nov 6, 2026
  • CVE-2026-86345CVSS 9.0
    A flaw was found in 389-ds-base. The server does not discard plaintext bytes already buffered from a client...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48752CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48751CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, instance snapshots ignore the `restricted.containers.lowlevel=block`...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48750CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, the `record-output` parameter of the...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.