Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Android 17 Bionic Bug Triggers String Parsing Flaw Android 17 Bionic bug causing wide character string parsing errors in libc
  • Android

Android 17 Bionic Bug Triggers String Parsing Flaw

Do Son October 16, 2026 0

A newly discovered Android 17 Bionic bug in wcscspn and wcspbrk causes premature string termination when processing non-ASCII characters on Pixel devices.
Mitsubishi Electric Patches Four Critical ICONICS Suite Vulnerabilities Mitsubishi Electric security advisory for ICONICS Suite vulnerabilities including CVE-2026-16438, CVE-2023-4863, and CVE-2026-16436
  • Vulnerability Report

Mitsubishi Electric Patches Four Critical ICONICS Suite Vulnerabilities

Do Son October 16, 2026 0

Review the Mitsubishi Electric security advisory fixing critical ICONICS Suite vulnerabilities, including CVE-2026-16438 and CVE-2026-16436.
Progress Software Patches Twelve High-Severity MOVEit Transfer Vulnerabilities Progress security bulletin detailing MOVEit Transfer vulnerabilities including CVE-2026-87093, CVE-2026-89067, and CVE-2026-89068
  • Vulnerability Report

Progress Software Patches Twelve High-Severity MOVEit Transfer Vulnerabilities

Do Son October 16, 2026 0

Review the Progress security bulletin fixing 12 MOVEit Transfer vulnerabilities, including high-severity flaws CVE-2026-87093 and CVE-2026-89067.
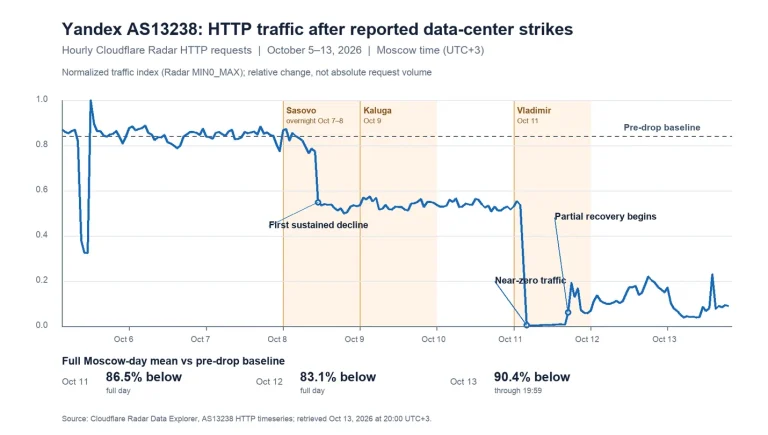
Russian Bot Traffic Resilient After Data Center Strikes Cloudflare telemetry graph analyzing Russian bot traffic and Yandex crawler disruption
  • Technology

Russian Bot Traffic Resilient After Data Center Strikes

Do Son October 16, 2026 0

Cloudflare telemetry reveals Russian bot traffic swiftly migrated to alternative clouds following drone strikes on Yandex data center infrastructure.
Backuply WordPress Plugin Patched for High-Severity SQL Injection Vulnerability Backuply WordPress plugin SQL injection vulnerability diagram showing CVE-2026-93953 privilege escalation impact
  • Vulnerability Report

Backuply WordPress Plugin Patched for High-Severity SQL Injection Vulnerability

Do Son October 16, 2026 0

Update the Backuply WordPress plugin to 1.5.9 to fix CVE-2026-93953, a high-severity SQL injection vulnerability impacting 600,000 sites.
AWS Patches Critical Amazon Neptune Vulnerability in Apache TinkerPop Gremlin Amazon Neptune vulnerability diagram showing Apache TinkerPop Gremlin flaw CVE-2026-110812 impact
  • Vulnerability Report

AWS Patches Critical Amazon Neptune Vulnerability in Apache TinkerPop Gremlin

Do Son October 16, 2026 0

Upgrade your DB cluster to fix CVE-2026-110812, a critical 9.9 CVSS Amazon Neptune vulnerability in Apache TinkerPop Gremlin.
Google AI Plus Changes Drop Pro Model Access Google AI Plus changes removing Pro model access in Gemini interface
  • Technology

Google AI Plus Changes Drop Pro Model Access

Do Son October 16, 2026 0

Google AI Plus changes take effect November 13, removing Pro model access in Gemini. Learn what this means for your subscription and pricing.
cURL Releases Version 8.23.0 to Fix Critical Flaw cURL CVE-2026-92392 vulnerability diagram illustrating HTTP/2 use-after-free flaw
  • Vulnerability Report

cURL Releases Version 8.23.0 to Fix Critical Flaw

Do Son October 15, 2026 0

The cURL CVE-2026-92392 vulnerability enables remote code execution during HTTP/2 uploads. Update to cURL 8.23.0 or disable HTTP/2 to protect systems.
Windows 11 Wi-Fi Authentication Broken by KB5127648 Windows 11 Wi-Fi authentication failure and enterprise 802.1X connection error
  • Windows

Windows 11 Wi-Fi Authentication Broken by KB5127648

Do Son October 15, 2026 0

The Windows 11 KB5127648 update breaks enterprise Windows 11 Wi-Fi authentication on 802.1X networks. Discover the root cause and registry workaround.
Claude Code Linux Kernel Patch Triples Read Speeds Claude Code Linux kernel memory management optimization and Linus Torvalds benchmark results
  • Linux

Claude Code Linux Kernel Patch Triples Read Speeds

Do Son October 15, 2026 0

Linus Torvalds used a Claude Code Linux kernel patch to triple small data read speeds via RCU memory management, though the experimental code needs testing.
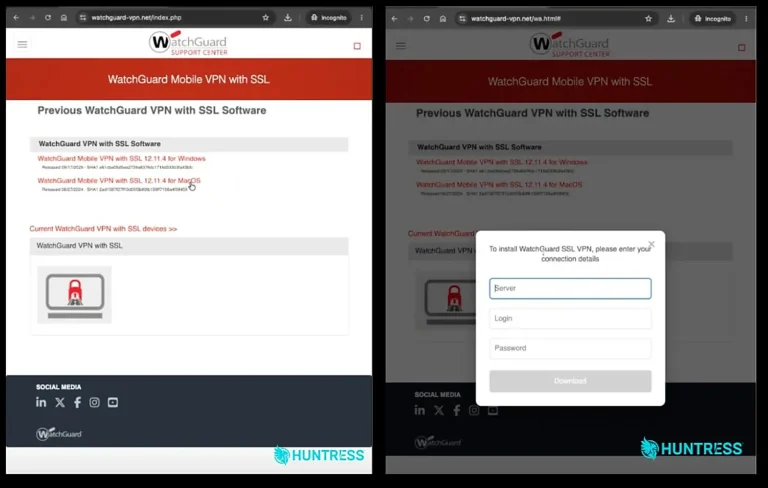
Fake WatchGuard VPN Site Steals Credentials Before Delivering Genuine Installer WatchGuard VPN phishing and WatchGuard VPN phishing site attack flow diagram
  • Malware

Fake WatchGuard VPN Site Steals Credentials Before Delivering Genuine Installer

Do Son October 15, 2026 0

Huntress uncovers a WatchGuard VPN phishing campaign where a WatchGuard VPN phishing site steals logins twice before serving the real client.
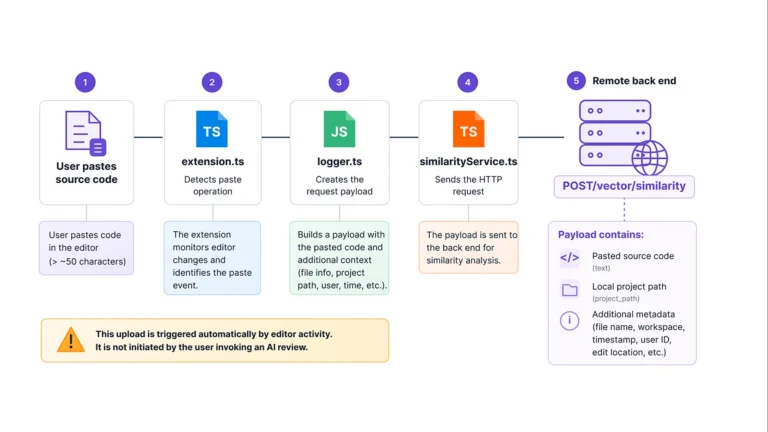
CodeAudit AI VS Code Extension Captures Developer Source Code in the Background CodeAudit AI extension and VS Code CodeAudit AIextension activity flow diagram
  • Malware

CodeAudit AI VS Code Extension Captures Developer Source Code in the Background

Do Son October 15, 2026 0

Akamai reveals the CodeAudit AI extension and VS Code CodeAudit AIextension upload pasted source code and metadata over unencrypted HTTP.
Next.js Fixes Two Critical Unauthenticated RCE Flaws in Out-of-Band Update Next.js security update fixes unauthenticated remote code execution flaws
  • Vulnerability Report

Next.js Fixes Two Critical Unauthenticated RCE Flaws in Out-of-Band Update

Do Son October 15, 2026 0

The Next.js security update fixes two critical unauthenticated remote code execution flaws, including CVE-2026-96889. Upgrade to 16.4.1 or 15.5.28.
Citrix Patches XenServer Host Escape Risks and UniconOS Privilege Escalation Flaws Citrix security update fixes XenServer and UniconOS privilege escalation vulnerabilities
  • Vulnerability Report

Citrix Patches XenServer Host Escape Risks and UniconOS Privilege Escalation Flaws

Do Son October 15, 2026 0

A Citrix security update fixes seven XenServer and UniconOS flaws, including guest-to-host and privilege escalation bugs. Patch hosts and thin clients.
Windows 11 Mouse Stutter Fixed in KB5127648 Update Windows 11 mouse stutter fix in KB5127648 gaming update
  • Windows

Windows 11 Mouse Stutter Fixed in KB5127648 Update

Do Son October 15, 2026 0

Microsoft fixes the frustrating Windows 11 mouse stutter and cursor drift issues in games with the new KB5127648 update for versions 24H2, 25H2, and 26H2.
SiteGuard Server Edition Flaw CVE-2026-106931 Exploited in the Wild for Root Access SiteGuard Server Edition vulnerability CVE-2026-106931 exploited in the wild for OS command injection
  • Vulnerability Report

SiteGuard Server Edition Flaw CVE-2026-106931 Exploited in the Wild for Root Access

Do Son October 15, 2026 0

A SiteGuard Server Edition vulnerability, CVE-2026-106931, is exploited in the wild and grants root or SYSTEM access. Update to Ver8.00 Update 5 now.
Google Updates Chrome VRP Rewards for Memory Flaws Chrome VRP rewards update for Google Chrome memory corruption vulnerabilities
  • Technology

Google Updates Chrome VRP Rewards for Memory Flaws

Do Son October 15, 2026 0

Google restructures its Chrome VRP rewards, raising baseline payouts for memory corruption bugs to $2,000 and offering up to $20,000 for critical exploits.
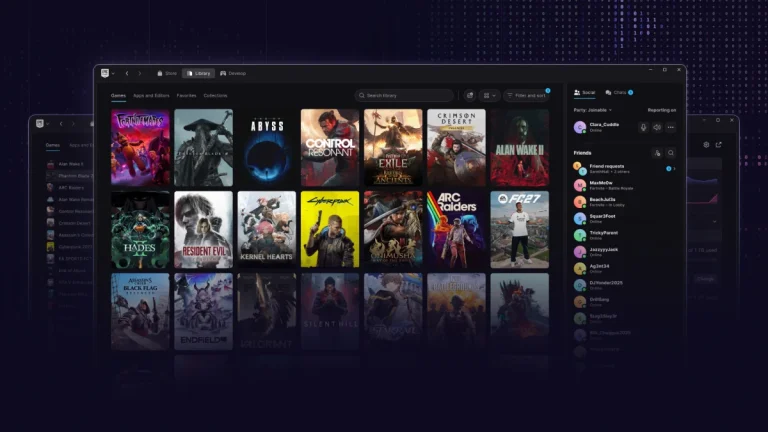
Epic Games Launcher Update Sparks Vibe Coding Backlash Epic Games Launcher update interface and Linux support comparison
  • Linux

Epic Games Launcher Update Sparks Vibe Coding Backlash

Do Son October 15, 2026 0

The new Epic Games Launcher update adds native Linux support and faster speeds, but its Vibe Coding marketing sparked massive backlash after recent layoffs.
Windows Blocks ReFS Removable Storage Starting in 2027 ReFS removable storage mounting block policy in Windows 11 and Windows Server
  • Windows

Windows Blocks ReFS Removable Storage Starting in 2027

Do Son October 15, 2026 0

Microsoft now audits ReFS removable storage in Windows 11 and will block mounting external ReFS volumes by default starting in January 2027.
npm Trusted Publishing Now Expires After 48 Hours npm trusted publishing configuration tied to a GitHub repository name, exposed to a repository name reuse attack before its first publish
  • Technology

npm Trusted Publishing Now Expires After 48 Hours

Do Son October 15, 2026 0

GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
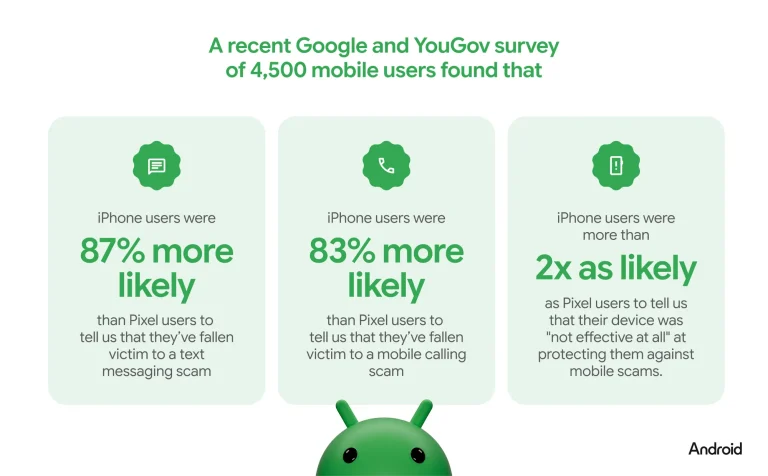
Android Scam Protection Gets Gemini AI Upgrades Android scam protection warning in Google Messages powered by Gemini scam detection, flagging a suspicious wrong-number text
  • Android

Android Scam Protection Gets Gemini AI Upgrades

Do Son October 15, 2026 0

New Android scam protection uses Gemini to flag scam chats, scan links on-device, mask shared screens, and block call forwarding attacks.

Juniper Networks Patches Critical Junos OS Vulnerabilities Across Core Platforms Junos OS vulnerabilities overview showing Juniper security bulletin fixes for CVE-2026-102182, CVE-2026-101954, and CVE-2026-33792
  • Vulnerability Report

Juniper Networks Patches Critical Junos OS Vulnerabilities Across Core Platforms

Do Son October 15, 2026 0

Review the latest Juniper security bulletin to patch critical Junos OS vulnerabilities, including RCE flaws CVE-2026-102182 and CVE-2026-101954.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.