Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Sandbox Bypassed: jsPDF Flaw Exposes Millions to Object Injection CVE-2026-31938 jsPDF Vulnerability CVE-2026-25755 jsPDF, CVE-2025-68428 jsPDF Vulnerability CVE-2026-24133
  • Vulnerability Report

Sandbox Bypassed: jsPDF Flaw Exposes Millions to Object Injection

Do Son February 23, 2026 0

A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
The Fake IT Threat: “TrustConnect” Malware-as-a-Service Masquerades as Legitimate RMM Software TrustConnect Malware Fake RMM MaaS
  • Cybercriminals

The Fake IT Threat: “TrustConnect” Malware-as-a-Service Masquerades as Legitimate RMM Software

Do Son February 23, 2026 0

Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

Weaponizing Windows Errors: PoC Dropped for Critical Privilege Escalation Flaw in WER Service C Windows SecureBoot folder KB5089549 Windows 11 BSOD Microsoft Windows, Rust programming WINS Service Deprecation Windows Server DNS Migration Windows Driver Standard OEM Kernel Privileges Windows Agentic OS Task Manager Bug, Windows 11 Performance Windows 11, Microsoft, WinRE, Update Bug, Tech Support Windows 11 OOBE, Microsoft Account Mandatory Windows 11, SSD failures Windows 11 Recovery, Black Screen of Death Windows 11 Update Issue, KB5062324 Windows 11, Indicator Bar
  • Vulnerability

Weaponizing Windows Errors: PoC Dropped for Critical Privilege Escalation Flaw in WER Service

Do Son February 23, 2026 0

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

Industrialized Theft: GoldFactory Malware Hijacks Tax Season via Fake ‘Coretax’ Apps Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cybercriminals

Industrialized Theft: GoldFactory Malware Hijacks Tax Season via Fake ‘Coretax’ Apps

Do Son February 23, 2026 0

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.
Streaming Fraud: “Massiv” Android Trojan Uses Fake IPTV Apps for Complete Device Takeover Massiv Android Malware IPTV Banking Trojan
  • Malware

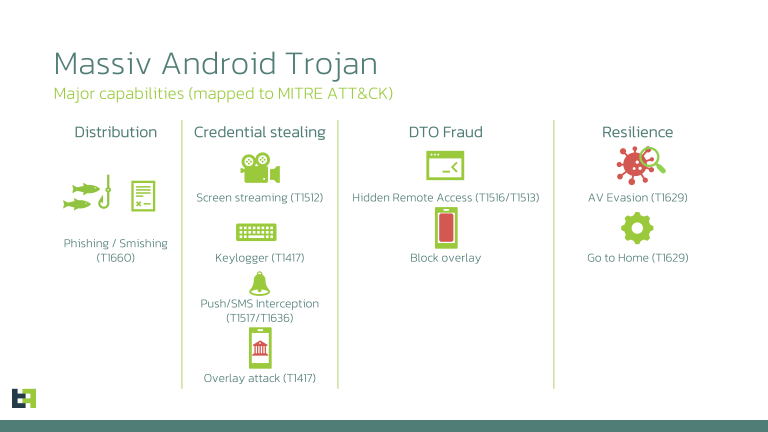
Streaming Fraud: “Massiv” Android Trojan Uses Fake IPTV Apps for Complete Device Takeover

Do Son February 23, 2026 0

ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Maintaining the critical minimum through energy monitoring during storm disruptions CVE-2024-31070 & CVE-2024-36491
  • Technique

Maintaining the critical minimum through energy monitoring during storm disruptions

Do Son February 21, 2026 0

Technical analysis of energy monitoring and load prioritization strategies for maintaining smart home stability during grid outages.

Inside the ‘Upworksell’ Syndicate: Hacker Gets 60 Months for Funneling US Tech Jobs to North Korea Romanian hacker sentenced identity theft conviction Pig-Butchering Crackdown Operation Level Up Oleksandr Didenko North Korean IT Workers Coinbase TaskUs insider breach, Hyderabad police Coinbase arrest Scattered Spider, Cybercrime Scattered Spider group
  • Cybercriminals

Inside the ‘Upworksell’ Syndicate: Hacker Gets 60 Months for Funneling US Tech Jobs to North Korea

Do Son February 20, 2026 0

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.

Exploited in the Wild & PoC Disclosed: Emergency Chrome Zero-Day (CVE-2026-2441) Patched Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Exploited in the Wild & PoC Disclosed: Emergency Chrome Zero-Day (CVE-2026-2441) Patched

Do Son February 20, 2026 0

Google patches Chrome zero-day CVE-2026-2441, an actively exploited memory flaw. With PoC exploit code now publicly disclosed, update to v145 immediately.

Bypassing the Bouncer: Apache Tomcat Patches SNI & Legacy Protocol Flaws Tomcat Security Update CVE-2026-24733 CVE-2023-41081 -CVE-2024-56337
  • Vulnerability Report

Bypassing the Bouncer: Apache Tomcat Patches SNI & Legacy Protocol Flaws

Do Son February 20, 2026 0

Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.

The Dev Environment Trap: 128 Million Users at Risk as Top VS Code Extensions Unmask Critical Flaws VS Code extension vulnerabilities 2026
  • Vulnerability Report

The Dev Environment Trap: 128 Million Users at Risk as Top VS Code Extensions Unmask Critical Flaws

Do Son February 20, 2026 0

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?

Google Unveils Gemini 3.1 Pro with 1 Million Tokens for Deep-Data Mastery Google Gemini Pentagon deal Google AI Pro 5TB storage Gemini 3.1 Pro launch
  • Technology

Google Unveils Gemini 3.1 Pro with 1 Million Tokens for Deep-Data Mastery

Do Son February 20, 2026 0

Google debuts Gemini 3.1 Pro! With a 1M token context window and native multi-modal power, it’s the new gold standard for complex analysis and big data.
Infoblox Exposes Hybrid Malvertising & “Pig Butchering” Scam Hybrid Crypto Scam Pig Butchering Malvertising
  • Cybercriminals

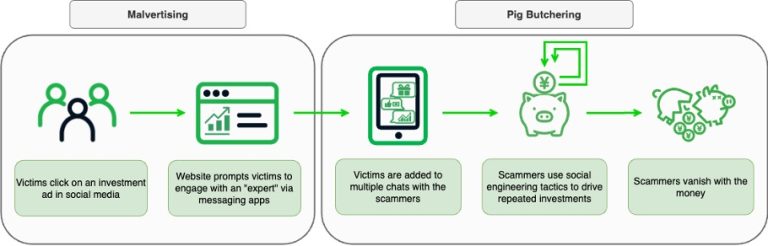
Infoblox Exposes Hybrid Malvertising & “Pig Butchering” Scam

Do Son February 20, 2026 0

Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.

PoC Publicly Disclosed: Critical Grandstream VoIP Flaw (CVSS 9.3) Grants Stealthy Root Access Grandstream VoIP Zero-Day CVE-2026-2329 PoC
  • Vulnerability Report

PoC Publicly Disclosed: Critical Grandstream VoIP Flaw (CVSS 9.3) Grants Stealthy Root Access

Do Son February 20, 2026 0

Rapid7 publicly discloses a critical zero-day and PoC (CVE-2026-2329) for Grandstream GXP1600 VoIP phones allowing remote root access. Patch now.

Trojan Routers: Texas Sues TP-Link Over Alleged CCP Surveillance and Supply Chain Deception TP-Link Lawsuit CCP Surveillance
  • Malware

Trojan Routers: Texas Sues TP-Link Over Alleged CCP Surveillance and Supply Chain Deception

Do Son February 20, 2026 0

Texas AG Ken Paxton sues TP-Link, alleging the Wi-Fi giant's routers act as Trojan horses for CCP surveillance. State bans TP-Link gear for employees.
How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags CVE-2025-20059
  • Technique

How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags

Do Son February 20, 2026 0
In the increasingly regulated world of crypto derivatives, managing multiple exchange accounts has become a common practice....
Read More Read more about How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags
CVE-2025-65717: Critical Vulnerability in VS Code’s Live Server Extension Puts 72 Million Developers at Risk, No Patch image-19
  • Vulnerability Report

CVE-2025-65717: Critical Vulnerability in VS Code’s Live Server Extension Puts 72 Million Developers at Risk, No Patch

Do Son February 20, 2026 0

Critical VS Code Live Server flaw CVE-2025-65717 (CVSS 9.1) lets attackers steal source code and credentials via malicious links. Protect your workspace now.

1.75 Million Apps Blocked: Google’s AI-Driven War on Android Malware in 2025 Google Play Security Android 16 Tapjacking Protection
  • Android
  • Malware

1.75 Million Apps Blocked: Google’s AI-Driven War on Android Malware in 2025

Do Son February 20, 2026 0

Google's VP Vijaya Kaza reveals 1.75M bad apps blocked in 2025. Android 16 introduces one-line tapjacking protection to fight AI-powered cyber threats.

The Symphonic Chatbot: How Google’s Gemini and Lyria 3 are Turning Every Prompt into a Hit Song Chrome hidden weights.bin download Gemini Nano privacy controversy 2026 Google Antigravity account suspension Gemini Lyria 3 integration Google Gemini enterprise sales, Google Cloud AI revenue 2026 Google Gemini daily limits 2026, Gemini Thinking model quotas Google Gemini 3 Agentic Development Platform
  • Technology

The Symphonic Chatbot: How Google’s Gemini and Lyria 3 are Turning Every Prompt into a Hit Song

Do Son February 20, 2026 0

Gemini meets Lyria 3! Generate 30-second high-fidelity songs from text, photos, or video. Discover the future of AI-driven musical creation today.

The Strategic Divorce: Why NVIDIA Sold Its Arm Shares While Doubling Down on Its Architecture NVIDIA GPU Security CUDA-Q Vulnerability NVIDIA Apex Vulnerability AI Infrastructure Security NVIDIA Cumulus Linux CVE-2025-33179 NVIDIA Arm divestment NVIDIA DGX Spark, CVE-2025-33187 NVIDIA Isaac-GROOT, Code Injection Megatron-LM Vulnerability, AI Code Injection NVIDIA China NVIDIA GPUs, Hardware Kill Switches NVIDIA Megatron-LM, LLM Vulnerabilities NVIDIA Base Command Manager - CVE-2024-0138
  • Technology

The Strategic Divorce: Why NVIDIA Sold Its Arm Shares While Doubling Down on Its Architecture

Do Son February 20, 2026 0

NVIDIA has fully divested its $156M stake in Arm. Is it a rift or a calculated move as Arm prepares to build its own chips? Discover the new "Grace" strategy.

The Wristband Revolution: Meta’s Revived Smartwatch Aims to Control the Future of AR Meta Malibu 2 smartwatch Solos Technology vs Meta lawsuit, Ray-Ban Meta patent infringement
  • Technology

The Wristband Revolution: Meta’s Revived Smartwatch Aims to Control the Future of AR

Do Son February 20, 2026 0

Meta's "Malibu 2" smartwatch is back! Discover how neural sensors and EMG gestures will turn this wearable into the ultimate controller for Meta's AR ecosystem.

The Private Powerhouse: How Meta’s $135B NVIDIA Bet is Bringing Stealth AI to WhatsApp WhatsApp Confidential Computing
  • Technology

The Private Powerhouse: How Meta’s $135B NVIDIA Bet is Bringing Stealth AI to WhatsApp

Do Son February 19, 2026 0

Meta is spending $135B to bring NVIDIA’s "Confidential Computing" to WhatsApp. Get AI assistance without breaking the sanctity of end-to-end encryption.
The Designer in the Machine: How WordPress’s New AI Concierge is Killing Layout Frustration WordPress Persistent AI Assistant
  • Technology

The Designer in the Machine: How WordPress’s New AI Concierge is Killing Layout Frustration

Do Son February 19, 2026 0

WordPress.com launches a Persistent AI Assistant to handle CSS, font styling, and image editing. Turn natural language into a professional site design instantly.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.