Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google Pixel 10a Perfects the Mid-Range with 3,000 Nits and Satellite SOS Pixel reboot loop bug, Pixel factory reset, Pixel software update issue, Pixel boot loop fix Google Pixel 10a pre-order
  • Android

Google Pixel 10a Perfects the Mid-Range with 3,000 Nits and Satellite SOS

Do Son February 19, 2026 0

Google Pixel 10a is here! For $499, get a 3,000-nit Actua display, Satellite SOS, and 7 years of updates. The mid-range "definitive" evolution has arrived.

Beyond the Lens: Samsung Unveils the Galaxy S26’s AI-Powered “Luminous Metamorphosis” Galaxy S26 AI Camera Galaxy Unpacked 2026
  • Android

Beyond the Lens: Samsung Unveils the Galaxy S26’s AI-Powered “Luminous Metamorphosis”

Do Son February 19, 2026 0

Samsung’s Galaxy S26 turns day into night with "Luminous Metamorphosis." Discover the AI-orchestrated camera workflow destined to redefine mobile photography.

Live from Your Webcam: Remcos RAT Evolves into a Real-Time Surveillance Nightmare WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Malware

Live from Your Webcam: Remcos RAT Evolves into a Real-Time Surveillance Nightmare

Do Son February 19, 2026 0

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.

Splunk Windows Flaws Expose Servers to System Takeover Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Windows Flaws Expose Servers to System Takeover

Do Son February 19, 2026 0

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.
Hackers Weaponize DocuSign and SimpleHelp in Stealthy New Campaign DocuSign Phishing SimpleHelp Malware
  • Malware

Hackers Weaponize DocuSign and SimpleHelp in Stealthy New Campaign

Do Son February 19, 2026 0

Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

CVE-2026-26016: Critical Pterodactyl API Flaw (CVSS 9.2) Exposes Entire Server Networks Pterodactyl Vulnerability CVE-2026-26016
  • Vulnerability Report

CVE-2026-26016: Critical Pterodactyl API Flaw (CVSS 9.2) Exposes Entire Server Networks

Do Son February 19, 2026 0

Critical Pterodactyl API flaw (CVE-2026-26016) allows cross-node authorization bypass. Attackers can destroy game servers. Update to version 1.12.1 now.

High-Severity DoS Flaw Hits 46 Million ‘fast-xml-parser’ Downloads fast-xml-parser DoS CVE-2026-26278
  • Vulnerability Report

High-Severity DoS Flaw Hits 46 Million ‘fast-xml-parser’ Downloads

Do Son February 19, 2026 0

Node.js DoS flaw CVE-2026-26278 in fast-xml-parser freezes event loops via XML entity expansion. 46M weekly downloads affected. Update to version 5.3.6.

Apache Camel Patches Critical Keycloak & LevelDB Flaws Apache Camel K Vulnerability CVE-2026-45760 Build Deputy Apache Camel Security CVE-2026-23552 CVE-2025-27636 CVE-2025-29891 PoC
  • Vulnerability Report

Apache Camel Patches Critical Keycloak & LevelDB Flaws

Do Son February 19, 2026 0

Apache Camel patches critical flaws in Keycloak (CVE-2026-23552) and LevelDB (CVE-2026-25747) components that allow auth bypass and RCE. Update to 4.18.0.
CI/CD at Risk: High-Severity Jenkins XSS Flaw Exposes Build Environments Jenkins Security Update CVE-2026-27099 Jenkins security - CVE-2023-35141 Jenkins plugins, CVE-2025-47884
  • Vulnerability Report

CI/CD at Risk: High-Severity Jenkins XSS Flaw Exposes Build Environments

Do Son February 19, 2026 0

Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.

AI Under Control: Link11 Launches AI Management Dashboard for Clean Traffic AI_Managament_Dashboard_17715024897h3GvpajHj
  • Press Release

AI Under Control: Link11 Launches AI Management Dashboard for Clean Traffic

cybernewswire February 19, 2026 0
Frankfurt am Main, Germany, 19th February 2026, CyberNewswire
Read More Read more about AI Under Control: Link11 Launches AI Management Dashboard for Clean Traffic
Urgent Chrome Patch: Google Fixes High-Severity PDF and V8 Engine Flaws Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Urgent Chrome Patch: Google Fixes High-Severity PDF and V8 Engine Flaws

Do Son February 19, 2026 0

Google releases an urgent Chrome update to patch high-severity flaws in PDFium (CVE-2026-2648) and the V8 engine (CVE-2026-2649). Update to 145 now.

Tutorials of Terror: How NVIDIA’s AI Training Guides Became a Gateway for Code Injection NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability Report

Tutorials of Terror: How NVIDIA’s AI Training Guides Became a Gateway for Code Injection

Do Son February 18, 2026 0

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.

Elon Musk’s Grok Faces “Large-Scale” EU Probe Over Deepfake Imagery and Data Rights EU GDPR Grok investigation xAI crypto trader recruitment X open-source algorithm 2026, Elon Musk ad transparency X Chat Replacement X End-to-End Encryption xAI, open-source xAI Elon Musk xAI Infrastructure, Saudi AI
  • Technology

Elon Musk’s Grok Faces “Large-Scale” EU Probe Over Deepfake Imagery and Data Rights

Do Son February 18, 2026 0

The EU’s primary regulator has launched a massive GDPR probe into xAI's Grok. From deepfake porn to data theft, can Elon Musk’s AI survive the legal onslaught?

The Tiny Titan: Why Raspberry Pi is the Unexpected King of the AI Agent Revolution Raspberry Pi AI Agents Raspberry Pi 4 dual-memory revision Raspberry Pi Price Hike AI Memory Demand
  • Technology

The Tiny Titan: Why Raspberry Pi is the Unexpected King of the AI Agent Revolution

Do Son February 18, 2026 0

A 42% stock surge and the rise of "Edge Inference" have transformed the Raspberry Pi into the premier low-cost vessel for autonomous AI agents in 2026.

Beyond the Chatbot: Google I/O 2026 to Unveil the “Agentic” Future of Android 17 Google I/O 2026 dates
  • Technology

Beyond the Chatbot: Google I/O 2026 to Unveil the “Agentic” Future of Android 17

Do Son February 18, 2026 0

Google I/O 2026 kicks off May 19! Discover how Gemini 3 and Android 17 are turning your phone into a proactive AI concierge. The era of the agent is here.

Critical Honeywell CCTV Flaw (CVSS 9.8) Allows Unauthenticated Takeover Honeywell CCTV Vulnerability CVE-2026-1670 EagleMsgSpy Spyware Tool ResidentBat Spyware, Belarusian KGB Surveillance
  • Vulnerability Report

Critical Honeywell CCTV Flaw (CVSS 9.8) Allows Unauthenticated Takeover

Do Son February 18, 2026 0

CISA warns of Honeywell CCTV flaw CVE-2026-1670. Unauthenticated attackers can reset passwords & hijack feeds. Update firmware immediately.

New CRESCENTHARVEST Malware Targets Iranian Dissidents Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

New CRESCENTHARVEST Malware Targets Iranian Dissidents

Do Son February 18, 2026 0

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

Fake Jobs, Real Theft: “Contagious Interview” Malware Drains Crypto Wallets Contagious Interview Campaign MetaMask Malware
  • Cybercriminals

Fake Jobs, Real Theft: “Contagious Interview” Malware Drains Crypto Wallets

Do Son February 18, 2026 0

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.

The “I Paid Twice” Trap: New Booking.com Phishing Kit Targets Hotels & Guests Booking.com Fraud Hospitality Phishing
  • Cybercriminals

The “I Paid Twice” Trap: New Booking.com Phishing Kit Targets Hotels & Guests

Do Son February 18, 2026 0

Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.
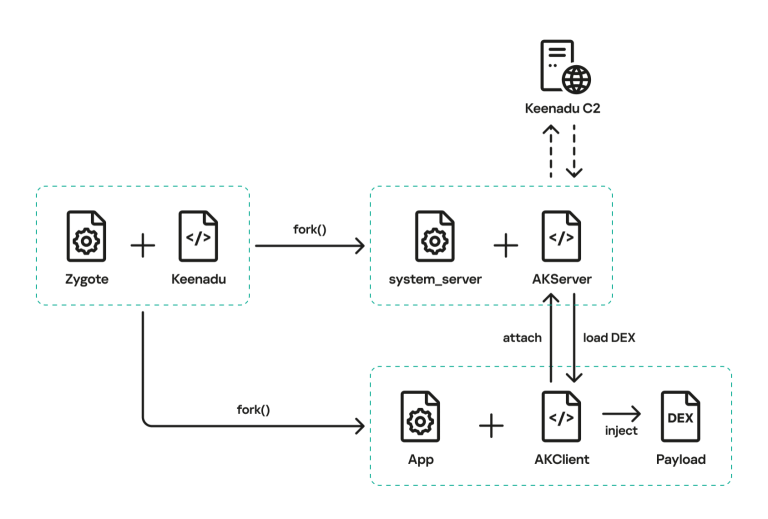
Infected Out of the Box: “Keenadu” Backdoor Hijacks Android at the Firmware Level Keenadu Malware Android Firmware Backdoor
  • Malware

Infected Out of the Box: “Keenadu” Backdoor Hijacks Android at the Firmware Level

Do Son February 18, 2026 0

Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.

PostgreSQL Fixes 5 Security Flaws Including Critical Code Execution Risks PostgreSQL Vulnerabilities CVE-2026-2006 PostgreSQL, security update CVE-2023-5869 - CVE-2025-1094
  • Vulnerability Report

PostgreSQL Fixes 5 Security Flaws Including Critical Code Execution Risks

Do Son February 18, 2026 0

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.

Ghost NICs & Secret Knocks: Dell Zero-Day (CVSS 10) Exploited by UNC6201 FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Cyber Security
  • Vulnerability Report

Ghost NICs & Secret Knocks: Dell Zero-Day (CVSS 10) Exploited by UNC6201

Do Son February 18, 2026 0

Mandiant reveals UNC6201 exploiting Dell RecoverPoint zero-day CVE-2026-22769. Attackers use "Ghost NICs" & GRIMBOLT malware. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.