Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Lumma Stealer Resurfaces After Doxxing with New Browser Fingerprinting to Target High-Value Victims Lumma Browser Fingerprinting, Infostealer Resurgence
  • Malware

Lumma Stealer Resurfaces After Doxxing with New Browser Fingerprinting to Target High-Value Victims

Do Son November 17, 2025 0

Despite a recent doxxing attempt, Lumma Stealer has resurfaced, integrating browser fingerprinting into its C&C to collect WebGL/Canvas signatures for sandbox evasion and victim assessment.

Phishing-as-a-Service Uncovered: Automated Kit Impersonates Aruba S.p.A. to Steal Credentials and Credit Cards Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cybercriminals

Phishing-as-a-Service Uncovered: Automated Kit Impersonates Aruba S.p.A. to Steal Credentials and Credit Cards

Do Son November 17, 2025 0

Group-IB exposed an automated PhaaS kit that impersonates Aruba S.p.A. to steal credentials, credit card details, and OTPs. The multi-stage scam uses a CAPTCHA filter and Telegram for real-time exfiltration.
New Yurei Ransomware Emerges: Go-Based Threat Uses ChaCha20-Poly1305 for Irreversible Double Extortion Yurei Ransomware, GoLang ChaCha20
  • Malware

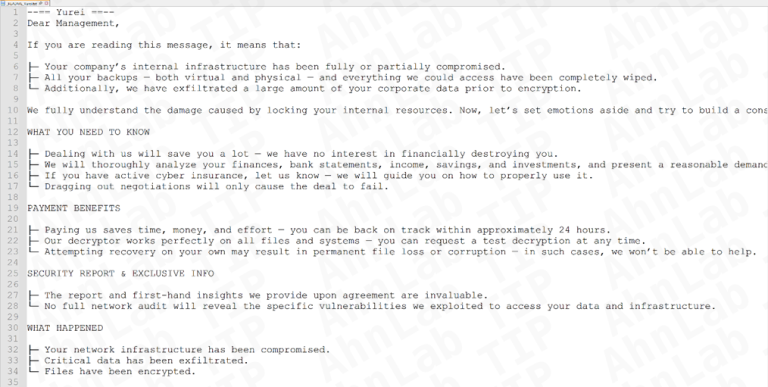
New Yurei Ransomware Emerges: Go-Based Threat Uses ChaCha20-Poly1305 for Irreversible Double Extortion

Do Son November 17, 2025 0

ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.

The Em Dash is Gone: Sam Altman Confirms ChatGPT Finally Dumps Its Most Annoying Habit OpenAI desktop Super App GPT-4o retirement date AI Model Collapse ChatGPT Personalization Characteristics, OpenAI Tone Sliders 2025 ChatGPT Ads OpenAI Losses AI browser, ChatGPT Atlas ChatGPT Em Dash AI Writing Quirks
  • Technology

The Em Dash is Gone: Sam Altman Confirms ChatGPT Finally Dumps Its Most Annoying Habit

Do Son November 16, 2025 0

Sam Altman confirmed ChatGPT has fixed its overuse of the em dash. The model will now respect Custom Instructions to stop using the punctuation, removing a clear AI tell.

X (Twitter) Launches ‘Chat’ to Replace DMs, Adding E2E Encryption and Video Calling EU GDPR Grok investigation xAI crypto trader recruitment X open-source algorithm 2026, Elon Musk ad transparency X Chat Replacement X End-to-End Encryption xAI, open-source xAI Elon Musk xAI Infrastructure, Saudi AI
  • Technology

X (Twitter) Launches ‘Chat’ to Replace DMs, Adding E2E Encryption and Video Calling

Do Son November 16, 2025 0

X (Twitter) launched 'Chat' to replace DMs, adding video/voice calling, file sharing, editing, and E2E encryption for messages on iOS and web. Android is coming soon.

Google to Invest $40 Billion in Texas for Next-Gen Cloud and AI Data Centers Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Google to Invest $40 Billion in Texas for Next-Gen Cloud and AI Data Centers

Do Son November 16, 2025 0

Google announced a $40B investment in Texas by 2027 to build new cloud and AI data centers. The plan includes a $30M Energy Impact Fund and workforce training.

Barrier Removed: Microsoft Makes Xbox Game Publishing Guide Public for All Developers Xbox Publishing Guide Indie Dev Barriers Xbox profit margin, Microsoft layoffs Gaming Copilot
  • Technology

Barrier Removed: Microsoft Makes Xbox Game Publishing Guide Public for All Developers

Do Son November 15, 2025 0

Microsoft publicly released the Xbox Game Publishing Guide, previously partner-only, to remove barriers and make it easier for all developers to launch titles on Xbox and PC.

WhatsApp Interoperability Live: Meta Confirms DMA Integration with BirdyChat and Haiket WhatsApp antitrust API probe India SIM-Binding Mandate Messaging App KYC WhatsApp DMA Interoperability BirdyChat Haiket Denmark Social Media Ban CVE-2025-55177 WhatsApp vulnerability, zero-click flaw npm Malware, System Wipe WhatsApp Windows App, WebView2 Downgrade WhatsApp Ban, US House NSO WhatsApp, Pegasus Spyware WhatsApp iPad iPadOS app
  • Technology

WhatsApp Interoperability Live: Meta Confirms DMA Integration with BirdyChat and Haiket

Do Son November 15, 2025 0

Meta confirmed WhatsApp is ready for DMA interoperability with third-party apps BirdyChat and Haiket. European users can soon opt in to cross-platform chats.

Project Kuiper is Now Amazon Leo: Amazon Rebrands Satellite Initiative for Commercial Launch Amazon Leo Project Kuiper Rebrand
  • Technology

Project Kuiper is Now Amazon Leo: Amazon Rebrands Satellite Initiative for Commercial Launch

Do Son November 15, 2025 0

Amazon officially rebranded its LEO satellite initiative, formerly Project Kuiper, as Amazon Leo, signaling its readiness to transition the network into a commercial product.

What Is An SPF Checker? Benefits Of SPF Validation For Your Domain domain
  • Technique

What Is An SPF Checker? Benefits Of SPF Validation For Your Domain

Do Son November 15, 2025 0
Sender Policy Framework (SPF) is a vital component of modern email authentication protocols, designed to combat email...
Read More Read more about What Is An SPF Checker? Benefits Of SPF Validation For Your Domain
Symfony Patches PATH_INFO Parsing Flaw Leading to Authorization Bypass (CVE-2025-64500) Symfony Path Info Flaw, Authorization Bypass
  • Vulnerability Report

Symfony Patches PATH_INFO Parsing Flaw Leading to Authorization Bypass (CVE-2025-64500)

Do Son November 15, 2025 0

Symfony patched a High-severity flaw (CVE-2025-64500) in its Request component. Improper PATH_INFO parsing allows attackers to bypass access control rules in vulnerable applications.

Cisco Warns of High-Severity Privilege Escalation Flaw (CVE-2025-20341) in Catalyst Center Virtual Appliance Cisco Catalyst EoP, CVE-2025-20341
  • Vulnerability Report

Cisco Warns of High-Severity Privilege Escalation Flaw (CVE-2025-20341) in Catalyst Center Virtual Appliance

Do Son November 15, 2025 0

Cisco patched a High-severity EoP flaw (CVE-2025-20341) in Catalyst Center Virtual Appliance. A low-privileged Observer user can remotely elevate privileges to Administrator via a crafted HTTP request.

App Store Cuts Commission to 15% for Mini Apps to Expand Services Vibe Coding apps Vibe Coding App Store surge Vibe Coding App Store Apple 50th Anniversary hardware Brazil CADE Apple settlement, iOS third-party app stores Brazil Tim Cook Succession Apple CEO Rumors App Store Mini Apps 15% Commission Fee iOS Japan Sideloading, Third-Party App Stores Web App Store, App Discovery Apple Age Verification, Texas SB2420 Apple AI acquisitions App Store, Antitrust Apple WebKit, Japan Regulations App Store Age Ratings, Parental Controls Apple App Store, Epic Games Lawsuit
  • Technology

App Store Cuts Commission to 15% for Mini Apps to Expand Services

Do Son November 14, 2025 0

Apple launched the Mini Apps Partner Program, cutting the App Store commission fee in half—from 30% to 15%—for eligible developers of self-contained web-based services.
5 KPIs to Measure When You Introduce AI SOC Agents CVE-2025-20059
  • Technique

5 KPIs to Measure When You Introduce AI SOC Agents

Do Son November 14, 2025 0
“Is it working?” It can be easy to drop an AI SOC agent into your environment and...
Read More Read more about 5 KPIs to Measure When You Introduce AI SOC Agents
ZERO-DAY ATTACK WARNING: Fortinet FortiWeb Exploit Grants Unauthenticated Admin Access! Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability Report

ZERO-DAY ATTACK WARNING: Fortinet FortiWeb Exploit Grants Unauthenticated Admin Access!

Do Son November 14, 2025 0

Cybersecurity firms warn of a Critical, actively exploited FortiWeb flaw that allows unauthenticated attackers to create a new administrator account on the FortiWeb Manager panel. Update to v8.0.2 immediately.
Critical ASUS DSL Router Flaw (CVE-2025-59367, CVSS 9.3) Allows Unauthenticated Remote Access ASUS DSL Router, Authentication Bypass Cyclops Blink malware
  • Vulnerability Report

Critical ASUS DSL Router Flaw (CVE-2025-59367, CVSS 9.3) Allows Unauthenticated Remote Access

Do Son November 14, 2025 0

ASUS released an urgent patch for a Critical (CVSS 9.3) Auth Bypass flaw (CVE-2025-59367) in its DSL Series Routers. The bug allows remote attackers to gain unauthorized access without credentials. Update firmware immediately.

Qualcomm Launches Dragonwing IQ-X: Oryon CPU Brings 45 TOPS Edge AI to Factory PCs Dragonwing IQ-X Industrial Edge AI
  • Technology

Qualcomm Launches Dragonwing IQ-X: Oryon CPU Brings 45 TOPS Edge AI to Factory PCs

Do Son November 14, 2025 0

Qualcomm launches Dragonwing IQ-X, its first industrial PC processor with Oryon CPUs, 45 TOPS of AI power, and a rugged design for factory edge controllers.

GPT-5.1 Arrives: OpenAI Unveils ‘Adaptive Reasoning’ & New Human-Like Chat Styles GPT-5.1 Instant Adaptive Reasoning
  • Technology

GPT-5.1 Arrives: OpenAI Unveils ‘Adaptive Reasoning’ & New Human-Like Chat Styles

Do Son November 14, 2025 0

OpenAI released GPT-5.1 Instant/Thinking with "adaptive reasoning" for slower, deeper thinking. It also adds new chat styles like Professional, Candid, and Quirky.

macOS Tahoe Beta Reveals ‘Edge Light’: Apple’s New AI-Driven Virtual Ring Light for Video Calls macOS Edge Light MacBook Ring Light
  • Technology

macOS Tahoe Beta Reveals ‘Edge Light’: Apple’s New AI-Driven Virtual Ring Light for Video Calls

Do Son November 14, 2025 0

macOS Tahoe 26.2 beta reveals "Edge Light," an AI-driven virtual ring light that uses the display edges and Neural Engine to optimize illumination for video calls.

Windows Agentic OS Revealed: Microsoft Aims to Transform Windows 11 into an AI-First Platform C Windows SecureBoot folder KB5089549 Windows 11 BSOD Microsoft Windows, Rust programming WINS Service Deprecation Windows Server DNS Migration Windows Driver Standard OEM Kernel Privileges Windows Agentic OS Task Manager Bug, Windows 11 Performance Windows 11, Microsoft, WinRE, Update Bug, Tech Support Windows 11 OOBE, Microsoft Account Mandatory Windows 11, SSD failures Windows 11 Recovery, Black Screen of Death Windows 11 Update Issue, KB5062324 Windows 11, Indicator Bar
  • Windows

Windows Agentic OS Revealed: Microsoft Aims to Transform Windows 11 into an AI-First Platform

Do Son November 14, 2025 0

Microsoft revealed plans for an "Agentic OS," transforming Windows 11 into an AI-first platform using the Model Context Protocol (MCP) to let AI agents interact with native apps.

Sui Blockchain Seed Stealer: Malicious Chrome Extension Hides Mnemonic Exfiltration in Microtransactions Chrome Crypto Stealer, Sui Blockchain Exfiltration
  • Malware

Sui Blockchain Seed Stealer: Malicious Chrome Extension Hides Mnemonic Exfiltration in Microtransactions

Do Son November 14, 2025 0

A malicious Chrome extension, Safery: Ethereum Wallet, steals BIP-39 seed phrases by encoding them into synthetic Sui blockchain addresses and broadcasting microtransactions, bypassing HTTP/C2 detection.

High-Severity NVIDIA NeMo Framework Flaws Allow Code Injection and Privilege Escalation in AI Pipelines NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability Report

High-Severity NVIDIA NeMo Framework Flaws Allow Code Injection and Privilege Escalation in AI Pipelines

Do Son November 14, 2025 0

NVIDIA patched two High-severity flaws in its NeMo Framework. CVE-2025-23361 and CVE-2025-33178 allow local code injection and privilege escalation in AI training environments. Update to v2.5.0.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.