Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
iPhone Air 2 Cancelled: Apple Shifts to Split Release Cycle for Foldable iPhone iOS 27 AirDrop speed, AirDrop transfer speed, AirDrop file transfer, AWDL protocol iPhone 17e rumors iPhone Air 2 Roadmap Apple Launch Cadence Shift iPhone Air sales collapse Apple iPhone Fold iPhone Air, thinnest iPhone camera flaw
  • Technology

iPhone Air 2 Cancelled: Apple Shifts to Split Release Cycle for Foldable iPhone

Do Son November 17, 2025 0

Mark Gurman says the iPhone Air 2 is cancelled, confirming Apple will shift to a split release cycle: high-end/Fold in Fall 2026, followed by standard models in Spring 2027.

Critical pgAdmin Flaws (CVE-2025-12762, CVSS 9.1) Allow Remote Code Execution via PostgreSQL Dump Files CVE-2023-5002 pgAdmin RCE, LDAP Injection
  • Vulnerability Report

Critical pgAdmin Flaws (CVE-2025-12762, CVSS 9.1) Allow Remote Code Execution via PostgreSQL Dump Files

Do Son November 17, 2025 0

pgAdmin patched four flaws. The Critical RCE (CVE-2025-12762) risks arbitrary code execution via malicious PostgreSQL dump files. LDAP Injection (CVE-2025-12764) and TLS Bypass were also fixed. Update to v9.10.

High-Severity Memos Flaw (CVE-2024-21635) Allows Hackers to Stay Logged In After Password Change Memos Session Flaw, Token Invalidation
  • Vulnerability Report

High-Severity Memos Flaw (CVE-2024-21635) Allows Hackers to Stay Logged In After Password Change

Do Son November 17, 2025 0

A High-severity flaw (CVE-2024-21635) in Memos fails to invalidate Access Tokens upon password change, allowing attackers to maintain access to the knowledge base. Update to v0.25.2.

HelloKitty Successor Kraken Ransomware Hits Windows/ESXi, Benchmarks Victim Performance Before Encryption Kraken
  • Cybercriminals

HelloKitty Successor Kraken Ransomware Hits Windows/ESXi, Benchmarks Victim Performance Before Encryption

Do Son November 17, 2025 0

Cisco Talos reports Kraken, a HelloKitty successor, is a cross-platform RaaS targeting Windows/ESXi. The malware uniquely benchmarks CPU/IO to optimize encryption speed and uses Cloudflared/SSHFS for persistence.

Critical IBM AIX RCE (CVE-2025-36250, CVSS 10.0) Flaw Exposes NIM Private Keys and Risks Directory Traversal IBM AIX RCE, NIM Private Key Leak
  • Vulnerability Report

Critical IBM AIX RCE (CVE-2025-36250, CVSS 10.0) Flaw Exposes NIM Private Keys and Risks Directory Traversal

Do Son November 17, 2025 0

IBM patched four critical flaws in AIX/VIOS. The RCE (CVSS 10.0) in nimesis and CVE-2025-36096 allow remote attackers to execute commands and obtain NIM private keys. Update immediately.

North Korea’s Contagious Interview APT Uses JSON Keeper and GitLab to Deliver BeaverTail Spyware North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Cyber Security
  • Malware

North Korea’s Contagious Interview APT Uses JSON Keeper and GitLab to Deliver BeaverTail Spyware

Do Son November 17, 2025 0

NVISO exposed the Contagious Interview APT using JSON Keeper and npoint.io as covert C2 channels. The North Korean group uses fake job lures on GitLab to deploy BeaverTail to steal Web3 credentials.

Record Supply Chain Attack: 150,000+ Malicious npm Packages Flooded Registry for Token Farming Rewards npm Token Farming, Supply Chain Flooding
  • Malware

Record Supply Chain Attack: 150,000+ Malicious npm Packages Flooded Registry for Token Farming Rewards

Do Son November 17, 2025 0

AWS Inspector exposed the largest npm supply chain incident ever: 150,000+ malicious packages were uploaded in a coordinated campaign to exploit tea.xyz token rewards via tea.yaml files.

CISA Warns: Critical Lynx+ Gateway Flaw (CVSS 10.0) Allows Unauthenticated Remote Reset; Vendor Non-Responsive shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CISA Warns: Critical Lynx+ Gateway Flaw (CVSS 10.0) Allows Unauthenticated Remote Reset; Vendor Non-Responsive

Do Son November 17, 2025 0

CISA warned of four flaws in Lynx+ Gateway. The Critical (CVSS 10.0) Auth Bypass allows unauthenticated remote reset and cleartext credential theft. Vendor GIC has not responded to CISA.

Lumma Stealer Resurfaces After Doxxing with New Browser Fingerprinting to Target High-Value Victims Lumma Browser Fingerprinting, Infostealer Resurgence
  • Malware

Lumma Stealer Resurfaces After Doxxing with New Browser Fingerprinting to Target High-Value Victims

Do Son November 17, 2025 0

Despite a recent doxxing attempt, Lumma Stealer has resurfaced, integrating browser fingerprinting into its C&C to collect WebGL/Canvas signatures for sandbox evasion and victim assessment.

Phishing-as-a-Service Uncovered: Automated Kit Impersonates Aruba S.p.A. to Steal Credentials and Credit Cards Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cybercriminals

Phishing-as-a-Service Uncovered: Automated Kit Impersonates Aruba S.p.A. to Steal Credentials and Credit Cards

Do Son November 17, 2025 0

Group-IB exposed an automated PhaaS kit that impersonates Aruba S.p.A. to steal credentials, credit card details, and OTPs. The multi-stage scam uses a CAPTCHA filter and Telegram for real-time exfiltration.
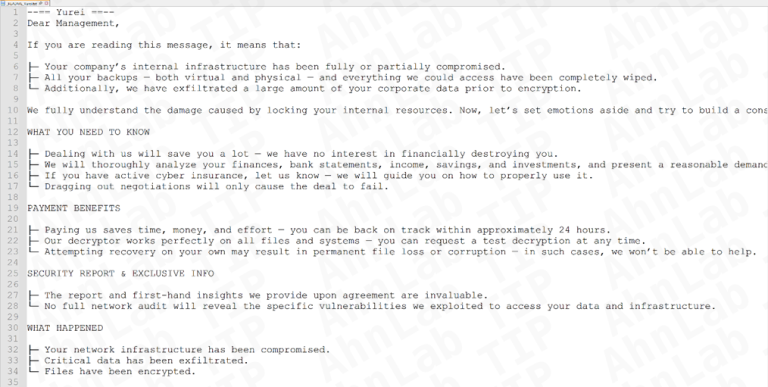
New Yurei Ransomware Emerges: Go-Based Threat Uses ChaCha20-Poly1305 for Irreversible Double Extortion Yurei Ransomware, GoLang ChaCha20
  • Malware

New Yurei Ransomware Emerges: Go-Based Threat Uses ChaCha20-Poly1305 for Irreversible Double Extortion

Do Son November 17, 2025 0

ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.

The Em Dash is Gone: Sam Altman Confirms ChatGPT Finally Dumps Its Most Annoying Habit OpenAI desktop Super App GPT-4o retirement date AI Model Collapse ChatGPT Personalization Characteristics, OpenAI Tone Sliders 2025 ChatGPT Ads OpenAI Losses AI browser, ChatGPT Atlas ChatGPT Em Dash AI Writing Quirks
  • Technology

The Em Dash is Gone: Sam Altman Confirms ChatGPT Finally Dumps Its Most Annoying Habit

Do Son November 16, 2025 0

Sam Altman confirmed ChatGPT has fixed its overuse of the em dash. The model will now respect Custom Instructions to stop using the punctuation, removing a clear AI tell.

X (Twitter) Launches ‘Chat’ to Replace DMs, Adding E2E Encryption and Video Calling EU GDPR Grok investigation xAI crypto trader recruitment X open-source algorithm 2026, Elon Musk ad transparency X Chat Replacement X End-to-End Encryption xAI, open-source xAI Elon Musk xAI Infrastructure, Saudi AI
  • Technology

X (Twitter) Launches ‘Chat’ to Replace DMs, Adding E2E Encryption and Video Calling

Do Son November 16, 2025 0

X (Twitter) launched 'Chat' to replace DMs, adding video/voice calling, file sharing, editing, and E2E encryption for messages on iOS and web. Android is coming soon.

Google to Invest $40 Billion in Texas for Next-Gen Cloud and AI Data Centers Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Google to Invest $40 Billion in Texas for Next-Gen Cloud and AI Data Centers

Do Son November 16, 2025 0

Google announced a $40B investment in Texas by 2027 to build new cloud and AI data centers. The plan includes a $30M Energy Impact Fund and workforce training.

Barrier Removed: Microsoft Makes Xbox Game Publishing Guide Public for All Developers Xbox Publishing Guide Indie Dev Barriers Xbox profit margin, Microsoft layoffs Gaming Copilot
  • Technology

Barrier Removed: Microsoft Makes Xbox Game Publishing Guide Public for All Developers

Do Son November 15, 2025 0

Microsoft publicly released the Xbox Game Publishing Guide, previously partner-only, to remove barriers and make it easier for all developers to launch titles on Xbox and PC.

WhatsApp Interoperability Live: Meta Confirms DMA Integration with BirdyChat and Haiket WhatsApp antitrust API probe India SIM-Binding Mandate Messaging App KYC WhatsApp DMA Interoperability BirdyChat Haiket Denmark Social Media Ban CVE-2025-55177 WhatsApp vulnerability, zero-click flaw npm Malware, System Wipe WhatsApp Windows App, WebView2 Downgrade WhatsApp Ban, US House NSO WhatsApp, Pegasus Spyware WhatsApp iPad iPadOS app
  • Technology

WhatsApp Interoperability Live: Meta Confirms DMA Integration with BirdyChat and Haiket

Do Son November 15, 2025 0

Meta confirmed WhatsApp is ready for DMA interoperability with third-party apps BirdyChat and Haiket. European users can soon opt in to cross-platform chats.

Project Kuiper is Now Amazon Leo: Amazon Rebrands Satellite Initiative for Commercial Launch Amazon Leo Project Kuiper Rebrand
  • Technology

Project Kuiper is Now Amazon Leo: Amazon Rebrands Satellite Initiative for Commercial Launch

Do Son November 15, 2025 0

Amazon officially rebranded its LEO satellite initiative, formerly Project Kuiper, as Amazon Leo, signaling its readiness to transition the network into a commercial product.

What Is An SPF Checker? Benefits Of SPF Validation For Your Domain domain
  • Technique

What Is An SPF Checker? Benefits Of SPF Validation For Your Domain

Do Son November 15, 2025 0
Sender Policy Framework (SPF) is a vital component of modern email authentication protocols, designed to combat email...
Read More Read more about What Is An SPF Checker? Benefits Of SPF Validation For Your Domain
Symfony Patches PATH_INFO Parsing Flaw Leading to Authorization Bypass (CVE-2025-64500) Symfony Path Info Flaw, Authorization Bypass
  • Vulnerability Report

Symfony Patches PATH_INFO Parsing Flaw Leading to Authorization Bypass (CVE-2025-64500)

Do Son November 15, 2025 0

Symfony patched a High-severity flaw (CVE-2025-64500) in its Request component. Improper PATH_INFO parsing allows attackers to bypass access control rules in vulnerable applications.

Cisco Warns of High-Severity Privilege Escalation Flaw (CVE-2025-20341) in Catalyst Center Virtual Appliance Cisco Catalyst EoP, CVE-2025-20341
  • Vulnerability Report

Cisco Warns of High-Severity Privilege Escalation Flaw (CVE-2025-20341) in Catalyst Center Virtual Appliance

Do Son November 15, 2025 0

Cisco patched a High-severity EoP flaw (CVE-2025-20341) in Catalyst Center Virtual Appliance. A low-privileged Observer user can remotely elevate privileges to Administrator via a crafted HTTP request.

App Store Cuts Commission to 15% for Mini Apps to Expand Services Vibe Coding apps Vibe Coding App Store surge Vibe Coding App Store Apple 50th Anniversary hardware Brazil CADE Apple settlement, iOS third-party app stores Brazil Tim Cook Succession Apple CEO Rumors App Store Mini Apps 15% Commission Fee iOS Japan Sideloading, Third-Party App Stores Web App Store, App Discovery Apple Age Verification, Texas SB2420 Apple AI acquisitions App Store, Antitrust Apple WebKit, Japan Regulations App Store Age Ratings, Parental Controls Apple App Store, Epic Games Lawsuit
  • Technology

App Store Cuts Commission to 15% for Mini Apps to Expand Services

Do Son November 14, 2025 0

Apple launched the Mini Apps Partner Program, cutting the App Store commission fee in half—from 30% to 15%—for eligible developers of self-contained web-based services.
5 KPIs to Measure When You Introduce AI SOC Agents CVE-2025-20059
  • Technique

5 KPIs to Measure When You Introduce AI SOC Agents

Do Son November 14, 2025 0
“Is it working?” It can be easy to drop an AI SOC agent into your environment and...
Read More Read more about 5 KPIs to Measure When You Introduce AI SOC Agents
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.