Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
MongoDB Driver Vulnerabilities Fixed Across Ecosystem Diagram illustrating critical MongoDB driver vulnerabilities and patched MongoDB driver vulnerabilities
  • Vulnerability Report

MongoDB Driver Vulnerabilities Fixed Across Ecosystem

Do Son September 25, 2026 0

MongoDB patched critical MongoDB driver vulnerabilities across its ecosystem. Update your drivers to resolve these MongoDB driver vulnerabilities now.
Construction With NetSuite: Connecting Job Costs to Financial Decisions Construction With NetSuite
  • Technique

Construction With NetSuite: Connecting Job Costs to Financial Decisions

Do Son September 25, 2026 0

Construction with NetSuite can connect job costs, project budgets, billing, and financial reporting. Learn what contractors should plan before bringing work into one system.
High-Severity Apache Qpid Broker-J Vulnerabilities Fixed Diagram showing Apache Qpid Broker-J vulnerabilities and attack mechanisms
  • Vulnerability Report

High-Severity Apache Qpid Broker-J Vulnerabilities Fixed

Do Son September 25, 2026 0

New Apache Qpid Broker-J vulnerabilities, including CVE-2026-92609, CVE-2026-92573, and CVE-2026-92564, expose brokers to DoS. Patch immediately.
Norwegian Cruise Line Vulnerability Permits Keycard Replay card-80442
  • Vulnerability Report

Norwegian Cruise Line Vulnerability Permits Keycard Replay

Do Son September 25, 2026 0

A critical Norwegian Cruise Line vulnerability allows attackers to clone RFID keycards. Mitigate CVE-2026-75907 to protect vessel and guest security.
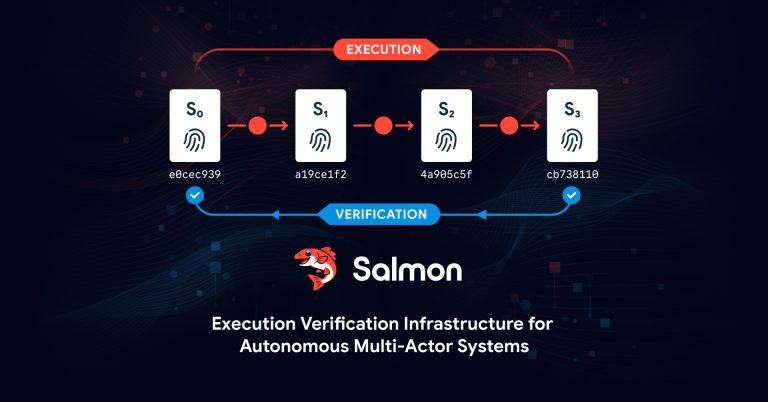
Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems image_26_1790250272WOIo9JWZto
  • Press Release

Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems

cybernewswire September 25, 2026 0
San Francisco, USA, 25th September 2026, CyberNewswire
Read More Read more about Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents and Autonomous Systems
Google Project Suncatcher: Pioneering Orbital AI Data Centers Google Project Suncatcher orbital AI data center satellite
  • Technology

Google Project Suncatcher: Pioneering Orbital AI Data Centers

Do Son September 25, 2026 0

Explore Google Project Suncatcher, a visionary moonshot to launch AI data centers into space. Discover how orbital TPUs aim to solve AI energy crises.
High-Severity PHP Vulnerabilities Patched Across Multiple Branches Diagram illustrating critical PHP vulnerabilities and patched PHP vulnerabilities
  • Vulnerability Report

High-Severity PHP Vulnerabilities Patched Across Multiple Branches

Do Son September 25, 2026 0

The PHP project patched critical PHP vulnerabilities across multiple branches. Update now to resolve these PHP vulnerabilities and secure your web servers.
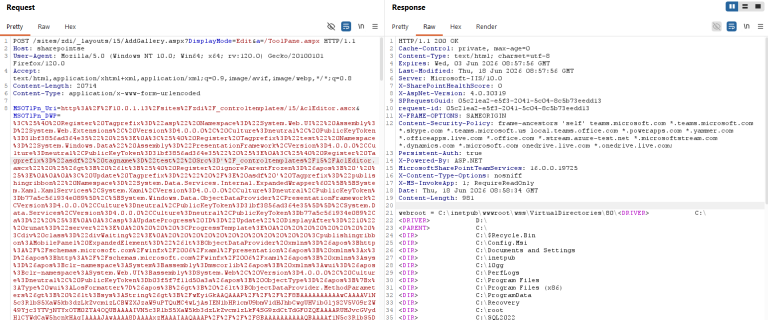
Exploited SharePoint RCE Vulnerability Details Disclosed Diagram illustrating the exploited SharePoint RCE vulnerability attack flow
  • Vulnerability Report

Exploited SharePoint RCE Vulnerability Details Disclosed

Do Son September 25, 2026 0

An exploited SharePoint RCE vulnerability is under attack. Technical details for this SharePoint RCE vulnerability are public. Patch CVE-2026-65660 now.
Malicious Terraform Providers Spread Graphalgo Go Malware Diagram to detect malicious Terraform providers and stop malicious Terraform providers in CI/CD
  • Malware

Malicious Terraform Providers Spread Graphalgo Go Malware

Do Son September 25, 2026 0

Learn how to detect malicious Terraform providers. New malicious Terraform providers spread Graphalgo Go malware through typosquatted packages.
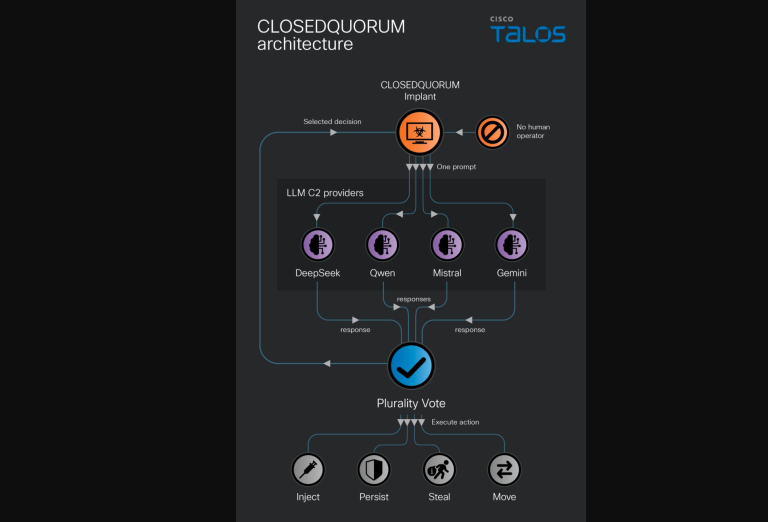
CLOSEDQUORUM AI Malware Uses LLMs for Autonomous C2 Diagram of the autonomous CLOSEDQUORUM AI malware architecture showing how CLOSEDQUORUM AI malware queries language models
  • Malware

CLOSEDQUORUM AI Malware Uses LLMs for Autonomous C2

Do Son September 25, 2026 0

Cisco Talos discovered autonomous CLOSEDQUORUM AI malware. The CLOSEDQUORUM AI malware uses multiple LLMs to guide cyberattacks independently.
WordPress Must-Use Plugin Malware Uses EtherHiding Analysis of stealthy WordPress must-use plugin malware and WordPress must-use plugin malware architecture
  • Malware

WordPress Must-Use Plugin Malware Uses EtherHiding

Do Son September 25, 2026 0

Wordfence uncovered stealthy WordPress must-use plugin malware. Learn how this WordPress must-use plugin malware abuses EtherHiding to steal secrets.
Critical ServiceNow Vulnerabilities Fixed in AI Platform Diagram showing critical ServiceNow vulnerabilities and attack paths in the AI Platform
  • Vulnerability Report

Critical ServiceNow Vulnerabilities Fixed in AI Platform

Do Son September 25, 2026 0

ServiceNow has patched five critical ServiceNow vulnerabilities, including an unauthenticated SQL injection flaw. Update your instances to stay secure.
Critical Eufy Robot Vacuum Vulnerabilities Allow System Takeover Diagram illustrating Eufy robot vacuum vulnerabilities and OS command injection paths
  • Vulnerability Report

Critical Eufy Robot Vacuum Vulnerabilities Allow System Takeover

Do Son September 25, 2026 0

Critical Eufy robot vacuum vulnerabilities expose the Omni C20 and X10 Pro to OS command injection. Patch CVE-2026-93289 and CVE-2026-93291 immediately.
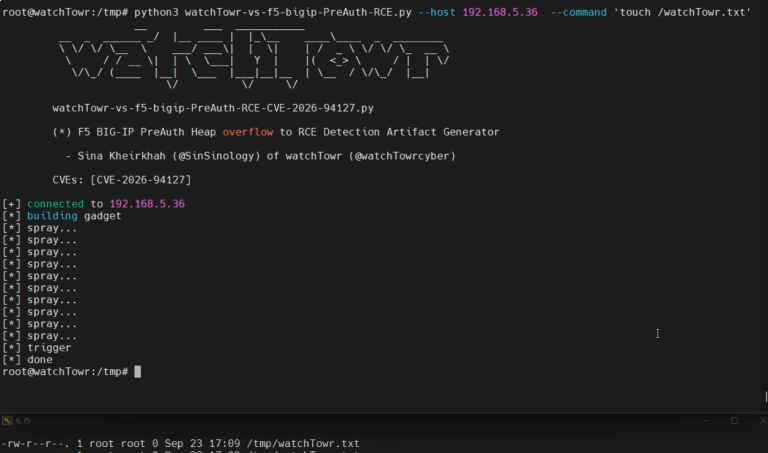
Exploited F5 BIG-IP RCE Vulnerability Details and PoC Disclosed Diagram showing the exploited F5 BIG-IP RCE vulnerability attack chain
  • Vulnerability Report

Exploited F5 BIG-IP RCE Vulnerability Details and PoC Disclosed

Do Son September 25, 2026 0

An exploited F5 BIG-IP RCE vulnerability (CVE-2026-94127) is under active attack. Discover how the PoC works and patch your APM proxies immediately.
CVE-2026-96512: Sudo Security Vulnerability Allows Privilege Escalation Diagram explaining the Sudo security vulnerability and CVE-2026-96512 mitigation
  • Vulnerability Report

CVE-2026-96512: Sudo Security Vulnerability Allows Privilege Escalation

Do Son September 25, 2026 0

A new Sudo security vulnerability (CVE-2026-96512) allows local users to bypass time-based restrictions. Learn how to mitigate this high-risk Linux flaw.
CISA Adds WSO2 and Adobe Flaws to KEV Catalog Diagram illustrating exploited CISA KEV vulnerabilities affecting WSO2 and Adobe
  • Vulnerability Report

CISA Adds WSO2 and Adobe Flaws to KEV Catalog

Do Son September 25, 2026 0

CISA added two exploited CISA KEV vulnerabilities to its catalog. Patch WSO2 and Adobe Commerce to secure systems against active attacks.
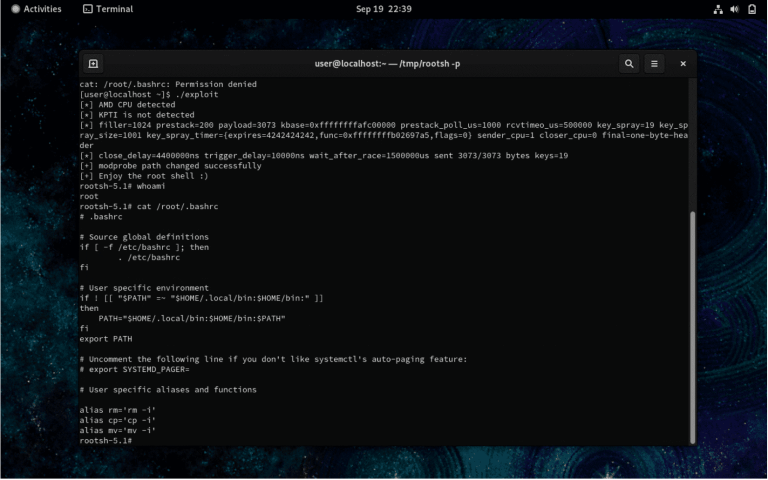
RustyTux: Public PoC Exploit Targets Linux Kernel Privilege Escalation Flaw RustyTux Linux kernel privilege escalation exploit chaining an ESP-in-TCP use-after-free race to a root shell on CentOS and Ubuntu
  • Vulnerability Report

RustyTux: Public PoC Exploit Targets Linux Kernel Privilege Escalation Flaw

Do Son September 25, 2026 0

RustyTux is a public PoC for a Linux kernel privilege escalation via an ESP-in-TCP use-after-free (CVE-2026-23239). Details and exploit code are now public.
SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta SCOUTz_-_Header_Banner_1200x720_1790189561nFevdYxfGB
  • Press Release

SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta

cybernewswire September 24, 2026 0
Phoenix, Arizona, 24th September 2026, CyberNewswire
Read More Read more about SCOUTz Prospect Intelligence Platform Launches for MSPs with 30-Day Beta
Microsoft Explores Intrusive In-Game Advertising Microsoft game ad patent concept showing a paused game screen for promotional content
  • Technology

Microsoft Explores Intrusive In-Game Advertising

Do Son September 24, 2026 0

Discover the new Microsoft game ad patent. Learn how this system intelligently pauses gameplay to show advertisements and rewards players with free credits.
Meta Muse Secretly Used Humans for AI Phone Calls Meta Muse AI agent phone calling feature secretly handed off to human contractors
  • Data Leak

Meta Muse Secretly Used Humans for AI Phone Calls

Do Son September 24, 2026 0

Meta Muse human concierge secretly routed AI phone calls to contractors, exposing users' private data. Meta paused the feature after a racist remark.

ShinyHunters Syndicate Alleges Major FBI Network Compromise Bling Libra
  • Data Leak

ShinyHunters Syndicate Alleges Major FBI Network Compromise

Do Son September 24, 2026 0

Discover how the ShinyHunters hacking group claims to have orchestrated a massive FBI data breach, stealing employee records via an Oracle zero-day flaw.
Windows 11 Update Breaks Always On VPN Connections Windows 11 Always On VPN connection stuck after the September 2026 update with a port in use error
  • Windows

Windows 11 Update Breaks Always On VPN Connections

Do Son September 24, 2026 0

Windows 11 Always On VPN fails to connect after the September 2026 update. Switch to a fixed IKEv2 or SSTP protocol until Microsoft ships a permanent fix.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-86413CVSS 9.1
    When using an *ambient user* in a first transfer doing Negotiate authentication and asked to follow redirects, curl...
    📅 Updated: Oct 30, 2026
  • CVE-2026-86414CVSS 9.1
    An HTTP proxy can trick libcurl into sending the origin's credentials (Basic password, or a Negotiate/Kerberos ticket) to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-87861CVSS 9.1
    When using ambient user credentials, an HTTP request directed to one origin may be dispatched over a connection...
    📅 Updated: Oct 30, 2026
  • CVE-2026-119568CVSS 9.1
    vsftpd through 3.0.5 contains an authentication bypass vulnerability in ssl_data_accept() that allows unauthenticated attackers to hijack FTPS data...
    📅 Updated: Oct 30, 2026
  • CVE-2026-119418CVSS 9.2
    CakePHP through 5.4.3 contains an sql injection vulnerability that allows attackers to inject SQL by supplying unvalidated frame...
    📅 Updated: Oct 30, 2026
  • CVE-2026-119419CVSS 9.2
    CakePHP through 5.4.3 contains an sql injection vulnerability that allows attackers to inject SQL by supplying unvalidated collation...
    📅 Updated: Oct 30, 2026
  • CVE-2025-31704CVSS 9.8
    A vulnerability has been found in the Dahua Intelligent Connection Center. A remote attacker could send a specially...
    📅 Updated: Oct 30, 2026
  • CVE-2026-116366CVSS 9.5
    An issue has been discovered in ClickHouse Server that, under certain conditions, could allow an unauthenticated user with...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.