PoC Published for Hugging Face Datasets RCE CVE-2026-57845 (CVSS 8.8) in Library With 38 Million Monthly Downloads
 Do Son
TL;DR
Researcher Sai Teja Erukude has published full details and a working proof-of-concept for CVE-2026-57845. This Hugging Face datasets RCE flaw carries a CVSS score of 8.8. The bug affects every datasets release up to and including 5.1.0, the latest version on PyPI. PyPI Stats counts about 38.4 million downloads of the library in the past 30 days.
The deprecated but still registered pandas builder passes user-supplied files straight to pickle deserialization. A crafted pickle file can therefore run Python code the moment a victim loads it. No fixed release exists yet, so avoid the pandas builder for untrusted data.
- CVE: CVE-2026-57845
- CVSS: 8.8 (High · CVSSv3)
- Product: huggingface datasets
- Affected: ≤ 5.1.0
- Impact: Hugging Face Datasets through 5.1.0 Pickle Deserialization RCE via Pandas Builder
- Status: No confirmed exploitation yet
- EPSS: 0.5% (30-day)
- Action: See vendor advisory
Why It Matters
The datasets library feeds data into machine learning, analysis and automation pipelines. Those systems often hold cloud keys, tokens and model secrets. According to the advisory, a successful attack may allow “reading files, environment variables, and application secrets accessible to the process.”
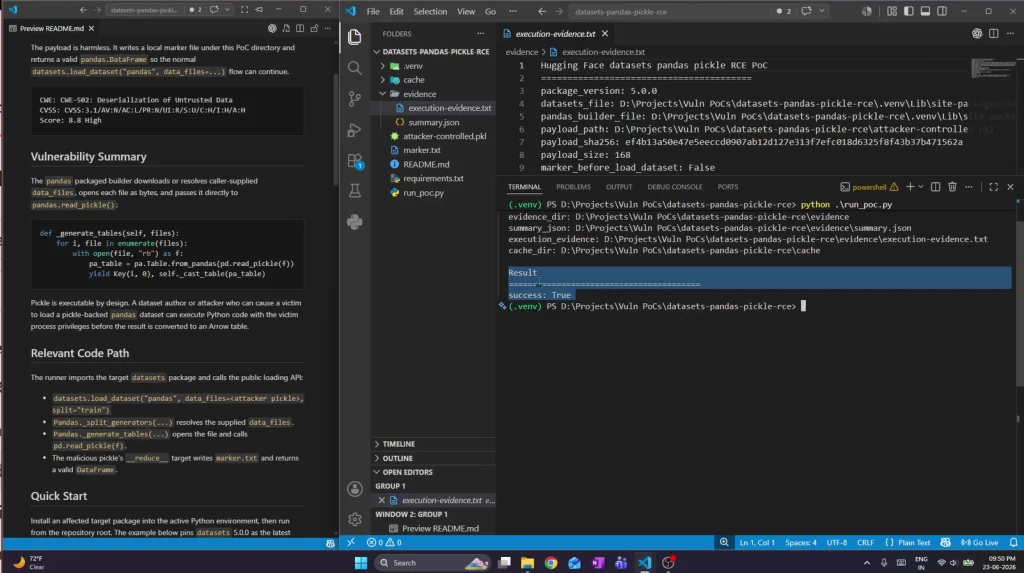
The public repository now includes the exploit script, saved evidence and a demo video. So far, however, no attacks in the wild have been reported. Download counts are an estimate of reach, since they include automated CI and mirror traffic.
How the Attack Works
A caller can still request the “pandas” builder through load_dataset(). The builder opens each data file and hands it to pandas.read_pickle(). As the researcher explains, “Python pickle deserialization can execute attacker-selected code.”
The attacker’s code runs “before Arrow conversion or feature validation.” In the PoC, loading even “completes normally and returns one row,” so the victim sees nothing unusual. The attack needs user interaction, since the victim must load the malicious dataset. Typical lures include untrusted projects, repositories, downloads or shared files.
The researcher also warns that common fixes fall short. “Deprecating the builder or validating the returned DataFrame does not prevent execution during unpickling.”
Affected Versions
- Hugging Face datasets 5.1.0 and all earlier versions
- Component: datasets.packaged_modules.pandas.pandas
VulnCheck assigned the CVE and coordinated disclosure. It also rates the flaw 8.7 under CVSS 4.0. VulnCheck published the CVE on October 23, 2026, more than two weeks after datasets 5.1.0 reached PyPI on October 5.
Patch and Mitigation
A proposed fix is open as Hugging Face datasets pull request #8879. It makes the pandas builder raise an error before it opens any file. Until a release ships it, take these steps:
- Never load pickle-backed datasets from untrusted sources through the pandas builder.
- Use the Parquet, Arrow, CSV or JSON builders instead.
- For an existing DataFrame, use Dataset.from_pandas() rather than a pickle file.
- Run dataset loading for untrusted inputs in isolated, low-privilege environments.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
