
 Do Son
A critical flaw (CVE-2025-24288, CVSS 9.8) in Versa Director exposes hardcoded default credentials for high-privilege accounts with sudo access. PoC released. Update now

Cisco ClamAV versions 1.4.3 and 1.0.9 fix critical flaws: CVE-2025-20260 (CVSS 9.8) in PDF scanning could allow RCE, and CVE-2025-20234 (UDF) leads to DoS.

A critical flaw (CVE-2025-5071) in WordPress's AI Engine plugin allows subscribers to escalate privileges and take over websites with Dev Tools/MCP enabled.
Cisco warns of a critical flaw (CVE-2025-20271, CVSS 8.6) in Meraki MX/Z Series devices, allowing unauthenticated remote DoS on AnyConnect VPN. Update firmware now!

Two critical flaws in Apache Traffic Server (CVE-2025-31698, CVE-2025-49763) allow IP-based ACL bypass and remote DoS via ESI plugin.

A high-severity flaw (CVE-2025-6020) in Linux PAM's pam_namespace allows unprivileged users to gain root via symlink attacks and race conditions.

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.

A critical SSRF flaw (CVE-2025-6087) in @opennextjs/cloudflare allows unauthenticated users to proxy arbitrary remote content via /_next/image endpoint.
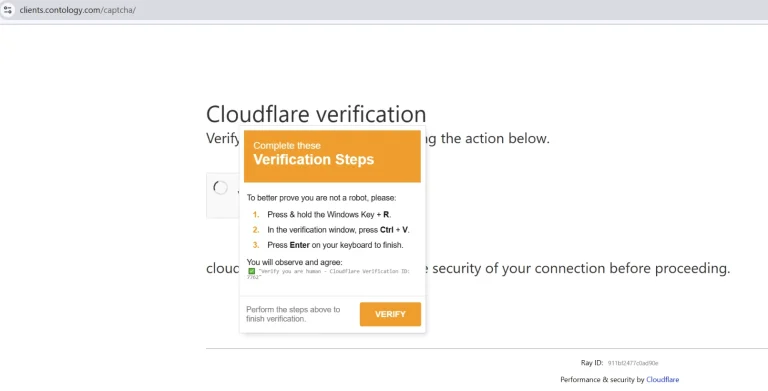
Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

A critical flaw (CVE-2025-51381) in KAON KCM3100 Wi-Fi gateways allows local attackers to bypass authentication. Update firmware to version 1.4.8 immediately.

A new wave of invoice-themed phishing emails is distributing the Sorillus RAT across Europe, leveraging legitimate platforms like OneDrive and Ngrok for stealthy delivery.

XDSpy, a covert cyber-espionage group, is back with a sophisticated campaign targeting governments, leveraging an obscure Windows LNK file parsing flaw and new XDigo malware

 cybernewswire

The Trump administration has granted TikTok another 90-day extension, allowing more time for a sale to a US buyer and keeping the app from being banned

A high-severity flaw (CVE-2025-4565) in Google's pure-Python Protobuf backend allows unauthenticated attackers to crash applications via crafted nested messages.

Two critical buffer overflow flaws in D-Link router allow remote code execution. PoC available, no patch will be issued.

Broadcom launches VMware Cloud Foundation 9.0, a unified platform for secure, managed private cloud, accelerating AI infrastructure and supporting modern workloads across environments.

The Wi-Fi Alliance is developing Wi-Fi 8 (802.11bn) for a 2028 release, focusing on ultra-reliable performance, throughput efficiency, and coordinated multi-AP operation.

A Reddit user lost 30 years of data after their OneDrive account was suspended, underscoring the critical need for multiple backup solutions beyond single cloud reliance.

Mastodon updates its Terms of Service, formally prohibiting unauthorized AI data scraping and LLM training, effective July 1, 2025. Other Fediverse instances may follow.