Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Firefox Pilots AI Search: Perplexity AI Integration Challenges Google’s Dominance Firefox AI Search, Perplexity AI
  • Technology

Firefox Pilots AI Search: Perplexity AI Integration Challenges Google’s Dominance

Do Son June 18, 2025 0

Mozilla is piloting an AI-powered search engine in Firefox, partnering with Perplexity AI. This experimental integration could challenge Google's search dominance.

The “Infinite Workday” is Here: Microsoft Warns of Never-Ending Work Driven by Hybrid Models & AI HTTP.sys RCE vulnerability, Windows HTTP stack exploit, CVE-2026-47291 Netlogon RCE vulnerability Exploited in the wild Secure Boot certificate renewal 2026, Windows 11 UEFI update Community-First AI Infrastructure, Microsoft self-funding energy mandate aka.ms/aoh online portal CVE-2025-55681, Windows DWM Elevation Windows Administrator Protection, CVE-2025-60718 Microsoft AI Compute, IREN Infrastructure Microsoft Japan PPA, Renewable Energy Microsoft AI Investment, Cloud Expansion Microsoft Azure, Startup Credits Infinite Workday, AI in Work Microsoft Russia, Bankruptcy AI code generation, Microsoft AI Microsoft Layoffs, Restructuring
  • Technology

The “Infinite Workday” is Here: Microsoft Warns of Never-Ending Work Driven by Hybrid Models & AI

Do Son June 18, 2025 0

Microsoft's latest Work Trend Index warns of the "infinite workday," where work increasingly spills into personal time, driven by hybrid models and AI integration.
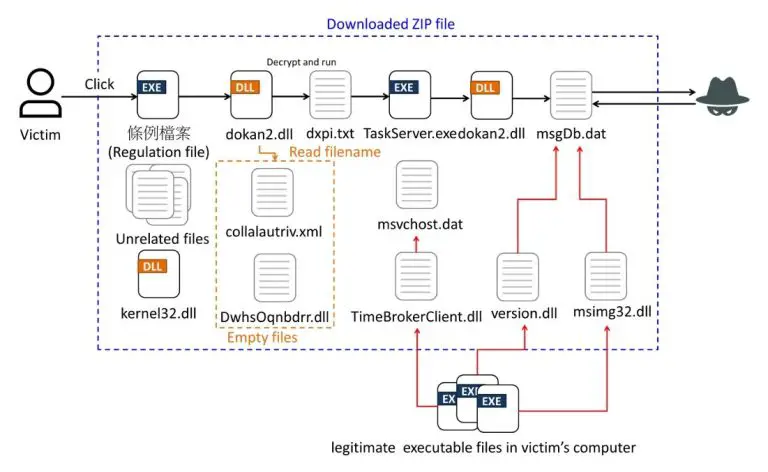
Taiwan Under Attack: Sophisticated Phishing Campaign Delivers Winos 4.0, HoldingHands RAT, & Gh0stCringe Taiwan Cyberattack, Phishing Campaign
  • Malware

Taiwan Under Attack: Sophisticated Phishing Campaign Delivers Winos 4.0, HoldingHands RAT, & Gh0stCringe

Do Son June 18, 2025 0

A sophisticated malware campaign is targeting Taiwan, impersonating the National Taxation Bureau to distribute Winos 4.0, HoldingHands RAT, and Gh0stCringe.

Urgent Ubiquiti Alert: Critical Flaws (CVSS 9.9) Allow Privilege Escalation via XSS & SQL Injection Ubiquiti Vulnerabilities, Privilege Escalation
  • Vulnerability

Urgent Ubiquiti Alert: Critical Flaws (CVSS 9.9) Allow Privilege Escalation via XSS & SQL Injection

Do Son June 18, 2025 0

Two high-severity Ubiquiti flaws allow privilege escalation via XSS in UCRM and authenticated SQL injection in UISP. Update immediately!

Critical Linux Root Exploit Chain Discovered in PAM & UDisks, Affecting Major Distros Linux Root Privilege Escalation
  • Linux
  • Vulnerability Report

Critical Linux Root Exploit Chain Discovered in PAM & UDisks, Affecting Major Distros

Do Son June 18, 2025 0

Qualys uncovered two critical Linux flaws (CVE-2025-6018, CVE-2025-6019) allowing local root privilege escalation via PAM and UDisks. Patching is urgent for major distros.

KimJongRAT Returns: New PE & PowerShell Variants Steal Crypto and Browser Data via CDNs KimJong
  • Malware

KimJongRAT Returns: New PE & PowerShell Variants Steal Crypto and Browser Data via CDNs

Do Son June 18, 2025 0

KimJongRAT is back with new PE and PowerShell variants, using LNK files and CDNs to steal browser, email, and over 30 crypto wallet details from victims.

Why Threat Intelligence Is Critical for Business Security and Avoiding Cyberattacks Threat Intelligence
  • Technique

Why Threat Intelligence Is Critical for Business Security and Avoiding Cyberattacks

Do Son June 18, 2025 0

Understand the importance of threat intelligence for businesses. Stay ahead of cyber threats and reduce breach costs effectively.

Linux Kernel Flaw (CVE-2023-0386) Actively Exploited for Root Privilege Escalation, PoC Available CVE-2023-0386 PoC Linux Privilege Escalation, OverlayFS
  • Vulnerability Report

Linux Kernel Flaw (CVE-2023-0386) Actively Exploited for Root Privilege Escalation, PoC Available

Do Son June 18, 2025 0

CISA has added CVE-2023-0386, a critical Linux kernel OverlayFS flaw, to its KEV Catalog, confirming active exploitation allowing local users to gain root privileges.

Critical NetScaler Flaws Allow Access Control Bypass & Memory Overread NetScaler Vulnerability CVE-2026-3055 Citrix VDA, Privilege Escalation NetScaler Vulnerabilities, Access Bypass CVE-2024-8534 and CVE-2024-8535
  • Vulnerability Report

Critical NetScaler Flaws Allow Access Control Bypass & Memory Overread

Do Son June 18, 2025 0

Cloud Software Group issues urgent patches for two critical NetScaler flaws allowing access bypass and memory overread. Update immediately.

Urgent Veeam Update: Critical RCE CVE-2025-23121 (CVSS 9.9) & Two Other Flaws Threaten Backup Servers Veeam Backup vulnerability remote code execution Veeam Backup vulnerability Veeam Vulnerabilities CVE-2024-42448 & CVE-2024-42449
  • Vulnerability Report

Urgent Veeam Update: Critical RCE CVE-2025-23121 (CVSS 9.9) & Two Other Flaws Threaten Backup Servers

Do Son June 18, 2025 0

Veeam released a critical update for Backup & Replication, patching three flaws, including a CVSS 9.9 RCE (CVE-2025-23121) allowing authenticated users to execute code.

Chrome Update Alert: Two High-Severity Flaws (CVE-2025-6191, CVE-2025-6192) Patched Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Vulnerability Report

Chrome Update Alert: Two High-Severity Flaws (CVE-2025-6191, CVE-2025-6192) Patched

Do Son June 18, 2025 0

Google Chrome 137.0.7151.119/.120 is rolling out with crucial security fixes, addressing two high-severity flaws: an integer overflow in V8 and a use-after-free in Profiler.

WAGO Device Manager Vulnerabilities Expose Critical Industrial Infrastructure to Remote Exploits WAGO Vulnerability
  • Vulnerability Report

WAGO Device Manager Vulnerabilities Expose Critical Industrial Infrastructure to Remote Exploits

Do Son June 18, 2025 0

WAGO Device Manager security updates address two vulnerabilities allowing unauthenticated remote access to sensitive system files.

Kimsuky APT Group Abuses HWP and AnyDesk for Covert Remote Surveillance kimsumy
  • Cyber Security

Kimsuky APT Group Abuses HWP and AnyDesk for Covert Remote Surveillance

Do Son June 18, 2025 0

Kimsuky APT is using HWP documents and stealthy AnyDesk backdoors in a new phishing campaign to infiltrate systems under the guise of academic collaboration.
Trend Micro Fortifies AI Security: Integrates NVIDIA Agentic AI Safety for End-to-End Protection Trend Micro Apex One CVE-2025-71210 AI Security Trend Micro Deep Security - CVE-2024-48904 & CVE-2024-51503
  • Technology

Trend Micro Fortifies AI Security: Integrates NVIDIA Agentic AI Safety for End-to-End Protection

Do Son June 17, 2025 0

Trend Micro integrates NVIDIA's Agentic AI Safety into its Secure AI Factory, offering end-to-end security for AI systems from development to runtime, protecting against data leakage and model poisoning.

OpenAI Secures $200M DoD Contract to Develop Advanced AI for National Security ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

OpenAI Secures $200M DoD Contract to Develop Advanced AI for National Security

Do Son June 17, 2025 0

OpenAI signed a $200M contract with the U.S. DoD to develop advanced AI prototypes for military healthcare, procurement, and cybersecurity needs.

Windows Hello Update: Microsoft Disables Facial Recognition in the Dark Due to Security Flaw Windows Hello vulnerabilities Windows Hello, Facial Recognition
  • Vulnerability Report
  • Windows

Windows Hello Update: Microsoft Disables Facial Recognition in the Dark Due to Security Flaw

Do Son June 17, 2025 0

Microsoft disabled Windows Hello facial recognition in dark environments on Windows 10/11 due to a security flaw that could allow local spoofing attacks.

High-Severity Flaw Exposes ASUS Armoury Crate to Authentication Bypass ASUS CVE-2025-13348 File Shredder Removal ASUS LPE Flaw CVE-2025-59373 ASUS Armoury Crate vulnerability Asus CVE Numbering Authority - CVE-2024-12912 and CVE-2024-13062 AMI BMC vulnerability, CVE-2024-54085
  • Vulnerability Report

High-Severity Flaw Exposes ASUS Armoury Crate to Authentication Bypass

Do Son June 17, 2025 0

ASUS warns of a high-severity flaw in Armoury Crate that allows authentication bypass and privilege escalation. Update immediately!

Team46 (TaxOff) Exploits Google Chrome Zero-Day (CVE-2025-2783) in Sophisticated Phishing Campaign Team46 APT, Google Chrome Zero-Day
  • Cyber Security
  • Vulnerability Report

Team46 (TaxOff) Exploits Google Chrome Zero-Day (CVE-2025-2783) in Sophisticated Phishing Campaign

Do Son June 17, 2025 0

Team46 (TaxOff) is exploiting a Google Chrome sandbox escape zero-day (CVE-2025-2783) to deploy the multi-layered Trinper malware via phishing campaigns

Critical Teleport Flaw (CVSS 9.8): Remote Authentication Bypass Threatens Infrastructure Access Teleport Vulnerability, Remote Authentication Bypass
  • Vulnerability

Critical Teleport Flaw (CVSS 9.8): Remote Authentication Bypass Threatens Infrastructure Access

Do Son June 17, 2025 0

Teleport disclosed a critical remote authentication bypass flaw (CVE-2025-49825) affecting self-hosted instances. Upgrade Proxies and agents immediately!

CVE-2025-49596: Critical RCE Vulnerability in MCP Inspector Exposes AI Developer Environments MCP Inspector, RCE Vulnerability
  • Vulnerability Report

CVE-2025-49596: Critical RCE Vulnerability in MCP Inspector Exposes AI Developer Environments

Do Son June 17, 2025 0

A critical flaw (CVE-2025-49596, CVSS 9.4) in MCP Inspector allows unauthenticated remote code execution, threatening AI application development environments.

Two sslh Flaws Disclosed: Remote DoS Attacks Possible via Protocol Multiplexer sslh Vulnerabilities, DoS Attack
  • Vulnerability Report

Two sslh Flaws Disclosed: Remote DoS Attacks Possible via Protocol Multiplexer

Do Son June 17, 2025 0

SUSE disclosed flaws in sslh (CVE-2025-46807, CVE-2025-46806) allowing remote DoS attacks via file descriptor exhaustion and unsafe memory access.

Unauthenticated RCE in BeyondTrust Tools: Chat Feature Opens Door to Server Takeover BeyondTrust RCE, Server-Side Template Injection
  • Vulnerability

Unauthenticated RCE in BeyondTrust Tools: Chat Feature Opens Door to Server Takeover

Do Son June 17, 2025 0

BeyondTrust warns of a high-severity unauthenticated RCE flaw in Remote Support and PRA, exploitable via the built-in chat feature. Patch immediately

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.