Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical Versa Director Flaw (CVSS 9.8): Hardcoded Credentials Grant Root Access, PoC Available Versa Director, Default Credentials
  • Vulnerability

Critical Versa Director Flaw (CVSS 9.8): Hardcoded Credentials Grant Root Access, PoC Available

Do Son June 19, 2025 0

A critical flaw (CVE-2025-24288, CVSS 9.8) in Versa Director exposes hardcoded default credentials for high-privilege accounts with sudo access. PoC released. Update now

Cisco ClamAV Critical Flaws: CVE-2025-20260 (CVSS 9.8) Allows Code Execution ClamAV Vulnerability ClamAV Vulnerabilities, RCE
  • Vulnerability Report

Cisco ClamAV Critical Flaws: CVE-2025-20260 (CVSS 9.8) Allows Code Execution

Do Son June 19, 2025 0

Cisco ClamAV versions 1.4.3 and 1.0.9 fix critical flaws: CVE-2025-20260 (CVSS 9.8) in PDF scanning could allow RCE, and CVE-2025-20234 (UDF) leads to DoS.

WordPress AI Engine Flaw (CVE-2025-5071): Critical Bug Allows Subscriber-Level Account Takeover WordPress Privilege Escalation CVE-2026-1492 Sneeit Framework RCE, Unauthenticated Code Execution Post SMTP, Account Takeover WordPress Vulnerability, Unpatched XSS WordPress Vulnerability, PHP Object Injection WordPress AI Engine, Privilege Escalation CVE-2024-43153 & CVE-2024-43234
  • Vulnerability Report

WordPress AI Engine Flaw (CVE-2025-5071): Critical Bug Allows Subscriber-Level Account Takeover

Do Son June 19, 2025 0

A critical flaw (CVE-2025-5071) in WordPress's AI Engine plugin allows subscribers to escalate privileges and take over websites with Dev Tools/MCP enabled.
CVE-2025-20271: Cisco Meraki VPN Bug Exposes MX and Z Series Devices to Remote DoS Attacks Cisco ISE Root Escalation * Read-Only Admin Exploit Cisco Secure FMC Vulnerability CVE-2026-20131 Cisco Meeting Management Vulnerability CVE-2026-20098 Cisco vulnerability, RCE flaw CVE-2025-20265 Cisco Meraki, VPN Vulnerability Cisco Nexus Dashboard - CVE-2024-20424 CVE-2025-20115 Cisco Vulnerability CVE-2018-0171 Privilege Escalation Cisco Unified Intelligence Center
  • Vulnerability Report

CVE-2025-20271: Cisco Meraki VPN Bug Exposes MX and Z Series Devices to Remote DoS Attacks

Do Son June 19, 2025 0

Cisco warns of a critical flaw (CVE-2025-20271, CVSS 8.6) in Meraki MX/Z Series devices, allowing unauthenticated remote DoS on AnyConnect VPN. Update firmware now!

Apache Traffic Server Flaws Allow Access Bypass & Remote DoS Apache Traffic Server Vulnerabilities CVE-2024-56195 and CVE-2024-56196
  • Vulnerability

Apache Traffic Server Flaws Allow Access Bypass & Remote DoS

Do Son June 19, 2025 0

Two critical flaws in Apache Traffic Server (CVE-2025-31698, CVE-2025-49763) allow IP-based ACL bypass and remote DoS via ESI plugin.

Root Access Unlocked: How a pam_namespace Flaw Lets Attackers Elevate Privileges on Linux Linux PAM, Privilege Escalation
  • Vulnerability

Root Access Unlocked: How a pam_namespace Flaw Lets Attackers Elevate Privileges on Linux

Do Son June 19, 2025 0

A high-severity flaw (CVE-2025-6020) in Linux PAM's pam_namespace allows unprivileged users to gain root via symlink attacks and race conditions.

Tor Meets Docker: Sophisticated Crypto-Mining Campaign Hijacks Misconfigured APIs Docker
  • Cybercriminals

Tor Meets Docker: Sophisticated Crypto-Mining Campaign Hijacks Misconfigured APIs

Do Son June 19, 2025 0

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.

MySQL Servers Under Attack: Threat Actors Exploiting UDFs to Inject Gh0stRAT, XWorm & Zoho Agents MySQL Attacks, UDF Exploitation pREST, SQL injection
  • Cybercriminals

MySQL Servers Under Attack: Threat Actors Exploiting UDFs to Inject Gh0stRAT, XWorm & Zoho Agents

Do Son June 19, 2025 0

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.

SSRF Flaw (CVE-2025-6087) in OpenNext for Cloudflare Allows Unauthenticated Content Proxying SSRF, Cloudflare OpenNext
  • Vulnerability Report

SSRF Flaw (CVE-2025-6087) in OpenNext for Cloudflare Allows Unauthenticated Content Proxying

Do Son June 19, 2025 0

A critical SSRF flaw (CVE-2025-6087) in @opennextjs/cloudflare allows unauthenticated users to proxy arbitrary remote content via /_next/image endpoint.
Elastic Uncovers Stealthy Campaign Using GHOSTPULSE and ARECHCLIENT2 Malware Fake captcha
  • Cybercriminals

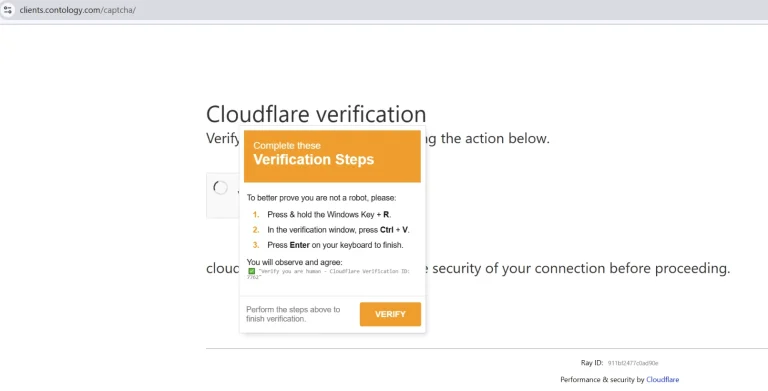
Elastic Uncovers Stealthy Campaign Using GHOSTPULSE and ARECHCLIENT2 Malware

Do Son June 19, 2025 0

Elastic uncovers a sophisticated ClickFix campaign deploying the GHOSTPULSE loader to deliver ARECHCLIENT2 malware, leveraging social engineering for credential theft and remote access.

Ransomware Gang Qilin Rises Amid Collapse of Major Gangs Like RansomHub and LockBit Qilin
  • Malware

Ransomware Gang Qilin Rises Amid Collapse of Major Gangs Like RansomHub and LockBit

Do Son June 19, 2025 0

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

Critical Auth Bypass Vulnerability (CVE-2025-51381) Found in KAON KCM3100 Gateways KAON Wi-Fi Gateway, Authentication Bypass
  • Vulnerability Report

Critical Auth Bypass Vulnerability (CVE-2025-51381) Found in KAON KCM3100 Gateways

Do Son June 19, 2025 0

A critical flaw (CVE-2025-51381) in KAON KCM3100 Wi-Fi gateways allows local attackers to bypass authentication. Update firmware to version 1.4.8 immediately.

Invoice to Infection: Sorillus RAT Campaign Strikes European Organizations invoic
  • Malware

Invoice to Infection: Sorillus RAT Campaign Strikes European Organizations

Do Son June 19, 2025 0

A new wave of invoice-themed phishing emails is distributing the Sorillus RAT across Europe, leveraging legitimate platforms like OneDrive and Ngrok for stealthy delivery.

XDSpy Resurfaces: Stealthy Cyber-Espionage Campaign Targets Governments with Obscure Windows LNK Flaw XDSPY
  • Cyber Security

XDSpy Resurfaces: Stealthy Cyber-Espionage Campaign Targets Governments with Obscure Windows LNK Flaw

Do Son June 19, 2025 0

XDSpy, a covert cyber-espionage group, is back with a sophisticated campaign targeting governments, leveraging an obscure Windows LNK file parsing flaw and new XDigo malware

Halo Security Honored with 2025 MSP Today Product of the Year Award halo-security-msp-today_1750188136PpIMWQWEM7
  • Press Release

Halo Security Honored with 2025 MSP Today Product of the Year Award

cybernewswire June 18, 2025 0
Miami, Florida, 18th June 2025, CyberNewsWire
Read More Read more about Halo Security Honored with 2025 MSP Today Product of the Year Award
TikTok Gets Another Lifeline: Trump Extends Ban Deadline by 90 Days TikTok USDS Joint Venture LLC divestiture, Project Texas 2.0 ByteDance stake TikTokRefugee TikTok Ban, US Extension
  • Technology

TikTok Gets Another Lifeline: Trump Extends Ban Deadline by 90 Days

Do Son June 18, 2025 0

The Trump administration has granted TikTok another 90-day extension, allowing more time for a sale to a US buyer and keeping the app from being banned

Python Protobuf Flaw Allows DoS Via Nested Messages Python Protobuf, DoS Vulnerability
  • Vulnerability

Python Protobuf Flaw Allows DoS Via Nested Messages

Do Son June 18, 2025 0

A high-severity flaw (CVE-2025-4565) in Google's pure-Python Protobuf backend allows unauthenticated attackers to crash applications via crafted nested messages.

D-Link Router Flaws Allow Code Execution, PoC Available, No Patch D-Link DIR-816, Critical Vulnerabilities D-Link EOL RCE, Unauthenticated Command Injection
  • Vulnerability

D-Link Router Flaws Allow Code Execution, PoC Available, No Patch

Do Son June 18, 2025 0

Two critical buffer overflow flaws in D-Link router allow remote code execution. PoC available, no patch will be issued.

Broadcom Unveils VMware Cloud Foundation 9.0: A Unified Private Cloud for AI & Modern Workloads Broadcom VCF, Private Cloud
  • Technology

Broadcom Unveils VMware Cloud Foundation 9.0: A Unified Private Cloud for AI & Modern Workloads

Do Son June 18, 2025 0

Broadcom launches VMware Cloud Foundation 9.0, a unified platform for secure, managed private cloud, accelerating AI infrastructure and supporting modern workloads across environments.

Wi-Fi 8 is Coming: Ultra-Reliable Connectivity Set for 2028 Launch EU 6GHz Spectrum Wi-Fi 7 vs 6G Wi-Fi 8, Wireless Standard Captive portal - WPA3 Security
  • Technology

Wi-Fi 8 is Coming: Ultra-Reliable Connectivity Set for 2028 Launch

Do Son June 18, 2025 0

The Wi-Fi Alliance is developing Wi-Fi 8 (802.11bn) for a 2028 release, focusing on ultra-reliable performance, throughput efficiency, and coordinated multi-AP operation.

OneDrive Shock: User Loses 30 Years of Photos After Account Suspension, Highlighting Cloud Backup Risks OneDrive cloud deletion 2026 OneDrive Facial Recognition, Three-Time Limit OneDrive Suspension, Data Loss
  • Technology

OneDrive Shock: User Loses 30 Years of Photos After Account Suspension, Highlighting Cloud Backup Risks

Do Son June 18, 2025 0

A Reddit user lost 30 years of data after their OneDrive account was suspended, underscoring the critical need for multiple backup solutions beyond single cloud reliance.

Mastodon Cracks Down: New Terms Ban Unauthorized AI Data Scraping Mastodon Data, AI Scraping CVE-2024-23832 PoC
  • Technology

Mastodon Cracks Down: New Terms Ban Unauthorized AI Data Scraping

Do Son June 18, 2025 0

Mastodon updates its Terms of Service, formally prohibiting unauthorized AI data scraping and LLM training, effective July 1, 2025. Other Fediverse instances may follow.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.