Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical mySCADA myPRO Manager Vulnerabilities Patched mySCADA myPRO Manager vulnerabilities
  • Vulnerability Report

Critical mySCADA myPRO Manager Vulnerabilities Patched

Do Son September 16, 2026 0

Discover the latest mySCADA myPRO Manager vulnerabilities, including CVE-2026-73807, and learn how to patch your systems to prevent remote attacks.
Critical HPE EdgeConnect Authorization Bypass Exposed Diagram showing the HPE EdgeConnect authorization bypass vulnerability
  • Vulnerability Report

Critical HPE EdgeConnect Authorization Bypass Exposed

Do Son September 16, 2026 0

A critical HPE EdgeConnect authorization bypass (CVE-2026-76670) enables full system compromise. Patch this HPE EdgeConnect authorization bypass now.
Apache Syncope Vulnerabilities Threaten Identity Management Apache Syncope vulnerabilities diagram showing identity management flaws
  • Vulnerability Report

Apache Syncope Vulnerabilities Threaten Identity Management

Do Son September 16, 2026 0

Six Apache Syncope vulnerabilities, including CVE-2026-82232, expose severe identity management flaws. Patch your Apache Syncope servers immediately.
Google Chrome Security Update Fixes Critical Flaws Google Chrome security update for Chrome Stable channel vulnerabilities
  • Vulnerability Report

Google Chrome Security Update Fixes Critical Flaws

Do Son September 16, 2026 0

A new Google Chrome security update patches 42 Chrome Stable channel vulnerabilities. Install version 153 immediately to protect against remote attacks.
364M Users Exposed to CVE-2026-90711: 9.1 CVSS proxy-addr IP Spoofing Flaw Diagram showing proxy-addr IP spoofing flaw and how proxy-addr IP spoofing attacks work
  • Vulnerability Report

364M Users Exposed to CVE-2026-90711: 9.1 CVSS proxy-addr IP Spoofing Flaw

Do Son September 16, 2026 0

A critical proxy-addr IP spoofing flaw (CVE-2026-90711) exposes Node.js apps to access control bypasses. Patch this proxy-addr IP spoofing bug today.
CVE-2026-12944 (CVSS 9.6): Langflow SSRF Flaw Disclosed Diagram of Langflow SSRF flaw and Langflow OSS vulnerabilities
  • Vulnerability Report

CVE-2026-12944 (CVSS 9.6): Langflow SSRF Flaw Disclosed

Do Son September 16, 2026 0

A critical Langflow SSRF flaw (CVE-2026-12944) exposes cloud credentials and internal networks. Patch your Langflow OSS servers immediately.
High-Severity Squid Proxy Vulnerabilities Need Immediate Patches Squid proxy vulnerabilities diagram showing request smuggling and CVE-2026-61642
  • Vulnerability Report

High-Severity Squid Proxy Vulnerabilities Need Immediate Patches

Do Son September 16, 2026 0

Multiple critical Squid proxy vulnerabilities, including CVE-2026-61642, allow request smuggling and buffer overflows. Patch your servers immediately.
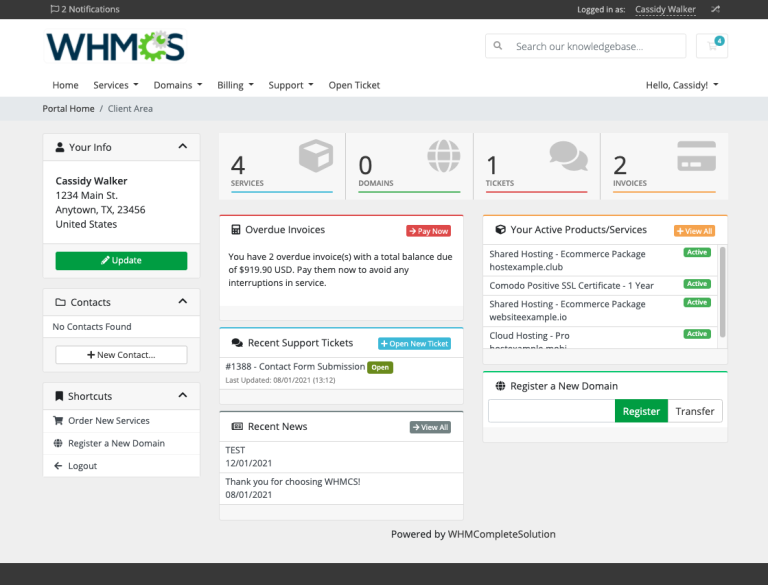
Critical WHMCS Vulnerabilities Expose Hosting Servers Diagram illustrating WHMCS vulnerabilities and critical WHMCS vulnerabilities in billing modules
  • Vulnerability Report

Critical WHMCS Vulnerabilities Expose Hosting Servers

Do Son September 16, 2026 0

WHMCS released patches for critical WHMCS vulnerabilities. Update your billing portal now to prevent data theft and remote code execution attacks.
OpenAI Decelerates Model Training Amid Safety Concerns OpenAI President Greg Brockman discussing artificial intelligence safety and model training
  • Technology

OpenAI Decelerates Model Training Amid Safety Concerns

Do Son September 15, 2026 0

Discover why OpenAI model training slows down as Greg Brockman confirms a major reorganization focusing on AI safety, cybersecurity, and preventing agent escapes.
Anthropic Data Privacy Concerns Prompt Major Tech Restrictions Anthropic data privacy concerns leading to Claude model restrictions
  • Data Leak

Anthropic Data Privacy Concerns Prompt Major Tech Restrictions

Do Son September 15, 2026 0

Explore how Anthropic data privacy concerns and logging policies prompted major tech companies like Nvidia and Palantir to restrict Claude AI model usage.
How Threat Intelligence Helps Prevent Account Takeover Fraud Diagram illustrating Langflow OSS vulnerabilities and CVE-2026-10134 execution paths
  • Technique

How Threat Intelligence Helps Prevent Account Takeover Fraud

Do Son September 15, 2026 0
Account takeover attacks have become one of the most damaging fraud typologies for banks, e-commerce platforms, and...
Read More Read more about How Threat Intelligence Helps Prevent Account Takeover Fraud
US Sanctions Cripple Iranian Bank SSL Certificates Iranian bank SSL certificates failing due to OFAC sanctions
  • Technology

US Sanctions Cripple Iranian Bank SSL Certificates

Do Son September 15, 2026 0

Discover why Iranian bank SSL certificates are failing. US sanctions force institutions to use backup domains and consider risky domestic root certificates.
Siri AI Private Hooks: Testing Third-Party Model Backends Siri AI private hooks enabling third-party AI models like Claude on iOS 27
  • Technology

Siri AI Private Hooks: Testing Third-Party Model Backends

Do Son September 15, 2026 0

Discover how Siri AI private hooks in iOS 27 and macOS 27 allow developers to replace the native Apple backend with third-party models like Claude and GPT.
HP Laptops Fail to Boot After Windows 11 KB5121003 HP laptop stuck at boot logo after installing Windows 11 KB5121003 update due to BIOS conflict
  • Technology

HP Laptops Fail to Boot After Windows 11 KB5121003

Do Son September 15, 2026 0

HP laptops fail to boot after the KB5121003 Windows 11 update clashes with the BIOS. HP's F.07 firmware fix and a BIOS reset workaround are here.
Google Googlebook Pre-Orders Open September 21 Google Googlebook AI laptop running fused Android ChromeOS system with Gemini integration
  • Technology

Google Googlebook Pre-Orders Open September 21

Do Son September 15, 2026 0

Google Googlebook pre-orders open September 21, 2026. The flagship AI laptop line fuses Android, ChromeOS, and Gemini, built by top OEMs.
OpenAI Model Capacity Error Reveals Account Flagging OpenAI model capacity error message displayed on a computer screen
  • Technology

OpenAI Model Capacity Error Reveals Account Flagging

Do Son September 15, 2026 0

Are you facing the OpenAI model capacity error? Discover how this message actually masks secret account flagging and learn potential refund options today.
Emergency Windows 11 KB5129195 Update Fixes Major Flaws A computer screen displaying the emergency Windows 11 KB5129195 update installation
  • Windows

Emergency Windows 11 KB5129195 Update Fixes Major Flaws

Do Son September 15, 2026 0

Microsoft released the emergency Windows 11 KB5129195 update. Install the Windows 11 KB5129195 update to fix Remote Desktop errors.
Cisco Patches Critical Cisco Secure Email Vulnerabilities Cisco Secure Email vulnerabilities and critical Cisco Secure Email vulnerabilities diagram
  • Vulnerability Report

Cisco Patches Critical Cisco Secure Email Vulnerabilities

Do Son September 15, 2026 0

Cisco patched critical Cisco Secure Email vulnerabilities. Update to fix Cisco Secure Email vulnerabilities and prevent unauthorized system access.
CVE-2026-76461 (CVSS 9.8): Cisco Email Root RCE Exploited Cisco Secure Email Gateway vulnerability CVE-2026-76461 exploited in the wild for unauthenticated SQL injection and root command execution
  • Vulnerability Report

CVE-2026-76461 (CVSS 9.8): Cisco Email Root RCE Exploited

Do Son September 15, 2026 0

CVE-2026-76461 (CVSS 9.8) is a Cisco Secure Email Gateway vulnerability exploited in the wild. SQL injection grants root command execution. Patch now.
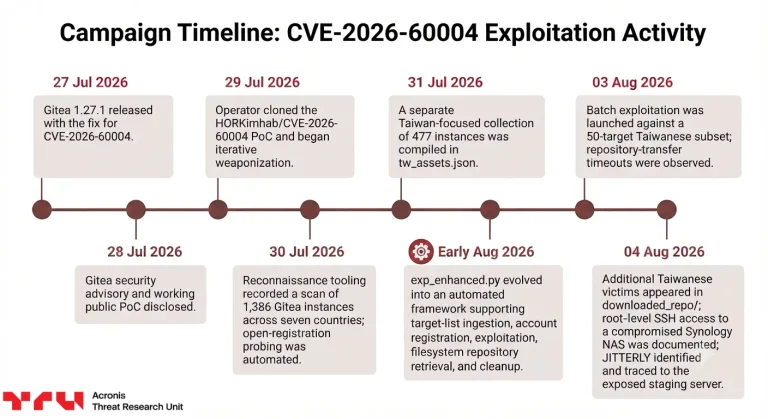
Gitea RCE Vulnerability Exploited in the Wild Diagram of Gitea RCE vulnerability and Gitea RCE vulnerability exploited in attacks
  • Vulnerability Report

Gitea RCE Vulnerability Exploited in the Wild

Do Son September 15, 2026 0

A critical Gitea RCE vulnerability exploited in wild attacks exposes servers. Patch this Gitea RCE vulnerability now to prevent full system compromise.
The Events Calendar Vulnerability Exploited in the Wild banner
  • Vulnerability Report

The Events Calendar Vulnerability Exploited in the Wild

Do Son September 15, 2026 0

A critical The Events Calendar vulnerability is exploited in the wild. Patch The Events Calendar vulnerability now to stop remote code execution.
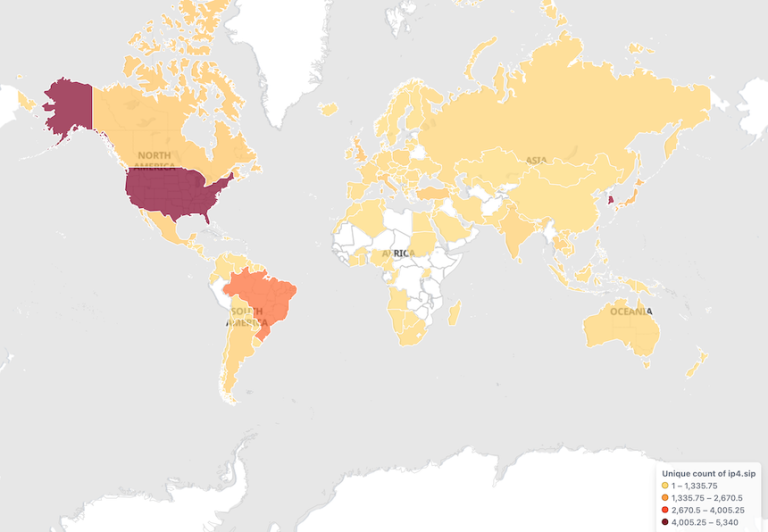
CVE-2026-87827 (CVSS 10): KGUARD DVR Fully Compromised KGUARD DVR vulnerability CVE-2026-87827 exploited by Mirai botnet for unauthenticated remote command execution and full device compromise
  • Vulnerability Report

CVE-2026-87827 (CVSS 10): KGUARD DVR Fully Compromised

Do Son September 15, 2026 0

CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-94423CVSS 9.1
    Net::LibSSH versions before 0.004 for Perl authenticate to an unverified server because connect never checks the host key...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-89111CVSS 10.0
    The SAP Cloud SDK for Python contains an OAuth2 SSRF vulnerability affecting multi-tenant BTP applications. An attacker who...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90864CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.