 Do Son
Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.
Discover Microsoft's unmetered intelligence vision. Learn how local AI agents on Windows 11 PCs will replace cloud reliance and token economics.
ChatGPT Images 2.5 cuts generation latency by 50%, improves transparent backgrounds and multi-turn editing, with Flare and Sunburst API models.
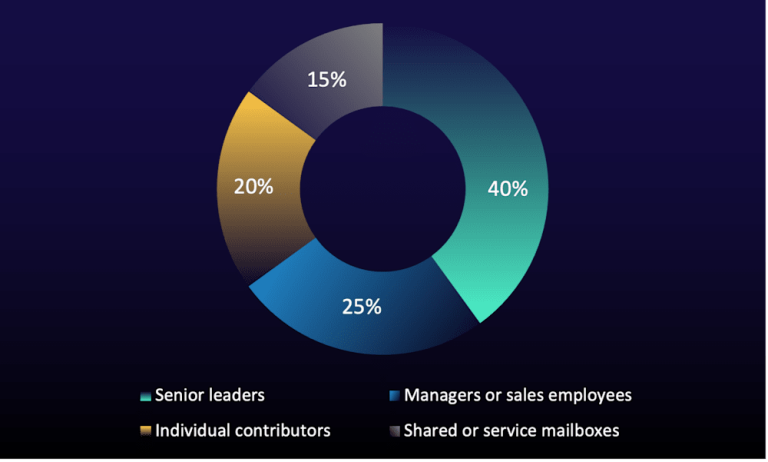
A Microsoft 365 RejectDirectSend bypass lets attackers spoof internal emails. Learn how this RejectDirectSend bypass works and how to protect your tenant.
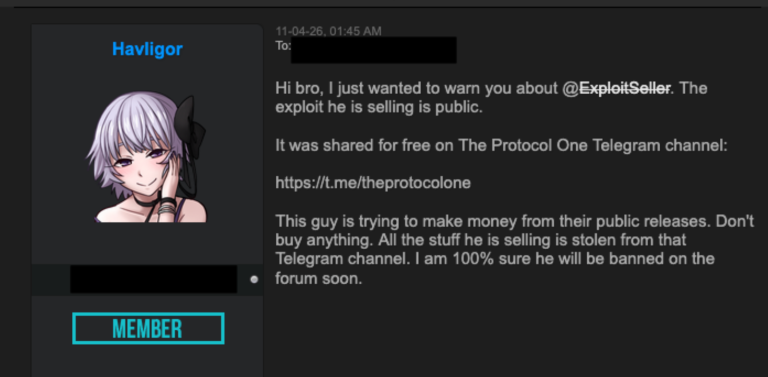
A ClickFix browser attack uses Google Sheets C2 to inject a crypto web skimmer into Chrome. See how Cisco Talos traced the theft.
Windows 11 auto dark mode switching surfaces in preview builds, with scheduled and sunrise-to-sunset options for light and dark themes.
A user can enable a passkey, protect an account with Telegram’s Two-Step Verification and still lose control...
Four Apache Impala vulnerabilities expose systems to remote code execution and authentication bypass. Upgrade to Impala 4.5.2 to secure your clusters now.
Asahi Linux M3 support reaches the mainline kernel with Wi-Fi and storage working, but GPU, Thunderbolt, and display remain in development.
Details and PoC for CVE-2026-84372 are publicly disclosed. This Predis command injection flaw via CRLF smuggling allows complete cluster compromise.
A critical MapLibre XSS vulnerability allows zero-click code execution in 2.7M weekly downloads. Discover how CVE-2026-85061 works and how to patch now.
Chrome's two-week release cycle begins with Chrome 153, doubling the pace of features and security patches while Extended Stable stays at 8 weeks.
A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
A Redis cryptomining botnet used a rogue replication attack to hijack 3,562 servers for Monero mining. See how the campaign worked.
Apache Nutch vulnerabilities include CVE-2026-41870, an unauthenticated remote code execution flaw. See affected versions and fixes.
Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.
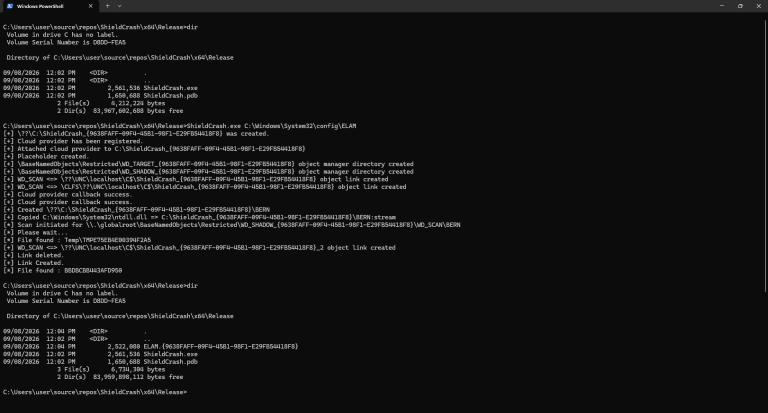
A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.
Google patched a Chrome zero-day, CVE-2026-87491, exploited in the wild. Chrome 153 fixes 230 flaws including critical WebGL bugs. Update now.

Unit 42 exposes AI-powered cyberattacks across Latin America, where LLM-assisted actors hit government, water, and financial targets.
US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.
Microsoft's September 2026 Patch Tuesday fixes two zero-day flaws, CVE-2026-81963 and CVE-2026-85880, both exploited in the wild.